 Do Son
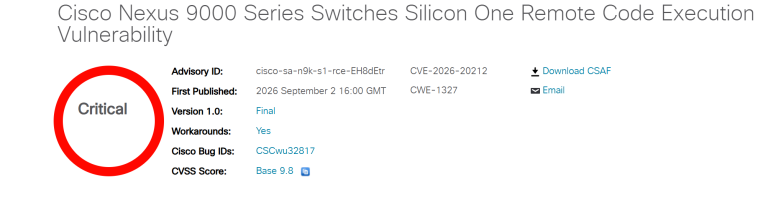
CVE-2026-20212, a critical Cisco Nexus 9000 vulnerability, lets an unauthenticated attacker gain remote code execution with root privileges. CVSS 9.8.
cisco

Cisco disclosed seven ClamAV vulnerabilities that let a remote attacker crash scanning via crafted files. Details are public. Patch now.

PoC exploit code is public for CVE-2026-20200, a Cisco IMC argument injection flaw enabling root RCE. CVSS 8.8. Patch details inside.

Cisco fixes a Cisco Catalyst Center vulnerability (CVE-2026-20191, CVSS 7.5) and seven ClamAV vulnerabilities causing DoS in Secure Endpoint Connectors.

Attackers exploit a Cisco Unified CM RCE flaw (CVE-2026-20230) in the wild. Public PoC code now details the SSRF-to-root chain. Patch now.
A threat actor exploited a Cisco SD-WAN zero-day (CVE-2026-20245) to gain root access. Learn how this attack happened and how to secure your networks.
Cisco warns CVE-2026-20262, a Cisco SD-WAN vulnerability enabling arbitrary file write, is exploited in the wild. Patch SD-WAN Manager now.
OpenAI unveils Project Daybreak, utilizing the GPT-5.5 lineage and Codex to automate vulnerability patching and Red Teaming in a direct challenge to Anthropic.
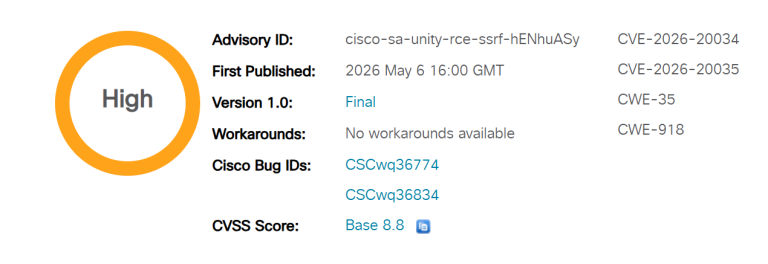
Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
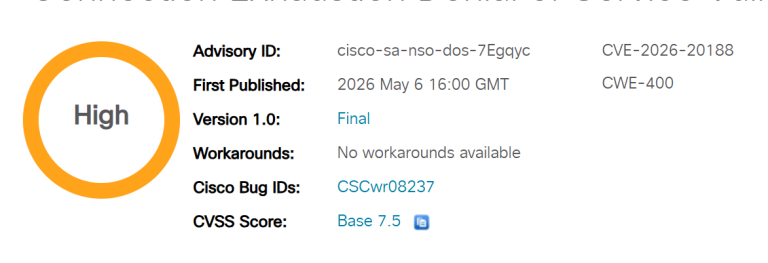
Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!
Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20093) in IMC. Unauthenticated attackers can change admin passwords and seize full control. Update now!

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20160) in SSM On-Prem. Unauthenticated attackers gain root access via exposed APIs. Update to 9-202601 now!
Cisco alerts of public flaws in IOS XE. Authenticated users can trigger a network-wide DoS or escalate privileges via the Lobby Ambassador API. Patch now.

Cisco alerts of public flaws in IOx app hosting. Unauthenticated actors can manipulate logs (CVE-2026-20113), plus a stored XSS risk (CVE-2026-20112). Patch now!
Cisco patches critical flaws: CVE-2026-20098 allows root access in Meeting Management, while malicious invites crash TelePresence units. Update now.

Cisco warns CVE-2026-20045 is being exploited. This critical RCE allows unauthenticated root access on Unified CM. Patch immediately to secure your network.
Cisco warns of a CVSS 10 zero-day (CVE-2025-20393) exploited by Chinese APT UAT-9686 to backdoor Secure Email Gateways with the Aqua malware suite.

Cisco released updates for its Desk and IP Phone series, fixing a High-severity DoS flaw (CVE-2025-20350) from buffer overflow and a Medium XSS flaw (CVE-2025-20351).

"Operation Zero Disco" exploits a critical Cisco SNMP flaw (CVE-2025-20352) to deploy Linux rootkits on switches. The malware sets a universal "disco" password and hides configuration to maintain persistence.