 Do Son
CISA KEV additions on November 10 cover six Known Exploited Vulnerabilities in Outlook, Chrome, Barracuda ESG, Cisco BroadWorks and Openwave.
CISA
CISA adds Linux kernel vulnerability CVE-2026-46300, chained with PHP2Shell for root, and VMware ESX flaw CVE-2026-41709 to KEV. Patch now.
CISA KEV catalog adds actively exploited Magento flaw CVE-2026-48356 and Brotli vulnerability CVE-2026-111497. Patch before November 10.
CISA warns of nine Kiloview E3 vulnerabilities in the NDI encoder, including CVSS 9.9 flaws CVE-2026-107861 and CVE-2026-110243. Update to V1.30.
A new StopRansomware advisory warns SafePay ransomware has hit 600+ victims via VPN logins and edge flaws. See its tactics and key defenses.
CISA warns of dcm4chee vulnerabilities that expose patient data, plus unpatched EseeCloud cameras with hard-coded credentials (CVE-2026-107617).
Fix critical openPDC openHistorian vulnerabilities like CVE-2026-100730 and CVE-2026-105281. CISA urges patching these severe RCE flaws immediately.

Chinese state hackers allegedly use Integrity Technology Group tools for botnet data theft. Protect your networks from this massive cyberespionage campaign.
CISA warned of critical Monta EV charging vulnerabilities. Learn how these Monta EV charging vulnerabilities impact stations and how to secure them.
CISA warns the Viidure dashcam app leaks hardcoded cloud credentials (CVE-2026-96587) and public storage (CVE-2026-94204). The vendor has not responded.
A critical MikroTik RouterOS vulnerability, CVE-2026-84411 (CVSS 9.8), lets unauthenticated attackers run code as root. Update RouterOS now.
CISA added two exploited CISA KEV vulnerabilities to its catalog. Patch WSO2 and Adobe Commerce to secure systems against active attacks.
US agencies warn of malicious AI distillation campaigns. New data shows systematic extraction of US frontier AI models.
CISA added critical CISA KEV vulnerabilities to its list. Patch these CISA KEV vulnerabilities now to block ongoing cyberattacks.
Critical Ebyte NA111-M vulnerabilities like CVE-2026-73125 could allow attackers to fully compromise the device. Review CISA guidance and mitigations.
CISA warns that Xiiaozet LK100W vulnerabilities, including CVE-2026-78239, allow attackers to take full control of affected devices. Update now.
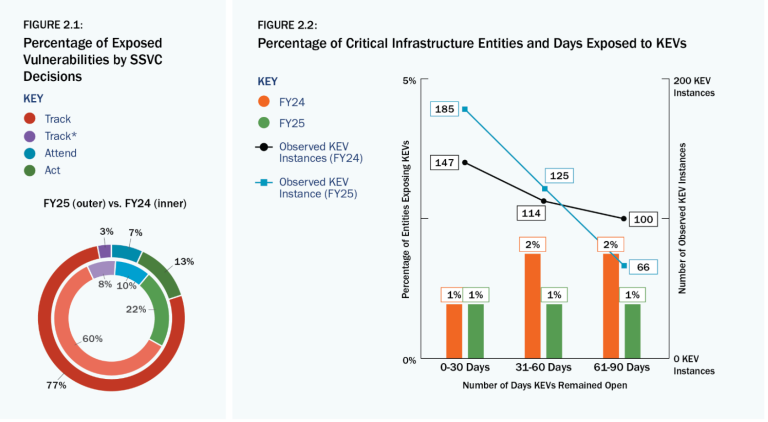
The CISA Vulnerability Review finds known exploited vulnerabilities and decades-old software flaws drive most compromises across FY2024 and FY2025.

CISA and the NSA warn of an active Siemens PLC cyber threat using AI-generated exploit scripts disguised as monitoring tools. Protect your OT now.
CISA and five agencies warn that Gunra ransomware is hitting critical infrastructure with double extortion. A Linux flaw may let victims recover free.

CVE-2026-68067 (CVSS 9.8) lets attackers control user accounts on the Mira Hormone Monitor by bypassing the cloud login. Eight flaws total.
CVE-2026-16347 lets attackers brute-force MikroTik RouterOS logins for unauthorized system access. Rated CVSS 8.8, with no fix yet. Apply mitigations.
CVE-2026-61884 is a Tycon authentication bypass rated CVSS 9.8 in TPDIN-Monitor-WEB2. No vendor fix exists, so isolate the devices now.