
 Do Son
Sekoia details PolarEdge, a Rust-based backdoor using a custom mbedTLS server for C2 on Cisco, QNAP, and Synology devices. The backdoor uses XOR 0x11 for config obfuscation and attempts to delete system utilities to block rivals.
cisco

Rapid7 exposed the unauthenticated RCE chain in Cisco ASA/FTD. CVE-2025-20362 bypasses auth to reach CVE-2025-20333, a buffer overflow in the WebVPN Lua script. Patch immediately.

The "Trinity of Chaos" alliance (Lapsus$, Scattered Spider, ShinyHunters) launched a DLS, listing 39 firms, including Google and Cisco, and claiming 1.5 billion stolen records.

Cisco patches a Critical 9.9 zero-day (CVE-2025-20333) in ASA/FTD VPN web servers. Authenticated attackers can exploit the flaw for root-level Remote Code Execution.
Cisco disclosed a Critical RCE flaw in its Firewall ASA/FTD, IOS, IOS XE, and IOS XR web services. Unauthenticated attackers can gain root access.

Cisco patches CVE-2025-20362, a medium-high zero-day vulnerability in ASA/FTD VPN web servers that is being exploited to gain unauthorized access to restricted resources.

A critical SNMP flaw (CVE-2025-20352) in Cisco IOS/IOS XE is being actively exploited, allowing attackers root access. Urgent patching and mitigation required!

A new GreyNoise report warns of two massive scanning spikes targeting Cisco ASA devices, raising concerns that attackers may be preparing to exploit a new vulnerability.
Cisco has issued a security advisory for a high-severity DoS vulnerability (CVE-2025-20241) in its Nexus switches that could allow an unauthenticated attacker to crash a device.
A new report from Cisco Talos exposes Static Tundra, a Russian state-sponsored group that has exploited unpatched Cisco devices for over a decade.
A critical vulnerability (CVE-2025-20265) in Cisco Secure Firewall Management Center allows unauthenticated attackers to execute commands with high privilege.

Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
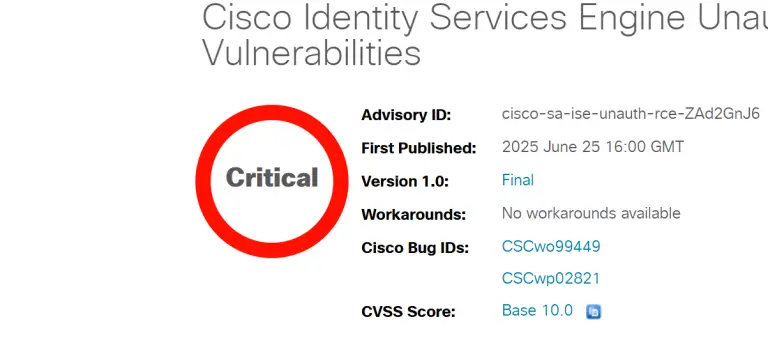
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.

Cisco ClamAV versions 1.4.3 and 1.0.9 fix critical flaws: CVE-2025-20260 (CVSS 9.8) in PDF scanning could allow RCE, and CVE-2025-20234 (UDF) leads to DoS.
Cisco warns of a critical flaw (CVE-2025-20271, CVSS 8.6) in Meraki MX/Z Series devices, allowing unauthenticated remote DoS on AnyConnect VPN. Update firmware now!

Cisco issues advisories for high-severity flaws (CVSS 8.8, 8.7) in IMC and NDFC, risking privilege escalation and device impersonation. Patch immediately!

A critical Cisco IOS XE WLC flaw (CVE-2025-20188, CVSS 10) allows unauthenticated RCE via arbitrary file uploads. Update or disable Out-of-Band AP Image Download.
Cisco patches two privilege escalation flaws in Unified Intelligence Center that could expose sensitive data. Users urged to upgrade immediately.

Cisco patches CVE-2025-20188, a CVSS 10 flaw in IOS XE WLCs, enabling unauthenticated remote file uploads and root-level command execution.

Critical RCE vulnerability (CVE-2025-32433) in Erlang/OTP affects Cisco products. Unauthenticated attackers can execute code remotely. Patch now!

Cisco patches CVE-2025-20236, an RCE flaw in Webex App exploitable via crafted links. Users urged to update to avoid command execution risks.
Research reveals Cisco CVE-2018-0171, a 7-year-old Smart Install RCE vulnerability, remains active, exposing over 1,200 devices. Learn how attackers exploit it and how to protect your network.