
 Do Son
The CVE-2023-20105 vulnerability resides within the change password functionality of the Cisco Expressway Series and Cisco TelePresence VCS
cisco

CVE-2023-20159 vulnerability stems from a security hole in the web-based user interface of the Cisco Small Business Series Switches.

CVE-2023-20126 affects Cisco SPA112 2-Port Phone Adapters and allows an attacker to execute arbitrary code on affected devices.

Attackers can exploit the CVE-2023-20046 vulnerability by sending a valid low-privileged SSH key to an affected device from a host configured

CVE-2023-20036 is present in the web UI of Cisco IND and allows an authenticated, remote attacker to execute arbitrary commands

The CVE-2023-20117 & CVE-2023-20128 vulnerabilities found in the web-based management interface of Cisco RV320 and RV325 VPN Routers

CVE-2023-20102 (CVSS score of 8.8) could allow an authenticated, remote attacker to execute arbitrary code on the underlying OS

CVE-2023-20078 in the web-based management interface of Cisco IP Phone allow attackers to execute arbitrary commands with root privileges

an authenticated attacker could exploit the CVE-2023-20009 vulnerability to execute arbitrary commands as root.

CVE-2023-20076 (CVSS score of 7.2) exists because of incomplete sanitization of parameters passed in for activation of an application
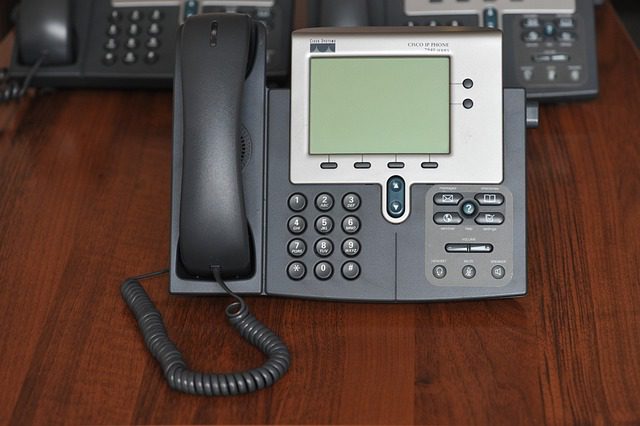
an attacker could exploit CVE-2023-20018 (CVSS score of 8.6) to access certain restricted parts of the web interface.
CVE-2023-20025 (CVSS score: 9.0), has been described as an authentication bypass vulnerability in Cisco Small Business RV016, RV042, RV042G, RV082

CVE-2022-20961 (CVSS score: 8.8) was caused by insufficient CSRF protections for the web-based management interface of an affected device

By sending a specially crafted HTTP request, an attacker could exploit CVE-2022-20958 to execute arbitrary code on the system

An attacker could exploit CVE-2022-20853 to perform cross-site scripting attacks, Web cache poisoning, and other malicious activities.

The CVE-2022-20696 hole can impact several Cisco products if they are running a Cisco SD-WAN vManage Software prior to 20.9.1.

Cisco has addressed a high severity privilege escalation vulnerability (CVE-2022-20921) found in the API implementation of the Cisco MSO

Discovery Protocol is enabled by default globally and on all interfaces in FXOS and NX-OS, CVE-2022-20824 impacts numerous products
On March 28, 2018, Cisco has released several updates to address vulnerabilities affecting Cisco IOS XE Software. A...
Cisco‘s latest report shows that the rapid growth of cloud applications will lead to an explosion of...

On January 10, 2018, Cisco officially released its Encrypted Traffic Analysis (ETA) software platform to examine network...