 Do Son
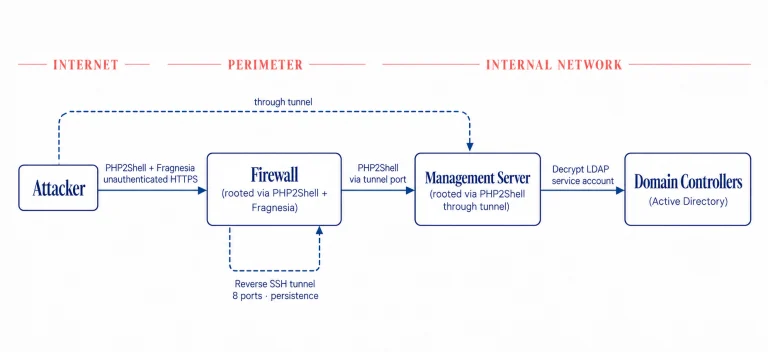
Dream researchers uncovered a Chinese-nexus PHP2Shell exploit Fragnesia chain that rooted 25 firewalls and breached a US government Active Directory.
active directory
A devastating GMO Desktop Cloud breach compromised over 26,000 servers, exposing FX trading accounts and prompting a full infrastructure shutdown.
UTA0576 chained an Ivanti Connect Secure zero-day, CVE-2026-104935, with a root exploit to steal AD credentials. Patch now and check memory.

Attackers used a PaperCut zero-day to plant a web shell and an AdaptixC2 implant hidden in fake Microsoft Copilot, then took over Active Directory.

An active SonicWall SMA 1000 campaign breached a UK council. Learn how the SonicWall SMA 1000 campaign exposed Active Directory records worldwide.

Details and PoC for CVE-2026-27912 (ResetNightmare) are public. This Kerberos flaw lets attackers reset AD passwords and gain SYSTEM.

Certighost AD CS vulnerability details and PoC code for CVE-2026-54121 are public. The flaw let a low-privileged user impersonate a Domain Controller.

VMRay Labs details Operation STANDOFF, a Russian-speaking threat group running malware, a proxy-botnet and AI influence tools behind fake GitHub traffic.

ManageEngine fixed an ADAudit Plus vulnerability, CVE-2026-6516, a CVSS 10 unauthenticated remote code execution flaw. Update to build 8606 now.
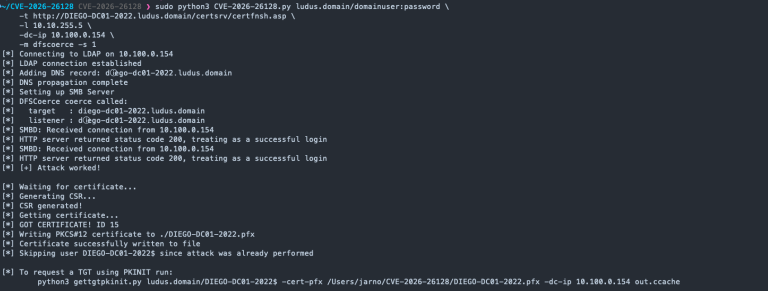
Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.
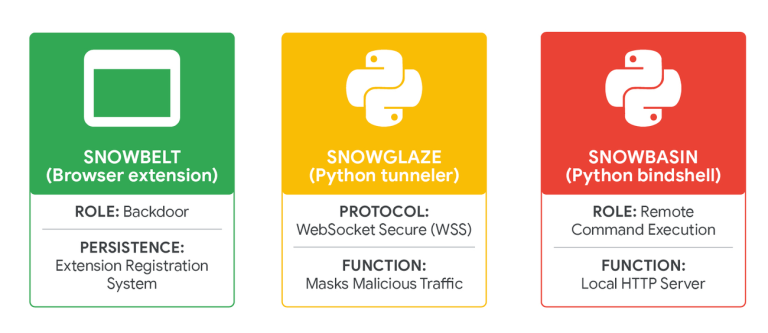
UNC6692 uses MS Teams impersonation to deploy the SNOW suite. Learn how "living off the cloud" bypasses reputation filters to hijack Active Directory.

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.

SentinelOne DFIR reveals how attackers exploit FortiGate NGFW flaws to extract credentials, abuse Active Directory, and establish persistent network access.
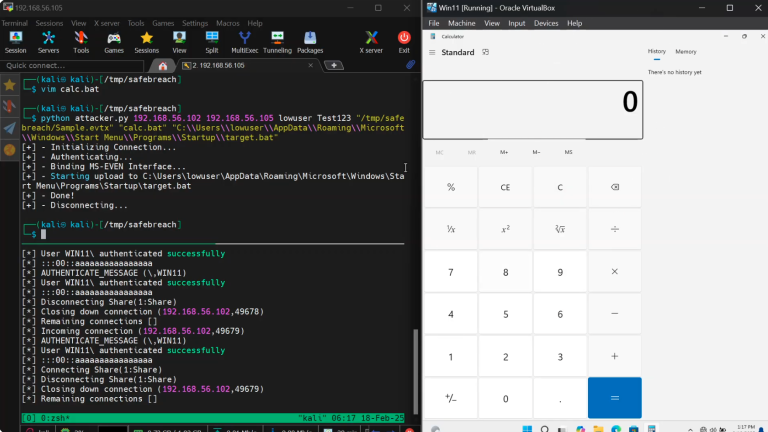
SafeBreach Labs releases PoC exploit code for EventLogin (CVE-2025-29969), a TOCTOU flaw in Windows MS-EVEN RPC allowing remote file writes. Patch now.

Critical ASUSTOR ADM flaw CVE-2026-24936 (CVSS 9.5) allows remote file overwrite. Unauthenticated attackers can seize NAS control. Update to v5.1.2 now.

ManageEngine patches critical ADSelfService Plus flaw CVE-2025-11250 (CVSS 9.1). Update to Build 6519 immediately to secure your Active Directory.

Fortinet warns of active exploits for CVE-2020-12812, where attackers bypass 2FA on FortiGate firewalls by simply changing username capitalization.

A flaw (CVE-2025-58726) allows SYSTEM privilege escalation via Kerberos authentication reflection using "Ghost SPNs" and disabled SMB signing. Patch immediately.

Samba released an urgent fix for a Critical (CVSS 10.0) RCE flaw (CVE-2025-10230) allowing unauthenticated command injection on AD DCs when the WINS hook is enabled. Update to 4.23.2.

A new Active Directory flaw, BadSuccessor, allows low-privileged users to become Domain Admins. Akamai researchers warn that the technique remains a threat even after patching.
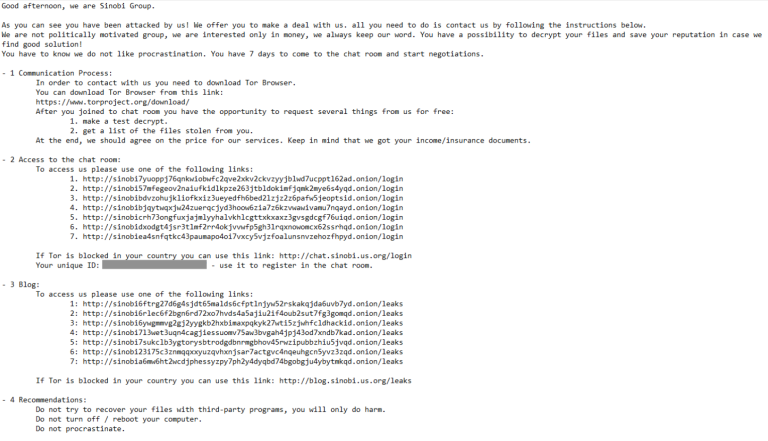
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.

SafeBreach Labs reveals Win-DDoS, a new DoS technique that weaponizes Windows domain controllers to launch large-scale attacks, exploiting flaws patched by Microsoft.