 Do Son
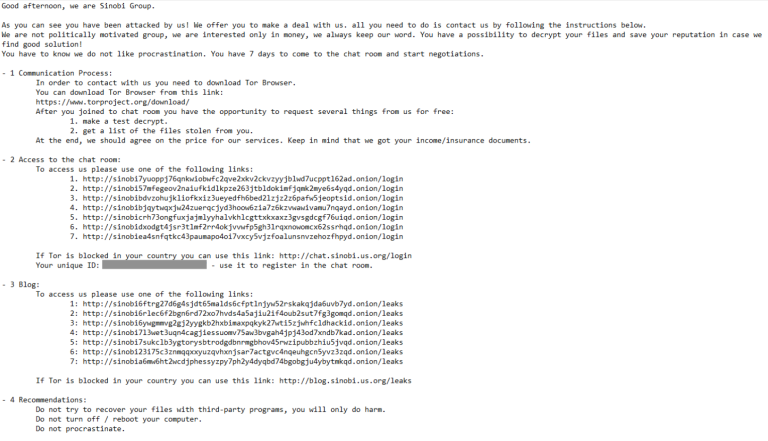
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.
active directory

SafeBreach Labs reveals Win-DDoS, a new DoS technique that weaponizes Windows domain controllers to launch large-scale attacks, exploiting flaws patched by Microsoft.

A new "EPM Poisoning" attack technique exploits a Windows RPC flaw (CVE-2025-49760) to hijack services, enabling unprivileged users to steal machine credentials and compromise Active Directory.
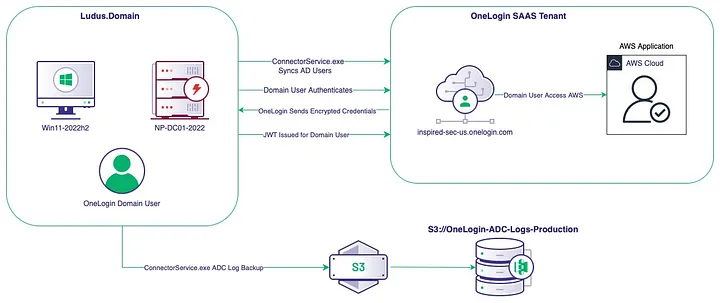
A critical flaw in OneLogin's AD Connector exposed API keys, allowing attackers to impersonate users across organizations via unclaimed S3 buckets and forged JWT tokens.

A spoofing flaw (CVE-2025-26685) in Microsoft Defender for Identity, combined with other vulnerabilities, enables unauthenticated privilege escalation to Active Directory.

Zero-day CVE-2025-33073 allows remote privilege escalation to SYSTEM on Windows via SMB. PoC available. Fixed in June 10, 2025 Patch Tuesday.
Weaponizing Group Policy: Custom Client-Side Extensions as a Stealthy Backdoor into Active Directory

Weaponizing Group Policy: Custom Client-Side Extensions as a Stealthy Backdoor into Active Directory
A new, stealthy AD persistence technique abuses custom Group Policy Client-Side Extensions (CSEs) for SYSTEM-level access. Learn how to detect it!

Exploit BadSuccessor to take over domains with PoC code. No patch, full AD compromise via dMSAs in Windows Server 2025.
Protect your organization from Kerberoasting attacks. Learn how to defend against this growing threat to Active Directory.

Protect your Zyxel security appliances from malicious activity. Stay up-to-date with firmware updates and secure your network against unauthorized access.

Akira ransomware group exemplifies the evolving nature of cyber threats. Their ability to adapt tactics, from encryption-based ransomware