 Do Son
An attacker targeted GitLab vulnerability CVE-2026-97229 (CVSS 10 RCE) on Alpine Linux's server. Alpine rebuilt GitLab and reset all passwords.
gitlab
Ruby security update 4.0.9, 3.4.12 and 3.3.13 fixes Onigmo regex bugs behind GitLab RCE flaws CVE-2026-110264 and CVE-2026-97229. Upgrade now.
Apply the GitLab critical patch release to fix 12 GitLab vulnerabilities, including 10.0 CVSS RCE flaw CVE-2026-110264 and CVE-2026-15723.
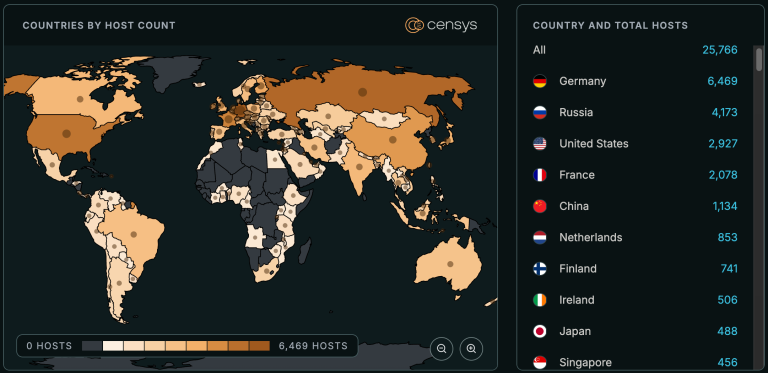
Technical details and PoC exploit code for CVE-2026-97229, a CVSS 10.0 GitLab RCE vulnerability exposing 25,766 hosts, are now public. Patch to 19.4.2 now.
A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.
GitLab AI Gateway vulnerability CVE-2026-90970 (CVSS 9.9) lets Duo Agent Platform users run commands. Upgrade self-hosted gateways now.
A GitLab critical patch release addresses two CVEs enabling a GitLab RCE vulnerability. Update your CI/CD pipelines to prevent arbitrary code execution.
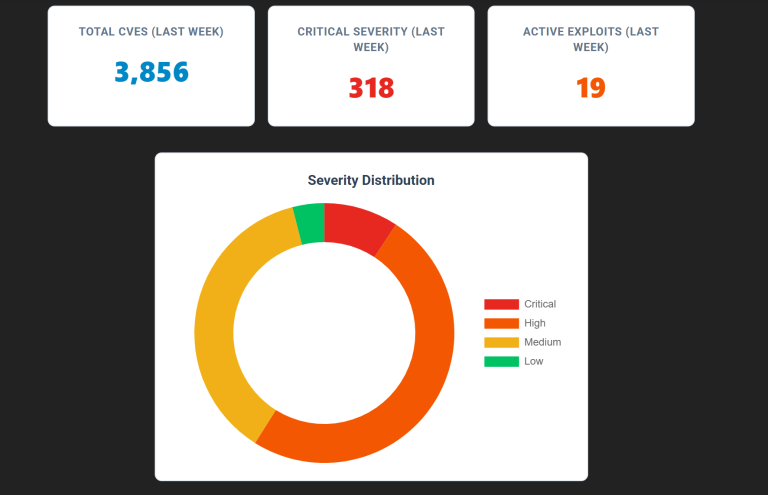
Our weekly CVE report tracked 3,856 new CVEs and 19 exploited vulnerabilities. See which reached CISA KEV and which stayed exclusive to DC.

GitLab patched critical GitLab vulnerabilities, led by CVE-2026-85706 with a CVSS 10.0 score. Update your server now to protect source code from exposure.
A critical GnuTLS token leak via a GitLab CI artifact exposure put major Linux distributions at risk. Learn how this supply chain vulnerability occurred.
A critical GitLab EE security patch addresses CVE-2026-18252, fixing a command execution flaw. Learn about affected versions, mechanisms, and mitigation.
GitLab CVE-2026-19478 vulnerability lets unauthenticated attackers delete public projects. Exploited in the wild with public PoC. Patch now.
GitLab patched CVE-2026-19478, a CVSS 9.4 GraphQL code injection flaw letting unauthenticated users alter or delete project data. Update now.
The new GitLab patch release fixes 13 flaws, including high-severity XSS and authorization bugs. Update to 19.2.2, 19.1.4, or 19.0.6 now.
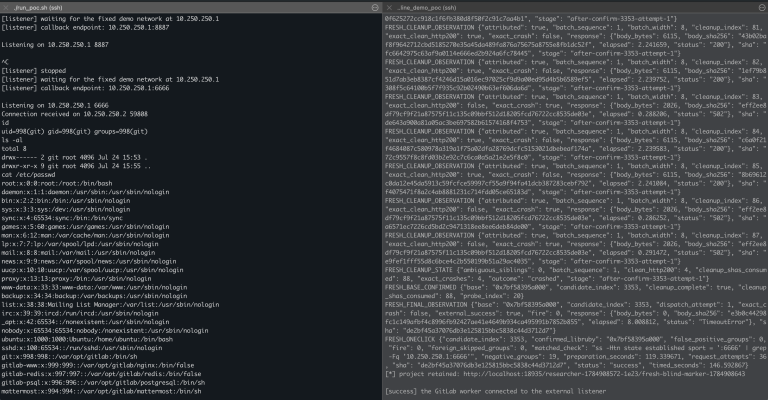
Public PoC exploits a GitLab RCE built from two Oj memory corruption bugs. See affected versions and patched GitLab releases to install now.
The latest GitLab patch release fixes 13 vulnerabilities, including CVE-2026-6267, a high-severity data exposure flaw. Update self-managed GitLab now.
GitLab released critical security updates addressing 13 vulnerabilities, including severe cross-site scripting and information disclosure flaws.

Discover the latest GitLab security updates in patch release 19.0.2. Protect your self-managed servers from critical vulnerabilities like CVE-2026-6552.
GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!
GitLab fixes high-severity GraphQL CSRF and Web IDE vulnerabilities in versions 18.11.1, 18.10.4, and 18.9.6. Protect your sessions and projects—patch now!

GitLab releases critical patches (18.10.3+) for WebSocket flaws, Terraform DoS, and unauthorized privilege demotions. Update your self-managed instances!

GitLab has released a critical security advisory alongside versions 18.10.1, 18.9.3, and 18.8.7 for its Community (CE)...