 Do Son
The November 2026 Android security update fixes 216 flaws, including zero-click remote code execution bugs CVE-2026-58868 and CVE-2026-58936.
android
The Android SMS of Death flaw crashes telephony services via malformed WAP Push messages, triggering persistent bootloops without user interaction.
The Google Registered App Stores program brings seamless one-click app installs and background updates to verified third-party Android marketplaces.
Anthropic's AI vulnerability research found remote code execution chains in Chrome, Safari, Android, Windows and Linux. All are now fixed.
Android phone number verification now links your numbers to every Google account on the device. Here is how to turn it off.
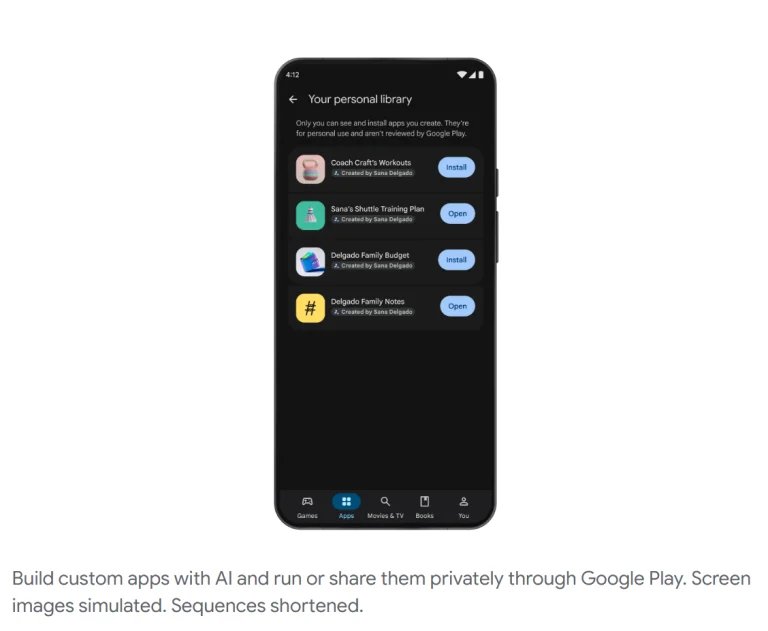
Users can now publish Google Play AI apps using a standard account. Discover how Google AI Studio and Gemini are transforming Android app development.
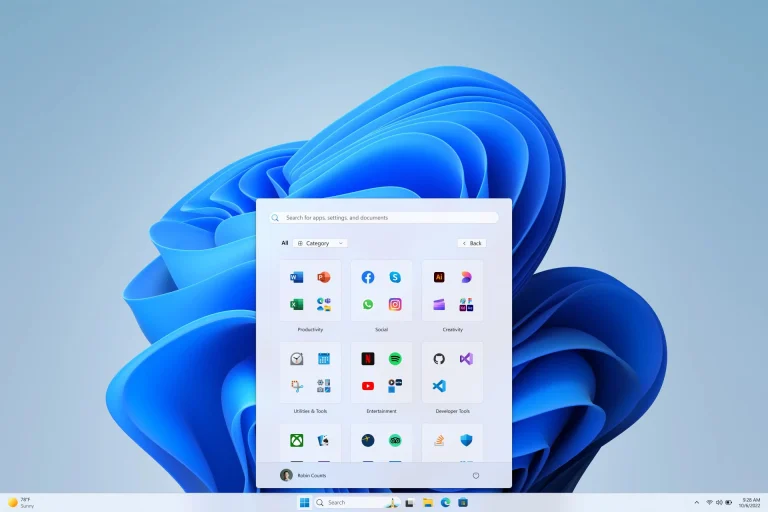
Microsoft is testing Windows 11 Quick Settings controls for Android: toggle Do Not Disturb, set volume, and ring a lost phone without Phone Link.
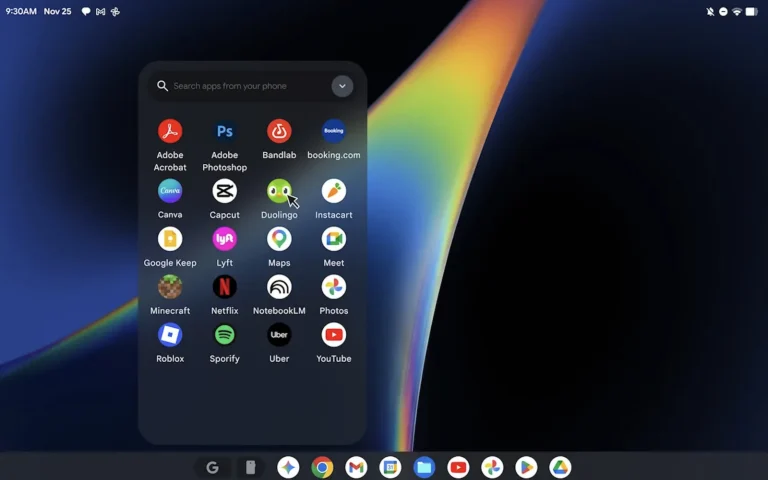
Discover how to run Googlebook OS on an Apple Silicon MacBook using QEMU virtualization, MoltenVK, and the open-source GBOS-VM project.
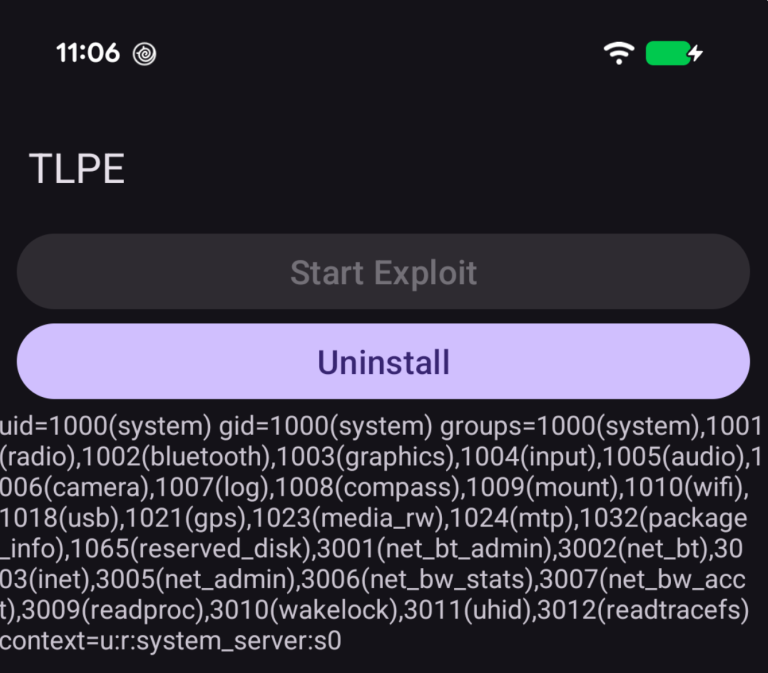
A critical Android Telecom vulnerability (CVE-2026-49881) allows remote code execution. Read the analysis and learn how to secure your device today.
A Google Pixel vulnerability exploited in targeted attacks allows privilege escalation. Update your device to patch this Google Pixel vulnerability now.
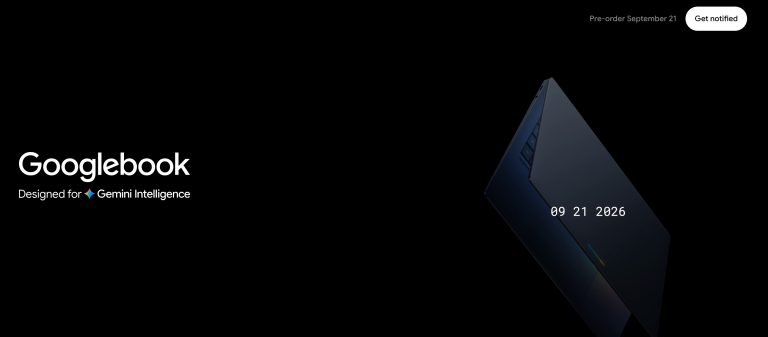
Google Googlebook pre-orders open September 21, 2026. The flagship AI laptop line fuses Android, ChromeOS, and Gemini, built by top OEMs.

Discover the new Android password manager migration feature. Learn how to securely transfer passkeys, passwords, and data between apps using FIDO standards.
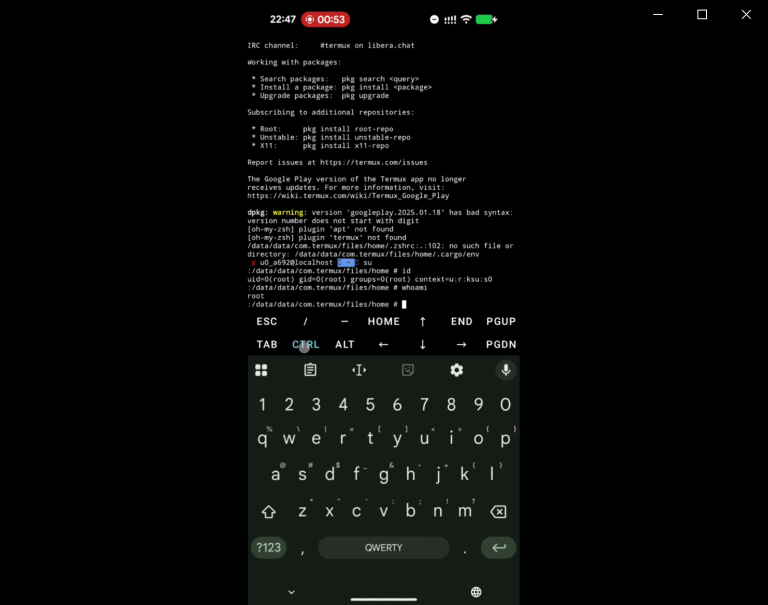
The LSPromise exploit chain provides a 100% success rate for local privilege escalation to root on Android 17. Details and PoC are publicly disclosed.
The September 2026 Android Security Bulletin patches critical RCE flaws like CVE-2026-28604 in the System component. Update to patch level 2026-09-05.

A public PoC for CVE-2026-0075 exposes an Android elevation of privilege in ContactsProvider2 with no user interaction. Details are now disclosed.

Google has quietly replaced public Git access to Pixel kernel source code with a manual application process, slowing custom ROM development, GrapheneOS reports.

Palo Alto Networks analyzed Kimwolf botnet malware. Read our Kimwolf botnet malware analysis to learn how it attacks Android TV boxes.

PoC exploit code is public for CVE-2026-64560, a Linux kernel CPU timer flaw that gives a root shell on Pixel 10 Pro. CVSS 7.0. Details inside.

PoC exploit code is public for CVE-2026-43074, a Linux kernel eventpoll flaw that gives a root shell on Pixel 10 Pro. CVSS 7.3. Details inside.

Google announced the imminent Google Assistant shutdown on mobile devices starting September 4, mandating the transition to the generative Gemini AI platform.

Qualcomm notifies clients of double-digit chip price hikes starting September 2026, impacting Android smartphones and wearable technology.