
 Do Son
Robin's proof-of-concept (PoC) exploit demonstrates CVE-2024-53675 by hosting a malicious DTD file and sending a crafted payload
PoC

Explore CVE-2024-12084 PoC and learn about critical vulnerabilities in Rsync that could enable remote code execution and data leaks.

Learn about CVE-2025-21420, a critical vulnerability in the Windows Disk Cleanup Tool that could allow SYSTEM privilege escalation.

A proof-of-concept (PoC) exploit for CVE-2025-0108 has been publicly released, making it easier for threat actors to target unpatched systems.

Security researcher Dhmos Funk released a PoC exploit for CVE-2025-0411 (CVSS 7.0), a high-severity vulnerability in the 7-Zip file archiver

Adding to the urgency, security researcher MrAle_98 released a proof-of-concept (PoC) exploit for CVE-2024-49138 on GitHub

Learn about the recently published technical details and PoC exploit code for CVE-2025-0107, a serious vulnerability in Palo Alto Networks' Expedition migration tool.

watchTowr Labs published a detailed analysis of the vulnerability and a proof-of-concept (PoC) exploit for CVE-2025-0282

Discover the in-depth analysis and PoC exploit code for CVE-2024-27397, a critical Linux kernel vulnerability that allows local privilege escalation.

Beware of the dangerous LDAPNightmare exploit posing as a proof-of-concept for Microsoft's CVE-2024-49113 vulnerability. Find out how attackers are distributing information-stealing malware through this fake exploit.

Protect your network from a critical vulnerability in GFI KerioControl firewalls. Find out about CVE-2024-52875 and the steps you can take to secure your devices.

Learn about the proof-of-concept (PoC) exploit for CVE-2024-21182 in Oracle WebLogic Server. Understand the risks and take action to secure your server.

A proof-of-concept (PoC) exploit for CVE-2023-4147 has been published on GitHub, increasing the urgency for patching.

With a PoC exploit already circulating and a near-perfect CVSS score, CVE-2024-45387 is a significant threat to organizations using Apache Traffic Control

Discover the details of the critical vulnerability (CVE-2024-56145) in Craft CMS that allows for unauthenticated remote code execution.

New security flaw (CVE-2024-53376) discovered in CyberPanel: understand the risks and potential server compromises. Check your version and take action.

Hackers are actively exploiting a recently fixed flaw CVE-2024-53677 in the Apache Struts after a PoC exploit was made public

Discover the critical vulnerability in the Spring Framework and the impact of CVE-2024-38819 PoC exploit on server security.
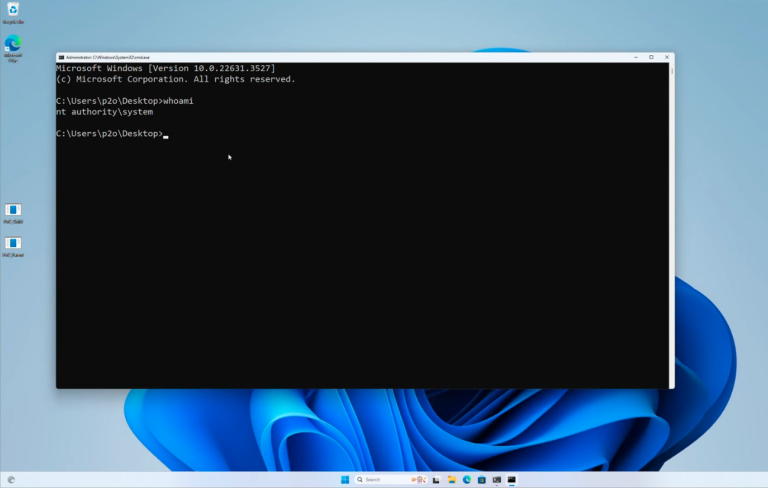
Explore the in-depth analysis of CVE-2024-38193, a critical use-after-free vulnerability in the afd.sys Windows driver. Understand the exploitation process and potential impact.

A proof-of-concept (PoC) exploit code for CVE-2024-49039, a zero-day vulnerability in Windows Task Scheduler, has been publicly released

A security researcher recently published technical details and a proof-of-concept (PoC) exploit for a critical zero-day vulnerability CVE-2024-47575

Explore the technical details of CVE-2024-9264, a critical vulnerability in Grafana that allows attackers to exploit SQL expressions feature.