 Do Son
A major MUJI credit card breach exposed 1.09 million card numbers stored in plaintext after Ryohin Keikaku failed to purge legacy loyalty data.
Data Breach
TSMC data breach confirmed: a TSMC employee data leak traced to a cloud provider. A seller claims 46,000 records and asks 3 BTC.
A massive Nitori data breach exposed up to 37.62 million personal and corporate customer records in Japan, raising severe impersonation scam risks.
The October Railway security incident exposed up to 100,000 workspaces in a targeted AI keys breach. Learn how the attack happened and what to do.
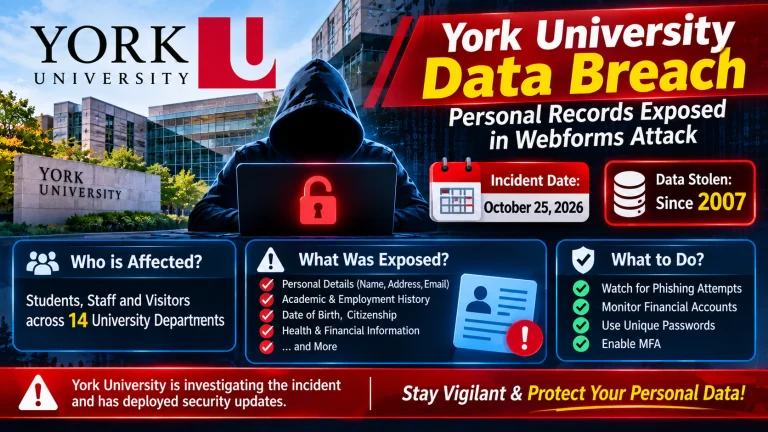
A York University data breach exposed records from 2007 to 2026 after a departmental webforms theft. Check which faculties and students are affected.
A severe DreamHost security breach exposed customer FTP credentials and webmail accounts, prompting urgent password rotations and website file audits.
An Amadeus airline data breach compromised passenger travel records across Malaysia Airlines, JAL, ANA, and Cathay Pacific via compromised credentials.
Hackers reduced the GMO Internet ransom demand from $50M to $1M and leaked victim files after the Japanese conglomerate ignored multiple bug warnings.
A devastating GMO Desktop Cloud breach compromised over 26,000 servers, exposing FX trading accounts and prompting a full infrastructure shutdown.
A Keystone wallet data breach via Shopify API exposed customer shipping addresses, raising physical wrench attack concerns for crypto holders.
A PingCAP data breach exposed customer records and source code. Learn how the TiDB Cloud security incident happened and how to protect your account.
A CAPCOM ID data breach exposed 11.77 million records, including emails and login activity. No payment data was leaked.
Quest Diagnostics data breach: hackers accessed patient records in its Quanum Lab Services Manager. Quest says it is not tied to the PHP flaw.
The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts.
A massive Sourcenext data breach exposed up to 22.5 million customer records via abused member APIs, prompting emergency company-wide password resets.
The OpenCode security breach may have exposed stored third-party API keys for 1.4% of Console users. Revoke and rotate keys now.
UpdraftPlus data breach exposed customer data and keys now used in an UpdraftCentral backdoor campaign. Update to 1.26.12 and check your sites.
CrowdStrike links the ARTEX AI tool to breaches at South Korean banks, run by a suspected Chinese-speaking, profit-driven attacker.
Trump Mobile data breach: BYOD leaks Trump Mobile customer data for 3,615 people, including Trump allies, via an infostealer and no MFA.
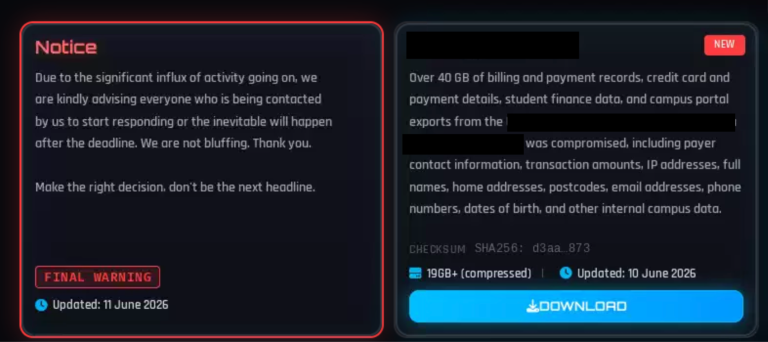
A ShinyHunters hacker arrest in Jordan may aid the FBI, as an alleged member reportedly shares devices and chats. Here is what we know.
Denmark CPR data breach: attackers abused a firm's access, leaving CPR numbers exposed for 8.8 million people. Here is what to know and do.

Discover how the ShinyHunters hacking group claims to have orchestrated a massive FBI data breach, stealing employee records via an Oracle zero-day flaw.