 Do Son
The Revolut data breach leaked passports, selfies, and crypto records of wealthy users, raising the risk of real-world wrench attacks. Details here.
Data Breach

Discover the details of the Surfshark test server breach. Learn how a configuration error exposed internal secrets and how the VPN provider responded.
The Trezor data breach at shipping partner ShipMonk exposed about 80,000 customers' order data. Wallets are safe, but phishing risk is high.
An unpatched JetBrains Cadence server exposed cloud infrastructure, AWS credentials, and critical developer secrets. Discover the details of this severe breach.
Discover the details of the massive Mercor data breach exposing 4TB of recruiting data for OpenAI, Google, Meta, and Microsoft.
Sakura Internet disclosed a breach of its customer management system affecting 1.36 million accounts, though passwords were hashed and salted and no ransom was demanded.

A SafePal data breach exposed order information for about 39,798 customers via an order-tracking flaw. Wallet funds and keys were not affected.

Discover how AI driven cyberattacks have become the most lethal weapon for hackers in 2026, increasing breach costs and targeting critical infrastructure.

The Hugging Face breach was driven end-to-end by an autonomous AI agent attack. Internal datasets and service credentials were exposed.

Discover the details of the recent KDDI data breach. Hackers stole over 12 million email addresses and millions of passwords. Learn how to protect yourself.
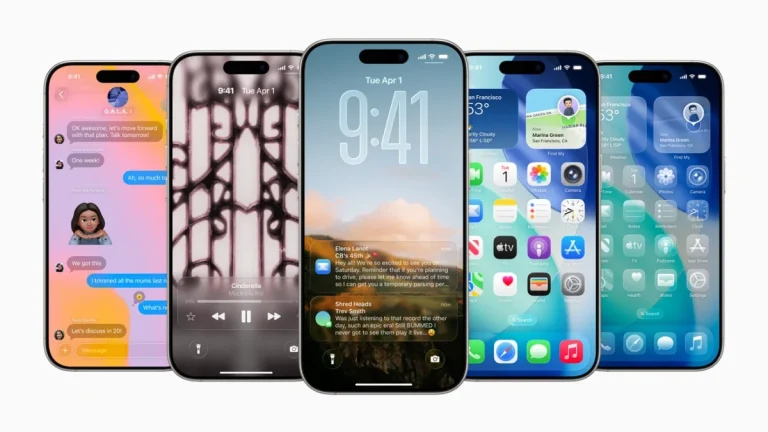
An iPhone 18 Pro leak from the Tata Electronics breach exposes supplier lists, component details, and device photos on the dark web.

LastPass confirms the Klue breach exposed customer CRM data via OAuth token theft in Salesforce. Vaults stayed safe. Here's what to know.
A Tata Electronics data breach exposed 630GB of files. Hackers claim Apple and Tesla design documents are in the stolen 200,000-file haul.

Hackers breached Novo Nordisk, stealing AI training data, model checkpoints, and pseudonymized clinical trial patient records, now held for ransom.
The Uncanny Automator breach exposed customer data and pushed a backdoored plugin build (7.3.0.5). Here's what happened and how to secure your site.

A serious Instagram account recovery flaw has been exposed. Read this Meta incident notification detailing how AI-assisted bugs bypass security.
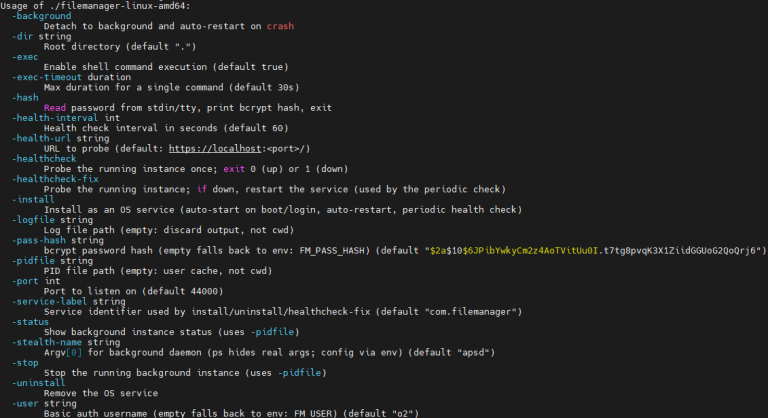
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!
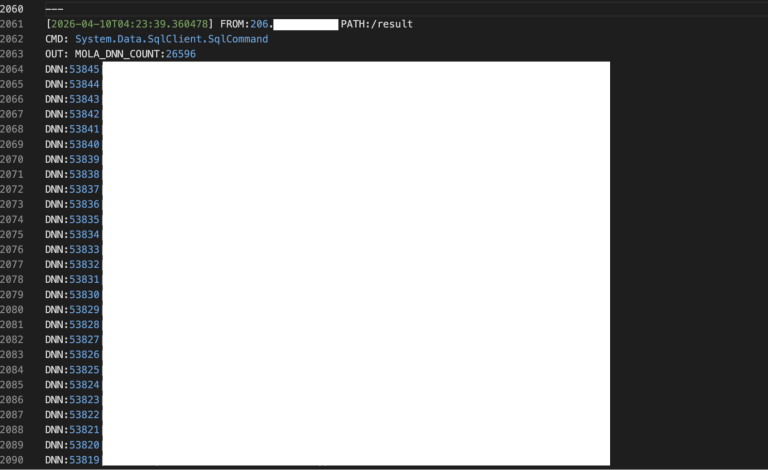
Hunt Intelligence uncovers a massive Iranian-nexus breach targeting the Omani Ministry of Justice. 26k records leaked via an unprotected UAE staging server.

Vimeo metadata and customer emails were exposed via a breach at third-party vendor Anodot. Internal systems remain secure. Learn how to manage vendor risk.

ClickUp discloses a configuration flaw exposing 893 emails and a live API token via Split.io feature flags. Learn how client-side SDKs became a public leak.
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.

CrowdStrike reveals a critical 9.8 CVSS flaw in LogScale Self-Hosted. Unauthenticated attackers can read arbitrary server files. Patch to v1.235.1+ now!