 Do Son
YggTorrent infrastructure falls to unknown hackers. Discover the massive 54,000 credit card leak, the "Turbo" tier scandal, and the new ygg.gratis clone.
Data Breach
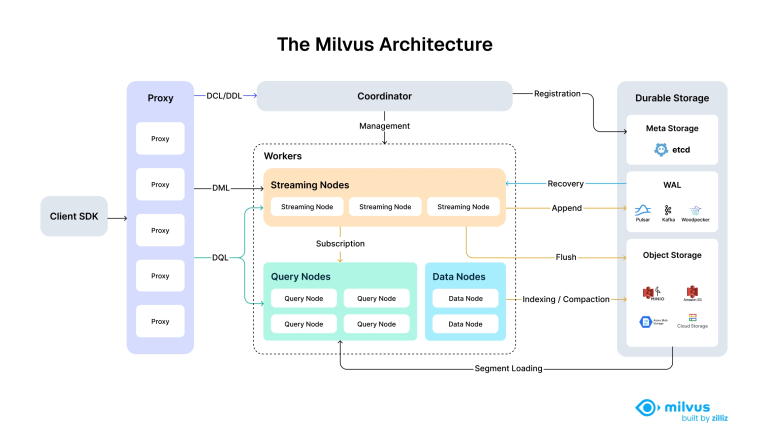
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

Sansec uncovers a keylogger on a major US bank's employee portal. 200,000 staff at risk of credential theft via hidden "side door" malware.

Malwarebytes warns of 17.5M Instagram accounts leaked by "Solonik." Meta denies a system breach but fixed a bug used to spam password reset emails.

Hackers bribed Ubisoft outsourced staff for backend access, leading to a $339T currency exploit and a massive source code leak. Is outsourcing to blame?

Hyderabad police arrest another ex-Coinbase agent for selling user data. The TaskUs insider breach exposed 70k users and cost Coinbase up to $400 million.
Ubisoft takes Rainbow Six Siege offline after a massive backend breach. Hackers gifted 2 billion credits to players and hijacked the game's ban system.

MongoBleed (CVE-2025-14847) allows unauthenticated MongoDB memory leaks. With Joe Desimone's PoC released, upgrade to v8.0.17 or v7.0.28 now!

EmEditor confirms its official site was compromised, redirecting users to a malicious MSI signed by WALSHAM INVESTMENTS LIMITED to steal sensitive data.

Google is retiring its Dark Web Report service in February 2026, stating it only caused anxiety by failing to offer users actionable steps to remedy leaked personal data.

E-commerce giant Coupang confirmed a breach exposing 33.7 million users (names, emails, addresses)—nearly its entire base. Financial data was not compromised, but social engineering risk is high.

OpenAI reveals a data breach at analytics vendor Mixpanel exposed API user emails and IDs. OpenAI has terminated the partnership. Watch out for phishing.

Salesforce revoked all Gainsight app tokens and removed the app from the AppExchange after finding unusual activity that may have exposed customer data via the connection.
Google denies claims of a mass Gmail breach, clarifying that a new HIBP dump of 183M credentials stems from third-party infostealer malware, not a platform hack.

A massive 10TB unprotected database belonging to ClaimPix exposed over 5M files, including sensitive insurance records, powers of attorney, and vehicle VINs.

Two popular apps, one for healthcare and one for jewelry, are leaking sensitive user data over unencrypted connections. Learn how this vulnerability puts you at risk.
A massive 600GB data leak from China's Great Firewall exposes its internal workings, source code, and proof of its export to other countries.

A critical vulnerability in HubSpot’s Jinjava template engine (CVE-2025-59340) could lead to remote code execution. Patch immediately to secure your site.

SolarWinds alerts on a Salesforce data breach impacting numerous companies. The breach exploited compromised OAuth tokens via the Salesloft Drift integration, exposing sensitive customer data.

A new report reveals a surge in coordinated hacktivist attacks on India's critical infrastructure. Groups from Pakistan, Russia, and others are launching breaches and DDoS attacks.

The founder of BreachForums, Conor Fitzpatrick, has been resentenced to three years in prison after his initial lenient sentence was overturned by a U.S. appeals court.

A new report reveals a major surge in phishing attacks targeting U.S. energy companies like Chevron, using cloned websites to steal credentials and financial data.