 Do Son
Kerio Connect vulnerability CVE-2026-112353, a stored XSS flaw via SVG attachments, is exploited in the wild to steal mailboxes. Update to 10.0.8p2.
XSS
WordPress 7.1.4 security release fixes 17 issues, including a core update race condition RCE and ten stored XSS bugs. Update your sites now.
A Roundcube security update fixes 20 flaws, including IMAP command injection and header injection. Upgrade to 1.6.20 or 1.7.5 now.
A critical MapLibre XSS vulnerability allows zero-click code execution in 2.7M weekly downloads. Discover how CVE-2026-85061 works and how to patch now.

The new GitLab patch release fixes 13 flaws, including high-severity XSS and authorization bugs. Update to 19.2.2, 19.1.4, or 19.0.6 now.

A BdThemes supply chain attack poisoned a plugin API feed to run silent XSS in admin browsers, creating rogue admins across WordPress sites.

WordPress 7.0.3 fixes CVE-2026-64638, a pre-auth XSS on the login screen that can escalate to remote code execution. CVSS 8.9. Update now.

Zimbra 10.1.20 fixes multiple Zimbra vulnerabilities, including an SNMP command injection flaw and several XSS bugs. Admins should upgrade now.

A critical Ghost cache poisoning bug lets an unauthenticated x-ghost-preview header hijack staff accounts. Update to Ghost v6.37.0 now.
New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.
Learn about the Apache ECharts XSS vulnerability (CVE-2026-45249) in the Lines series tooltip rendering logic and find out how to secure your code.

GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!

Critical Siemens Alert: 9.3 severity XSS flaws hit SIMATIC S7 PLCs. Attackers can hijack sessions via web interfaces. Update to V3.1.6 or follow mitigations.
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!

Zabbix fixes high-severity XSS (CVE-2026-23926) and Oracle injection flaws. Don't let your monitoring tool become a backdoor—upgrade your Zabbix server now!
Apache Wicket 10.9.0 fixes 3 Critical flaws: Path Traversal (CVE-2026-43975), Session Fixation, and Resource Guard bypass. Secure your Java apps and patch now!

Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.
Critical RCE and XSS vulnerabilities hit Apache ActiveMQ (CVE-2026-41044, 40466). Authenticated attackers can hijack the JVM. Update to 5.19.6 or 6.2.5 now.
Apache Storm patches a critical RCE via unsafe deserialization and a stored XSS in its UI. Secure your data streams—upgrade to version 2.8.6 today!
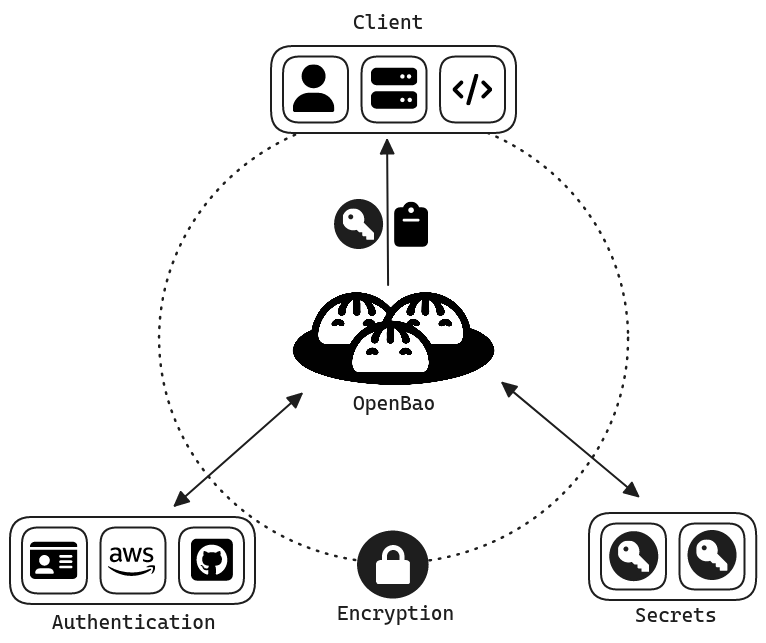
OpenBao patches critical 9.6 and 9.4 CVSS flaws in OIDC flows. Learn how "direct mode" enables session hijacking and XSS token theft. Update to 2.5.2 now.

MantisBT patches a critical 9.3 CVSS auth bypass (CVE-2026-30849) and high-severity XSS flaws. Learn how MySQL type conversion opens the door. Update now!

Cisco alerts of public flaws in IOx app hosting. Unauthenticated actors can manipulate logs (CVE-2026-20113), plus a stored XSS risk (CVE-2026-20112). Patch now!