 Do Son
TrustFall vulnerability CVE-2026-88235 PoC is public: any Windows user can abuse TrustedInstaller to act as SYSTEM. Install the November 2026 update.
privilege escalation
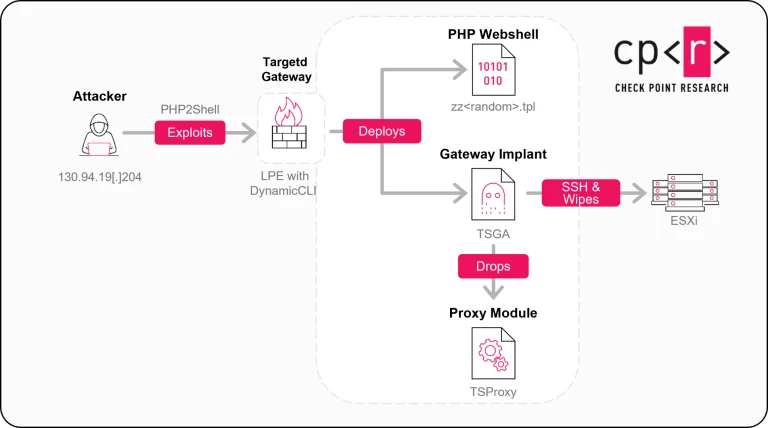
Check Point Gateway vulnerability CVE-2026-123039 exploited with PHP2Shell to gain root, plant backdoors and wipe ESXi. Patch to R82.20 Take 14.
Citrix NetScaler vulnerabilities fixed: CVE-2026-120868 hits default setups, CVE-2026-120869 bypasses Console login. Upgrade to 14.1-73.57 now.
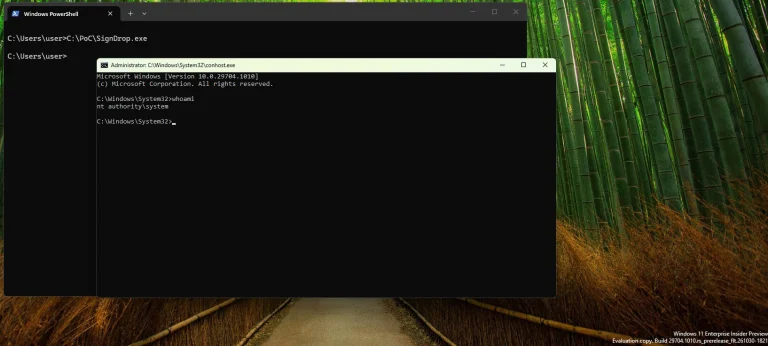
SignDrop, an unpatched Windows CLFS zero-day, now has a public proof-of-concept exploit that gives standard users SYSTEM privileges. No patch yet.
Axis fixes 15 flaws, led by AXIS Camera Station bug CVE-2026-13312 (CVSS 9.9) that could compromise a system. AXIS OS updates also released.
Zoom Workplace for Windows 7.1.8 fixes CVE-2026-108186 (CVSS 9.6) and CVE-2026-108187, two escalation of privilege flaws. Update now.
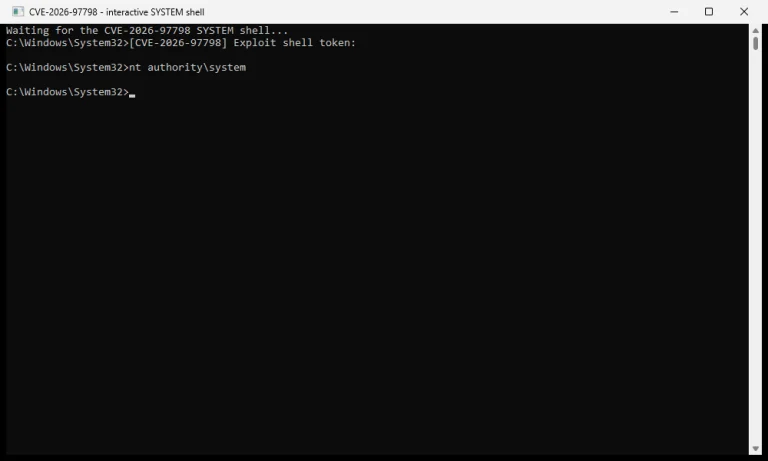
A proof-of-concept exploit for CVE-2026-97798, a Windows Error Reporting vulnerability, gives a SYSTEM shell. Install the October 2026 update now.
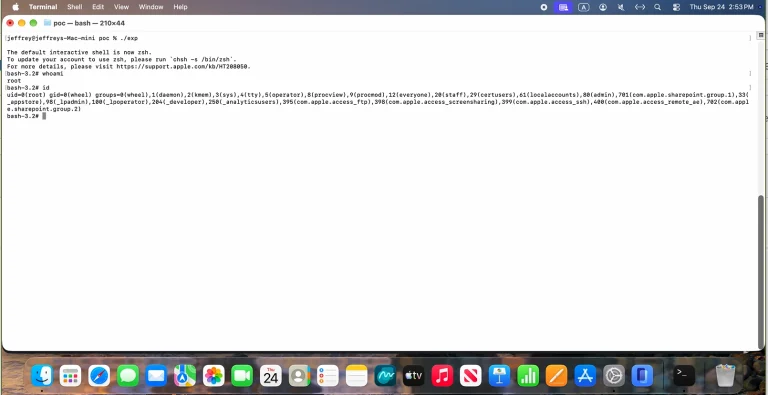
Details and a macOS privilege escalation PoC exploit are public for CVE-2026-112445. Patch macOS now to stop local users from gaining root privileges.
Patch two critical INFINITT PACS vulnerabilities today. Learn how CVE-2026-16305 and CVE-2026-16306 expose medical systems and secure your network now.
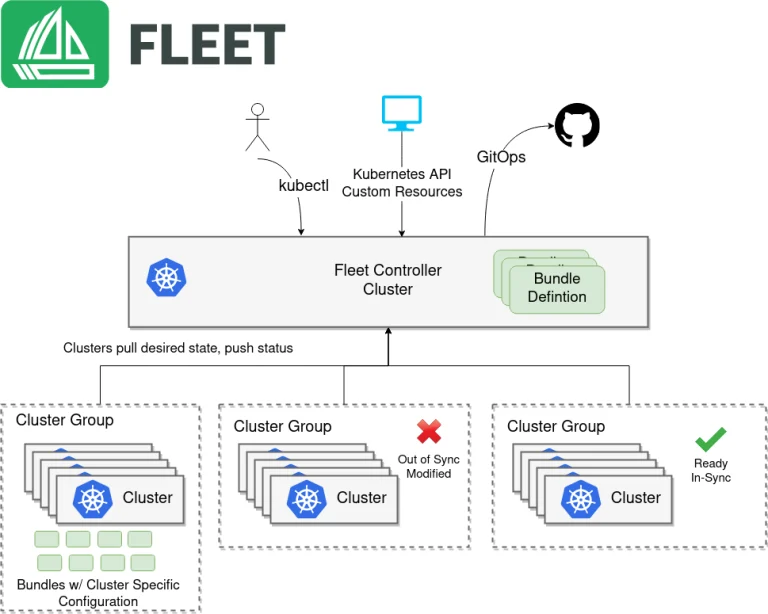
The new Rancher Fleet vulnerabilities patch resolves two Rancher Fleet vulnerabilities, including cluster-admin privilege escalation flaw CVE-2026-94290.
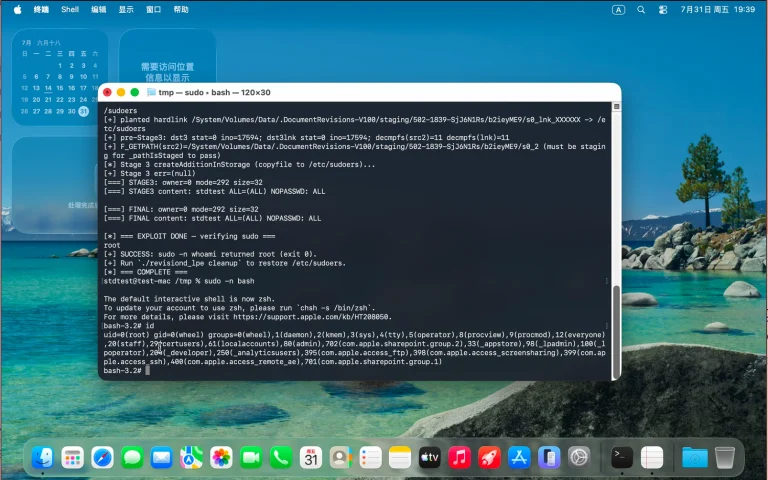
Technical details and a macOS revisiond vulnerability PoC exploit for CVE-2026-112487 are public, allowing root elevation. Update macOS immediately.
The November 2026 bulletin resolves critical MediaTek vulnerabilities, including modem flaws CVE-2026-20499, CVE-2026-20545, and CVE-2026-20546.
Details and a Linux kernel vulnerability PoC exploit are public for CVE-2026-31419. Patch this high-severity flaw to prevent local privilege escalation.
Update to TeamViewer 15.83 to patch three high-severity TeamViewer vulnerabilities: CVE-2026-92372, CVE-2026-111585, and CVE-2026-92374.
PoC and full details are public for the Linux nf_tables vulnerability CVE-2026-23111. The kernelCTF exploit gains root and escapes containers. Patch now.
A severe Tailscale SSH vulnerability allows attackers on authorized nodes to exploit Unix socket forwarding and escalate privileges to root access.
ZDI publicly posted details of unpatched Linux kernel vulnerabilities, including two CVSS 9.0 KSMBD remote code execution flaws. Fixes are pending.
Arista says VeloCloud Orchestrator vulnerability CVE-2026-114625, a CVSS 9.9 SQL injection, is exploited in the wild. Upgrade on-prem VCO now.
Two critical Portainer vulnerabilities enable a bind mount bypass and Docker host takeover by standard users. Upgrade to Portainer 2.45.2 now.
Details and PoC exploits are public for six Linux kernel vulnerabilities, including CVE-2026-98260, enabling privilege escalation. Patch now.
A Citrix security update fixes seven XenServer and UniconOS flaws, including guest-to-host and privilege escalation bugs. Patch hosts and thin clients.
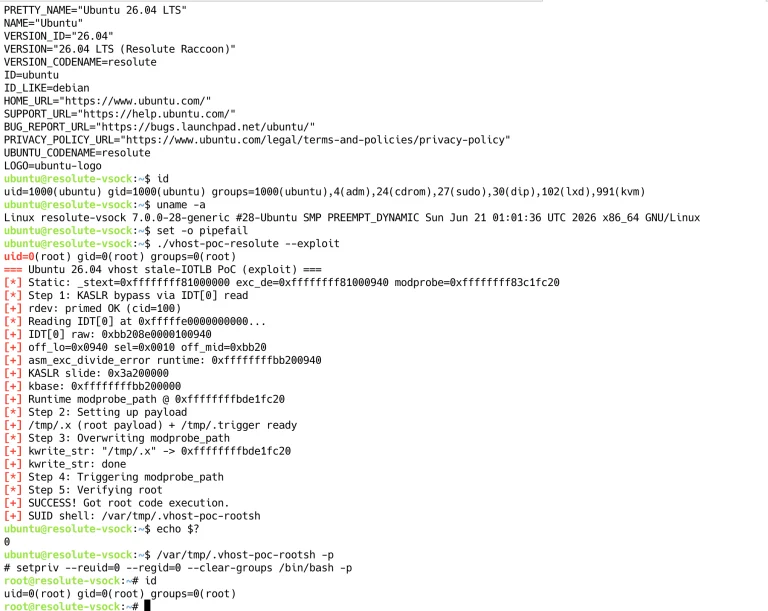
Technical details and PoC exploit code for CVE-2026-74580 (Vghost), an 8.8-severity Linux vhost vulnerability allowing root LPE and VM escape, are out.