 Do Son
ServiceNow has patched five critical ServiceNow vulnerabilities, including an unauthenticated SQL injection flaw. Update your instances to stay secure.
privilege escalation
A new Sudo security vulnerability (CVE-2026-96512) allows local users to bypass time-based restrictions. Learn how to mitigate this high-risk Linux flaw.
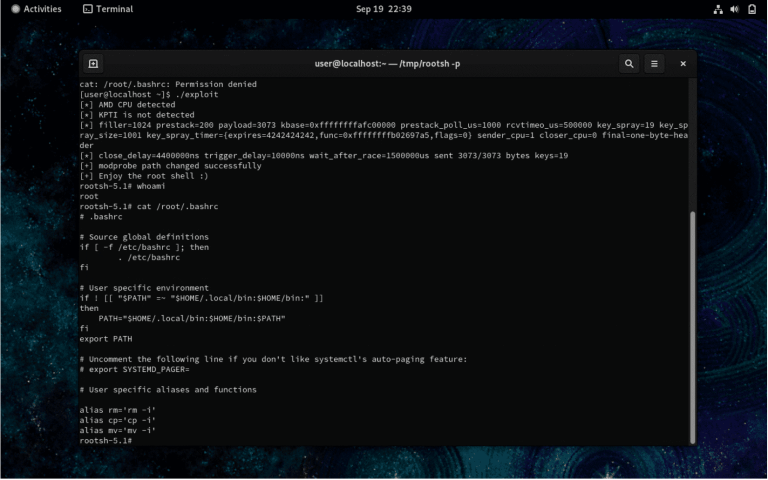
RustyTux is a public PoC for a Linux kernel privilege escalation via an ESP-in-TCP use-after-free (CVE-2026-23239). Details and exploit code are now public.
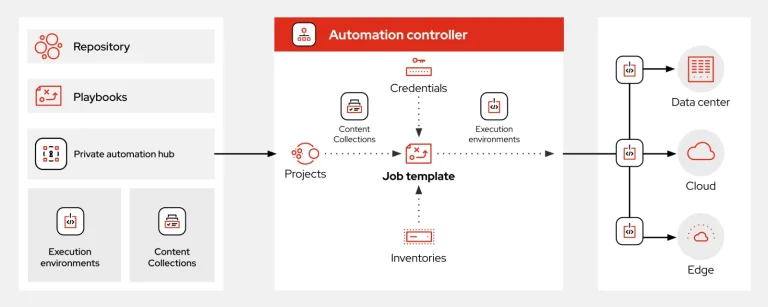
Patch these critical Ansible Automation Platform vulnerabilities to prevent privilege escalation. Ansible Automation Platform vulnerabilities expose secrets.
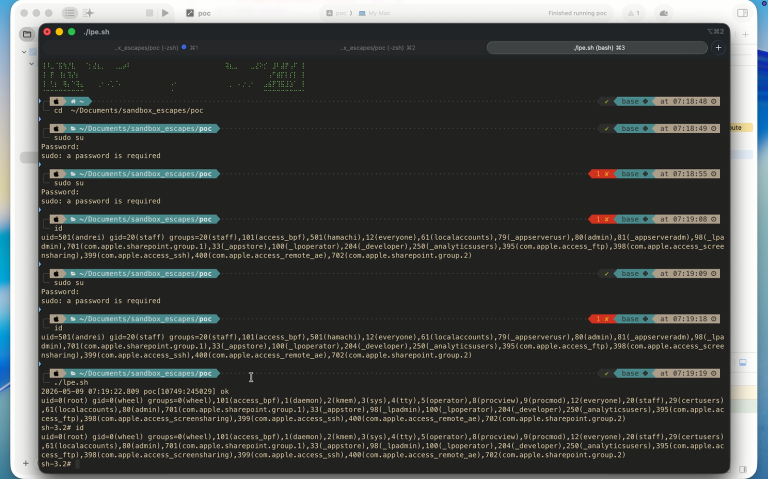
Details and PoC for the critical macOS DesktopServicesHelper vulnerability are public. Learn how CVE-2026-43783 enables root access.
cPanel patched critical cPanel security vulnerabilities including CVE-2026-87899. Update cPanel and WP Toolkit now to prevent privilege escalation.
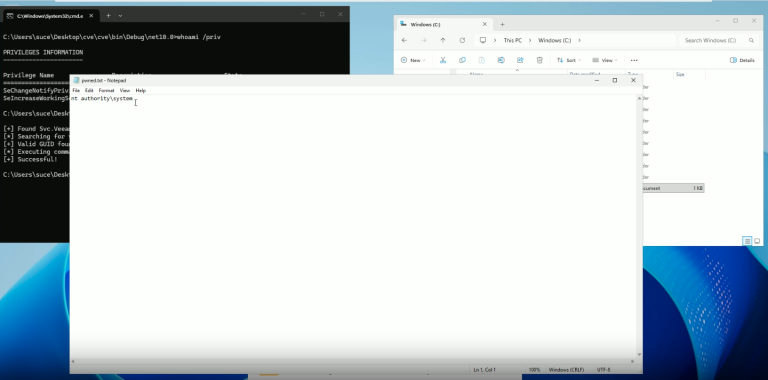
A critical exploited Veeam Agent vulnerability (CVE-2026-32996) is under active attack. Public PoC exploit code has been disclosed. Update systems now.
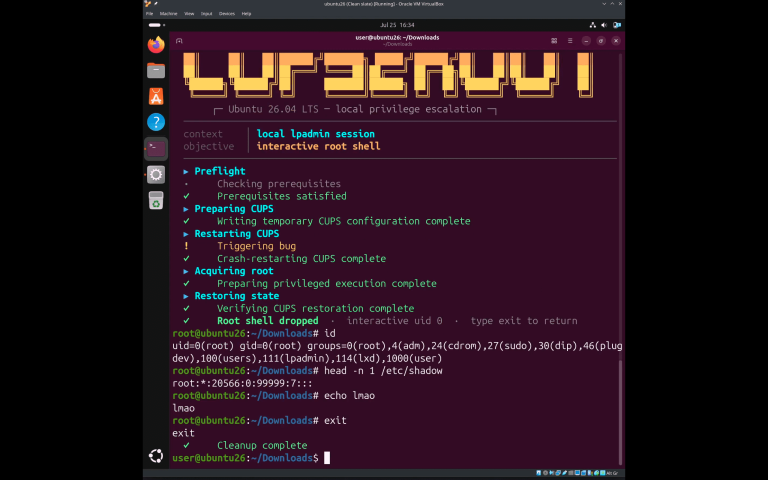
A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
CISA warned of exploited Linux kernel vulnerabilities in the KEV catalog. Patch these Linux kernel vulnerabilities to block privilege escalation.
Four Linux kernel privilege escalation flaws were disclosed with public PoC exploits granting local root. Details and patches are now out. Update now.
A critical KVM guest escape (CVE-2026-89775) enables an LPE to gain root on Linux hosts. Patch this KVM guest escape vulnerability now.
The LSPromise exploit chain provides a 100% success rate for local privilege escalation to root on Android 17. Details and PoC are publicly disclosed.
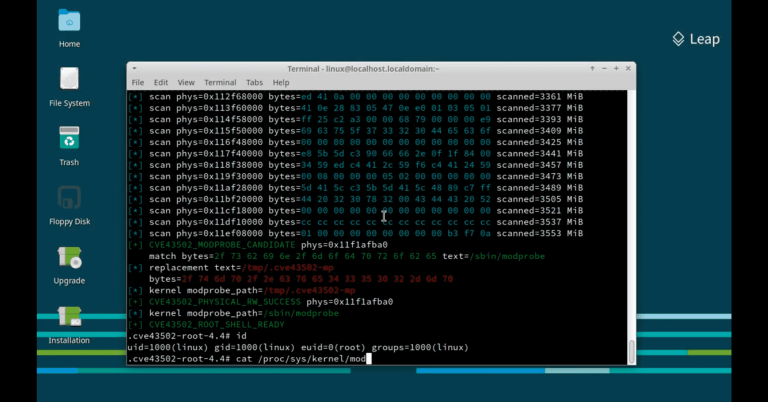
The details and PoC exploit code for the ZcopyReaper Linux vulnerability (CVE-2026-43502) are publicly disclosed, posing a privilege escalation risk.
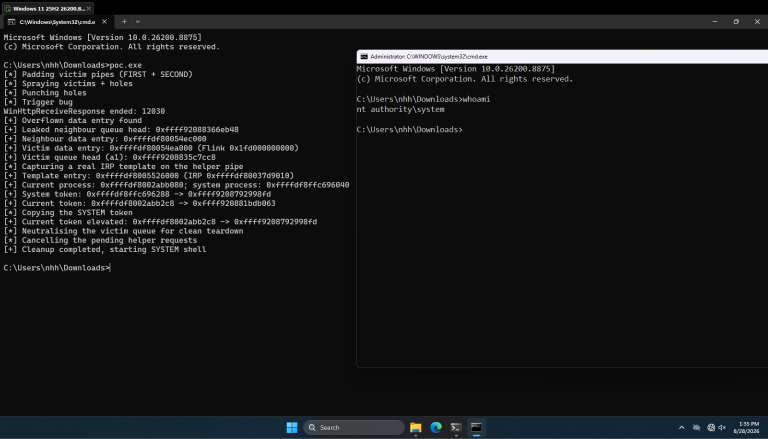
A Windows HTTP.sys vulnerability, CVE-2026-62735 (CVSS 7.8), now has public details and a PoC. It escalates local users to SYSTEM. Patch now.
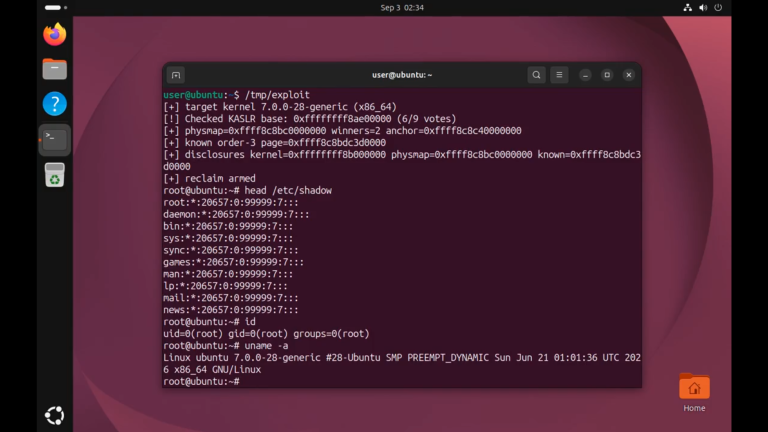
Security researchers released a Linux CVE-2026-52924 PoC exploit. Check flaw details and patch instructions to secure your systems against root takeovers.
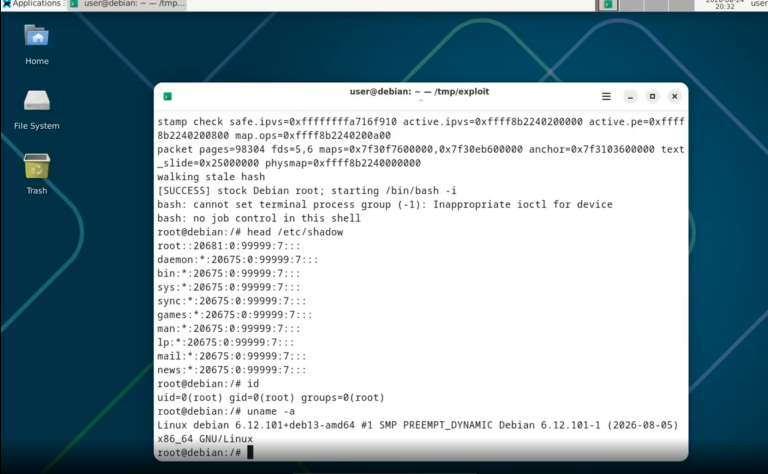
CVE-2026-80714 (CVSS 9.8) is a Linux kernel IPVS use-after-free with public PoC code enabling root privilege escalation on Debian. Patch now.
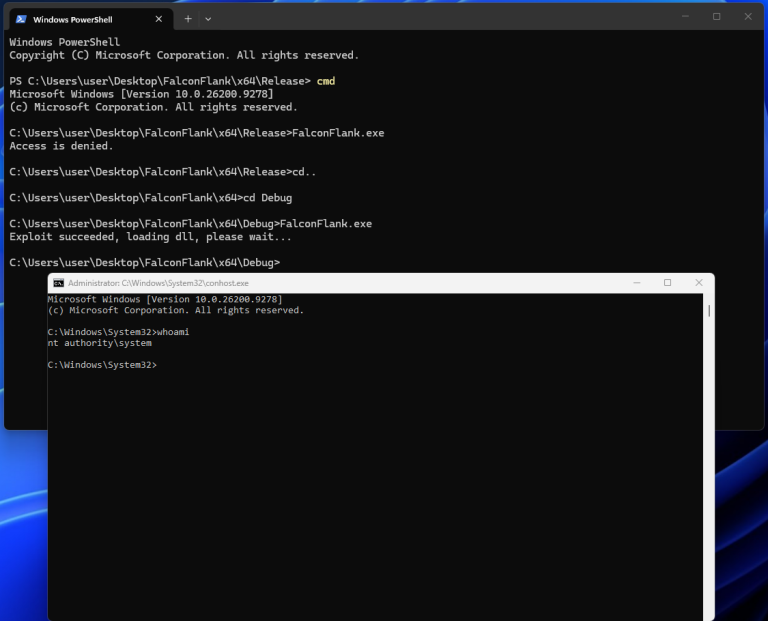
A researcher claims a CrowdStrike Falcon vulnerability enabling privilege escalation and published a PoC. CrowdStrike has not confirmed it; no CVE exists.
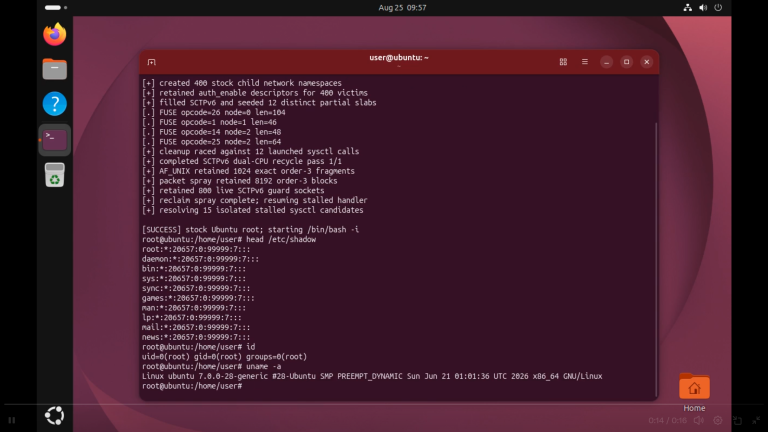
CVE-2026-68162, a Linux kernel vulnerability in SCTP (CVSS 7.8), has public PoC code enabling root privilege escalation on Ubuntu 26.04. Patch now.
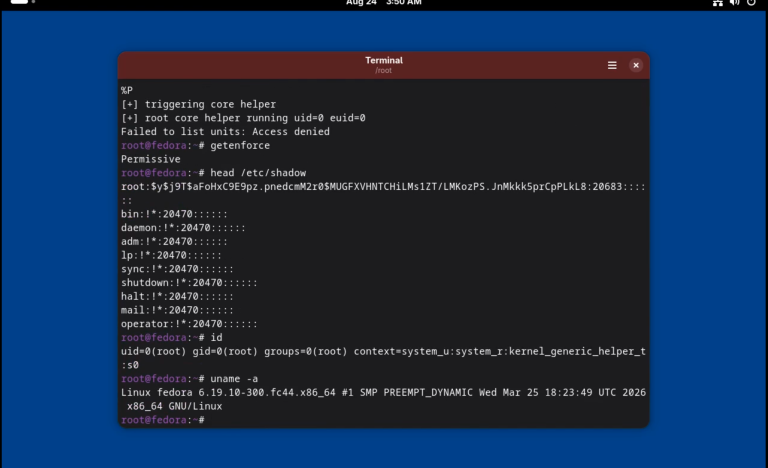
A public proof-of-concept for the CVE-2026-52933 privilege escalation flaw is available. This Linux kernel io_uring exploit carries a CVSS 7.8 score.
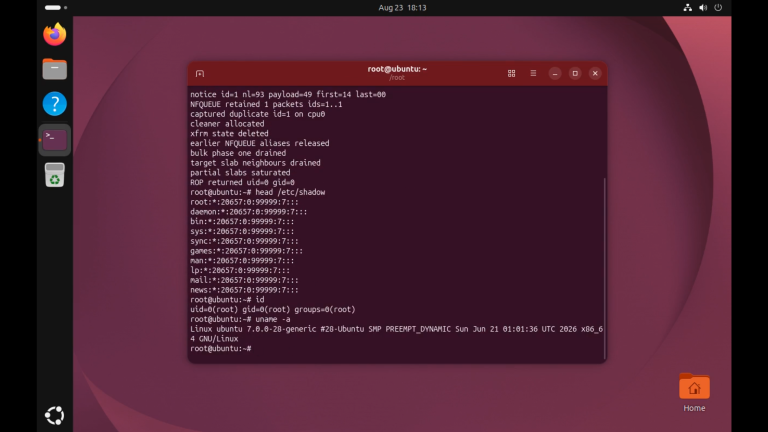
A public PoC exploit targets CVE-2026-72137, a CVSS 9.8 Linux kernel double-free that enables root privilege escalation. Patch now.
FreeBSD patched 8 vulnerabilities on August 25, 2026, mostly local privilege escalation flaws plus a ppp code execution bug. Update now.
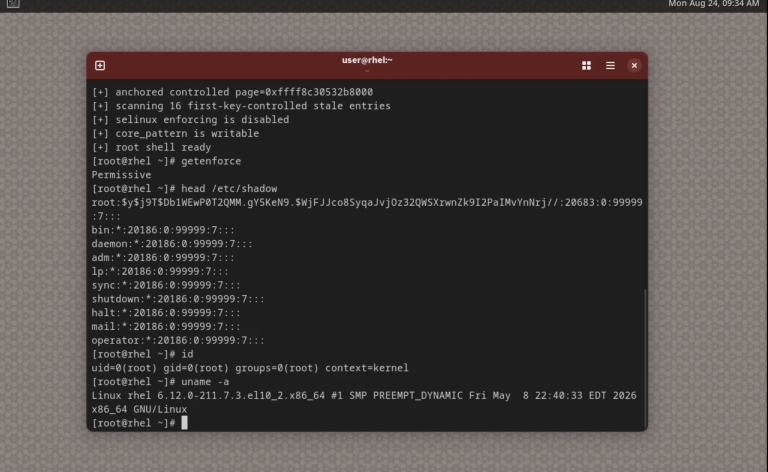
A public PoC for the Linux kernel flaw CVE-2026-52923 allows local attackers to escalate to root privilege. Learn about the patch and technical details.