 Do Son
NoisyTCP vulnerability CVE-2026-99288 lets remote attackers panic Linux kernel TCP servers pre-auth. Patch to 6.12.117, 6.18.63 or 7.3.4.
Linux Kernel
A public exploit for CVE-2026-80521, an AF_UNIX use-after-free, enables Linux kernel privilege escalation. Fixed in 7.1.10, 6.12.111 and 7.2.
Update your Veeam Software Appliance and Backup & Replication servers now to fix CVE-2026-98432, a critical 9.8 CVSS Linux kernel flaw.
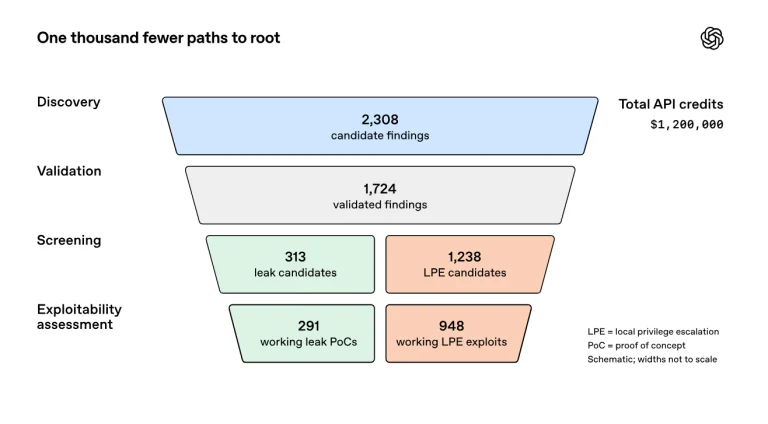
An upcoming OpenAI cyber model found 1,724 Linux kernel vulnerabilities and built 948 local root exploits to help maintainers patch critical bugs.
Ubuntu puts fixes for CVE-2026-98432, a Linux kernel TCP flaw rated CVSS 9.8, in the proposed pocket for 22.04 LTS and newer. Older releases wait.
Arista fixed critical Arista security vulnerabilities CVE-2026-111497 and CVE-2026-98432 that allow unauthenticated remote code execution. Update now.
Linux kernel vulnerabilities this week: 129 CVEs, including critical iSCSI flaws CVE-2026-99154 and CVE-2026-99153. Get the kernel security update.
Details and a Linux kernel vulnerability PoC exploit are public for CVE-2026-31419. Patch this high-severity flaw to prevent local privilege escalation.
A critical Linux kernel CVE-2026-98432 flaw enables remote root execution via MPTCP race conditions, impacting multiple distributions including Ubuntu.
CISA adds Linux kernel vulnerability CVE-2026-46300, chained with PHP2Shell for root, and VMware ESX flaw CVE-2026-41709 to KEV. Patch now.
Anthropic's AI vulnerability research found remote code execution chains in Chrome, Safari, Android, Windows and Linux. All are now fixed.
PoC and full details are public for the Linux nf_tables vulnerability CVE-2026-23111. The kernelCTF exploit gains root and escapes containers. Patch now.
A PoC and full details are public for CVE-2026-43501 (CVSS 9.8), a Linux kernel IPv6 vulnerability in RPL source routing. Update your kernel now.
ZDI publicly posted details of unpatched Linux kernel vulnerabilities, including two CVSS 9.0 KSMBD remote code execution flaws. Fixes are pending.
The Linux Assisted-by tag is going away after maintainers agreed it misreports AI use, but human accountability stays.
PwnEscape (CVE-2026-99999) is a critical Linux kernel VM escape that let a guest run code as root on the host in lab tests. Update your kernel now.
Details and PoC exploits are public for six Linux kernel vulnerabilities, including CVE-2026-98260, enabling privilege escalation. Patch now.
Linus Torvalds used a Claude Code Linux kernel patch to triple small data read speeds via RCU memory management, though the experimental code needs testing.
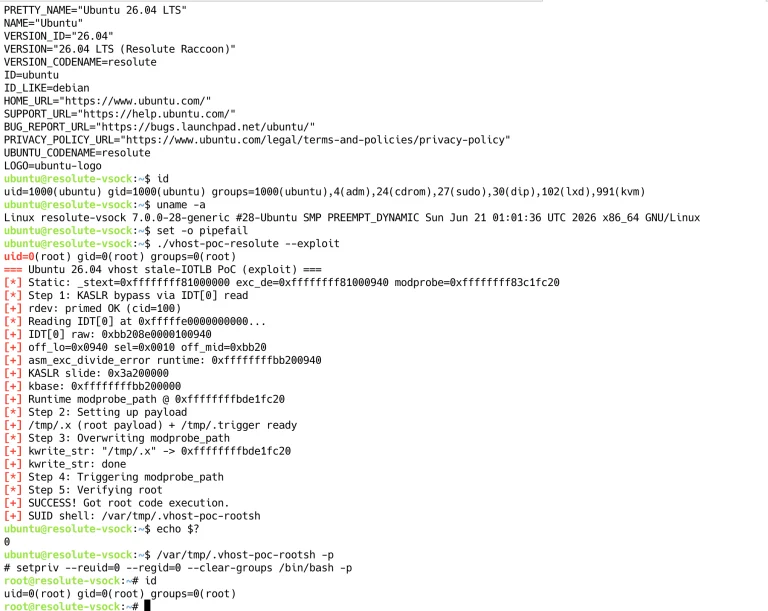
Technical details and PoC exploit code for CVE-2026-74580 (Vghost), an 8.8-severity Linux vhost vulnerability allowing root LPE and VM escape, are out.
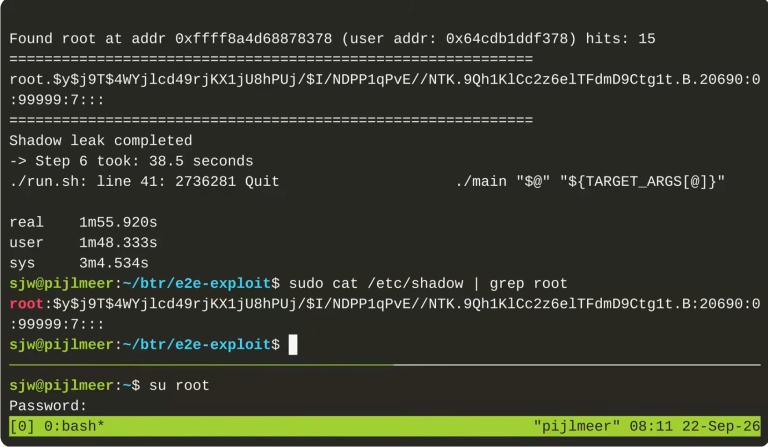
VUSec released details and PoC code for Branch Target Reuse, a Spectre-v2 attack on JIT engines that leaked Linux root password hashes. Patch now.
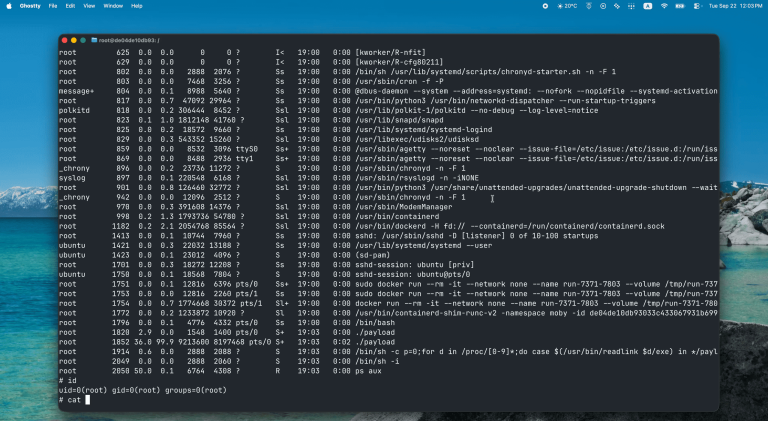
Details for a critical Linux container escape flaw are public. Discover how this Linux container escape flaw works and review key mitigation steps.
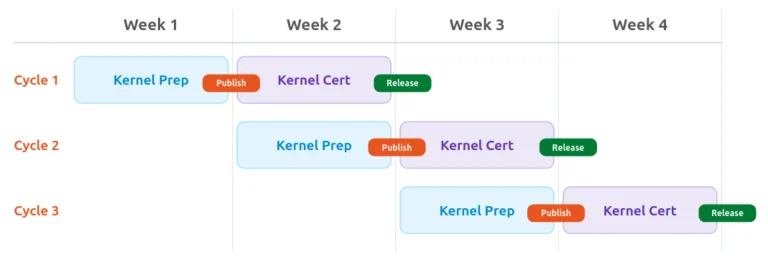
Learn why Canonical accelerated Ubuntu kernel updates. A surge in CVEs prompted a shift to an overlapping two-week SRU cycle for faster vulnerability patching.