
 Do Son
Google uncovers UNC6508 cyber espionage using INFINITERED malware to target US medical and defense research. Learn how to protect your organization.
malware

Hackers are hiding malware inside malicious Steam wallpapers. Learn how the Wallpaper Engine app exposes gamers to account hijacking and crypto miners.
A ShapedPlugin supply chain attack (CVE-2026-10735) injected malware into WordPress Pro plugins. Discover the impact and how to protect your site today.

Discover how a simple phishing email triggers a complex Agent Tesla infection chain, using process injection and in-memory loading to steal sensitive data.

A stealthy GPU cryptojacking campaign leverages AI search poisoning and process hollowing injection to hijack high-end rigs. Read the Microsoft report.
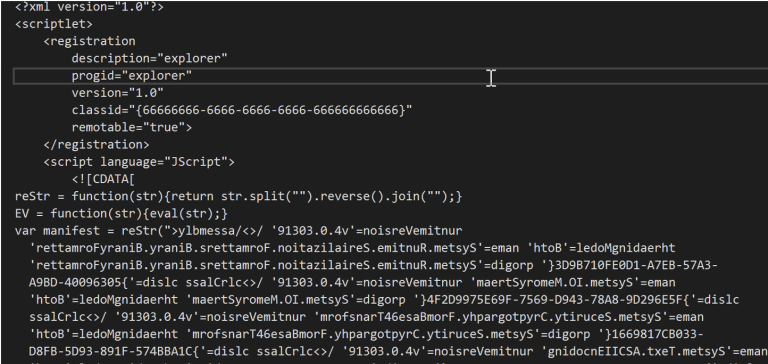
Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.
Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.
Sophos X-Ops uncovers a fake Claude AI site (claude-pro.com) distributing an undocumented backdoor via DonutLoader. Protect your team from AI-themed lures.

JDownloader's website was breached on May 6, swapping official installers for malware. If you downloaded it between May 6-7, your system may be compromised.
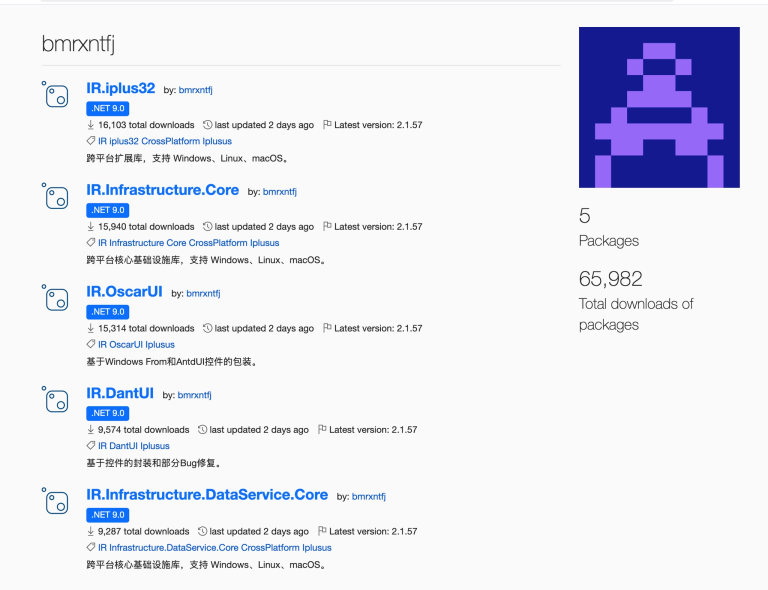
Critical alert: A stealth NuGet supply chain attack has hijacked 65,000 .NET workstations. Audit your CI/CD for malicious IR.* packages immediately.

OceanLotus targets Python developers worldwide via PyPI supply chain attacks. New ZiChatBot malware hijacks Zulip APIs for invisible C2 traffic. Patch now!
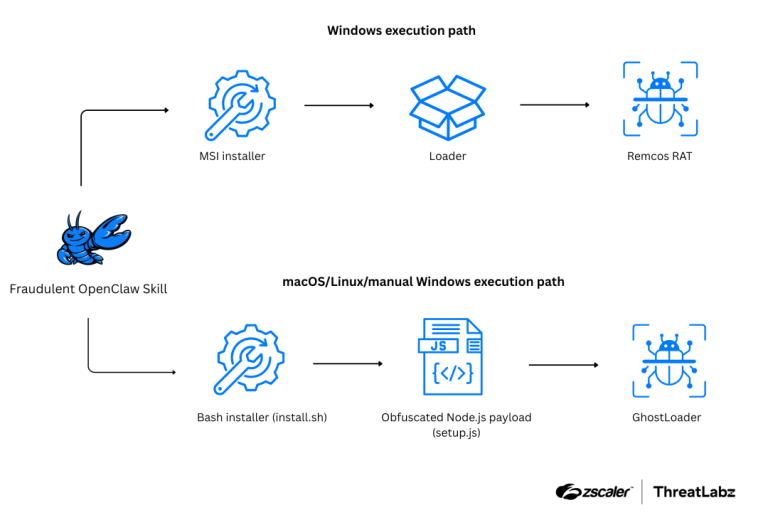
Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!
Kaspersky warns that DAEMON Tools installers (v12.5) are trojanized with the QUIC RAT. Signed binaries are being used for global espionage. Update and audit now!
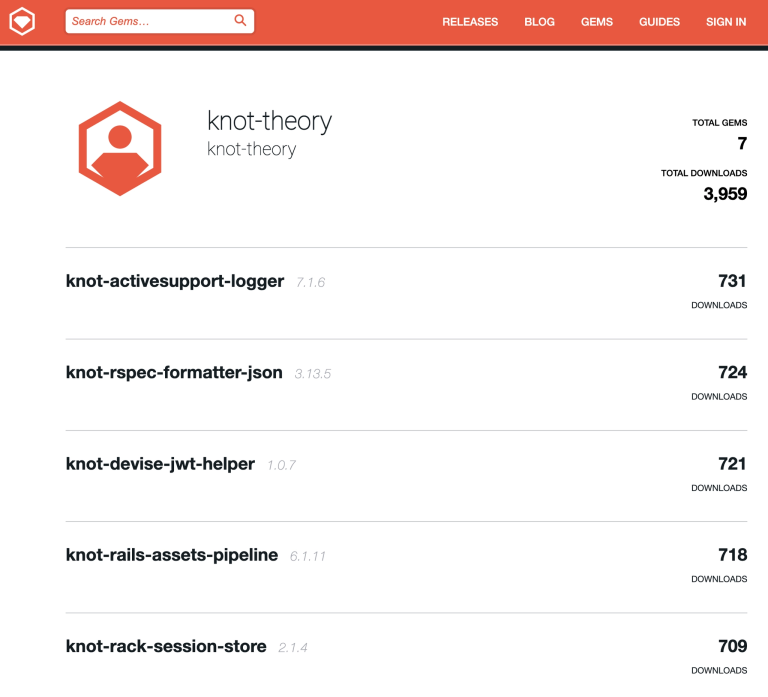
Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!

The alleged mastermind behind the massive "Versus Project" dark web market has been extradited to the US. He faces life in prison for cybercrime and drugs.
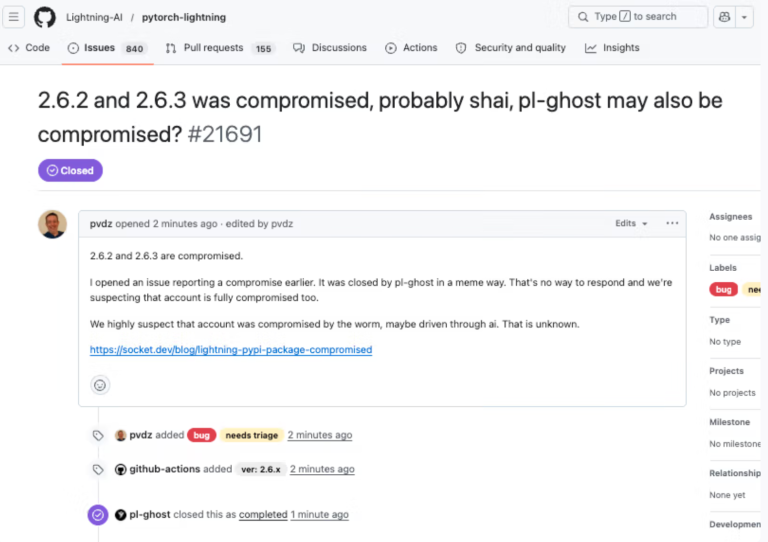
Lightning framework v2.6.2 & 2.6.3 are malicious. The "TEAM PCP" worm steals cloud secrets and poisons repos. Downgrade to 2.6.1 and rotate keys immediately!

Yeeth Security uncovers a sophisticated Open VSX campaign using string-fragment reconstruction to hide malware. 16 malicious extensions identified.
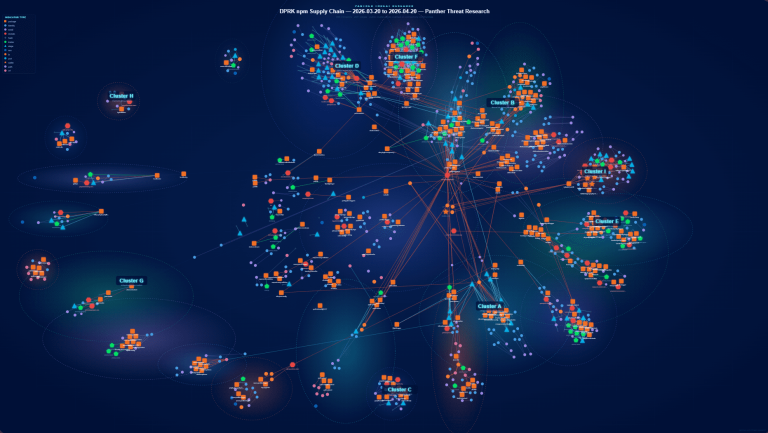
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.
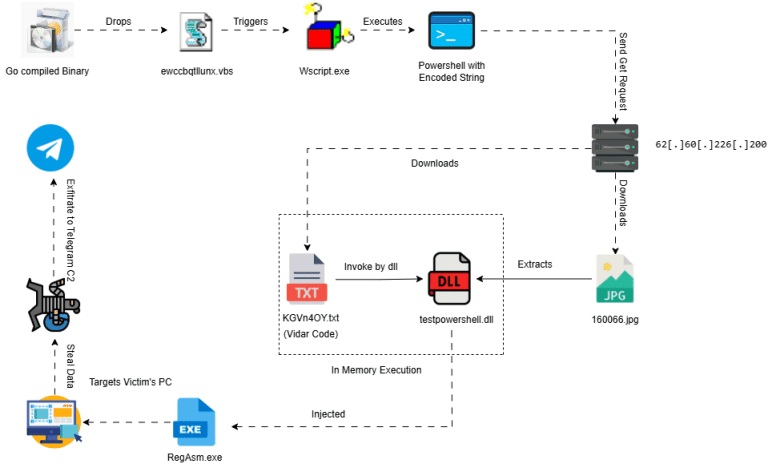
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.
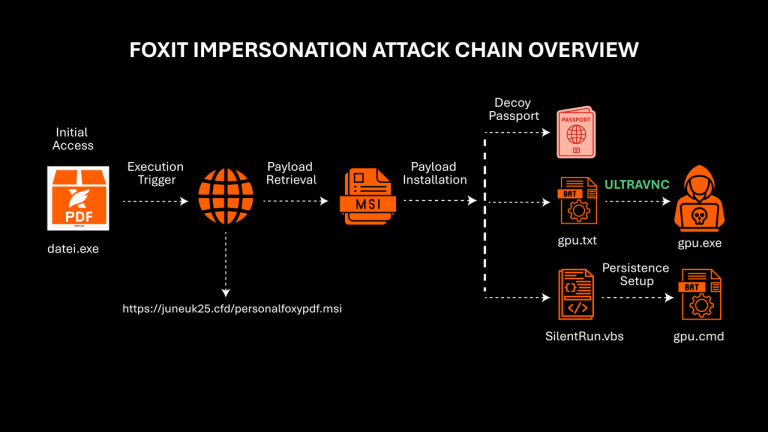
G DATA warns Foxit PDF users of a global malware campaign using fake installers and Danish passport decoys to deploy hidden UltraVNC remote access tools.

Bitwarden CLI v2026.4.0 compromised in "Dune"-themed supply chain attack. Malware steals cloud secrets and SSH keys. Rotate your credentials immediately.
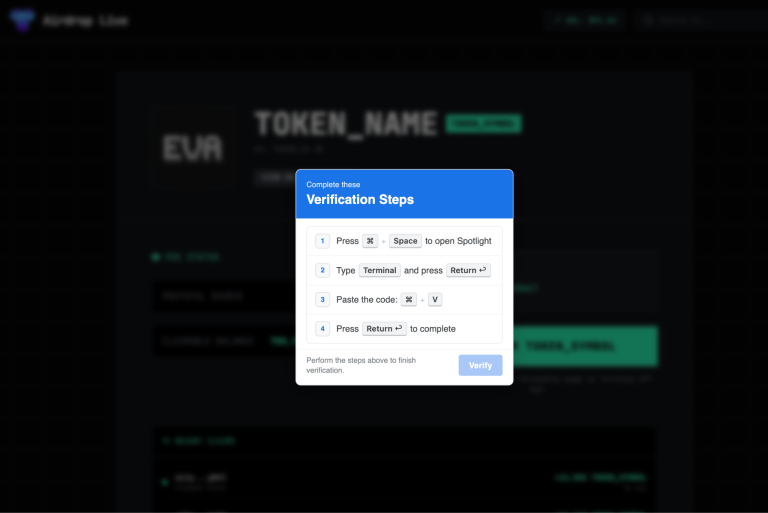
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.