
 Do Son
LayerX unmasks 12 TikTok downloader extensions tracking 130,000+ users. Even "Featured" tools can be traps. Learn how this resilient malware ecosystem works.
malware
Splunk STRT identifies a new campaign bundling Ghost RAT with CloverPlus adware to steal RDP credentials and monetize infections. Patch your systems now!
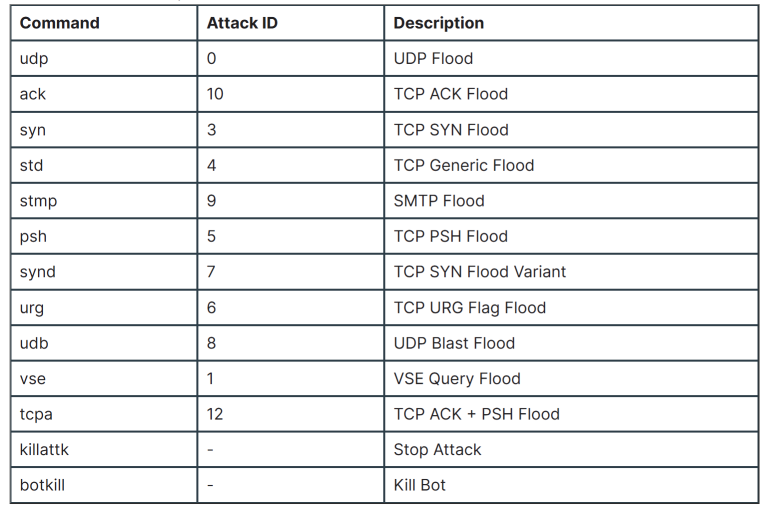
FortiGuard unmasks Nexcorium, a Mirai variant targeting DVRs via CVE-2024-3721. Secure your IoT devices against this multi-arch DDoS botnet. Patch now!
Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.
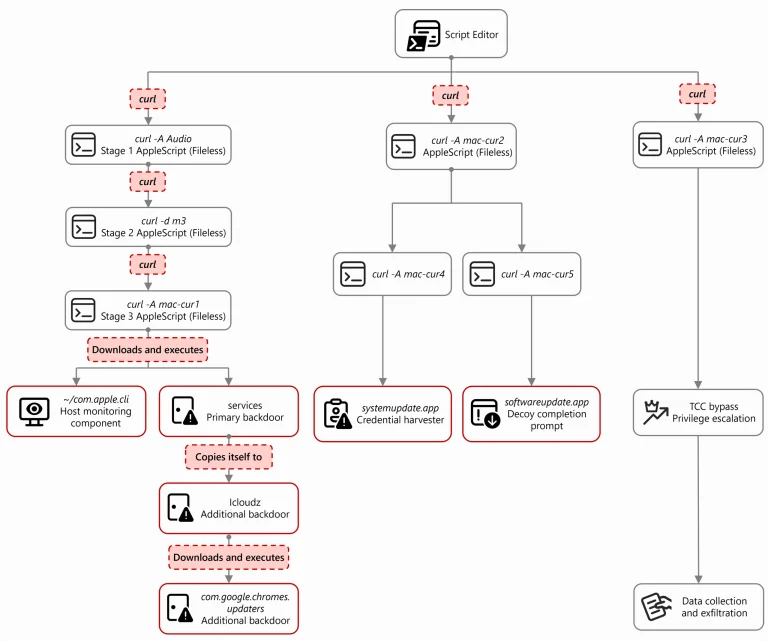
Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.
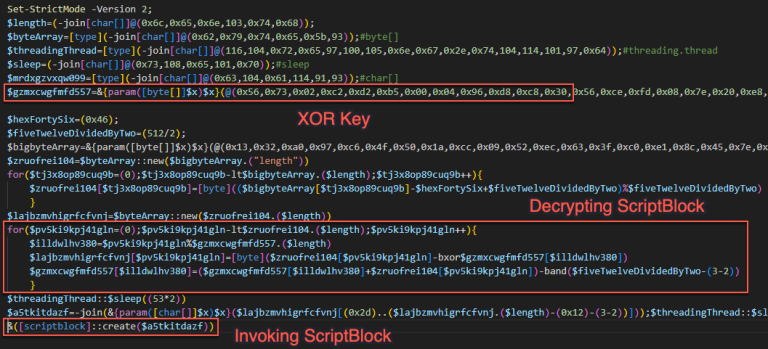
Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.

Microsoft Defender faces a critical "Red Sun" vulnerability. Learn how this zero-day exploit bypasses security to grant hackers full administrative control.
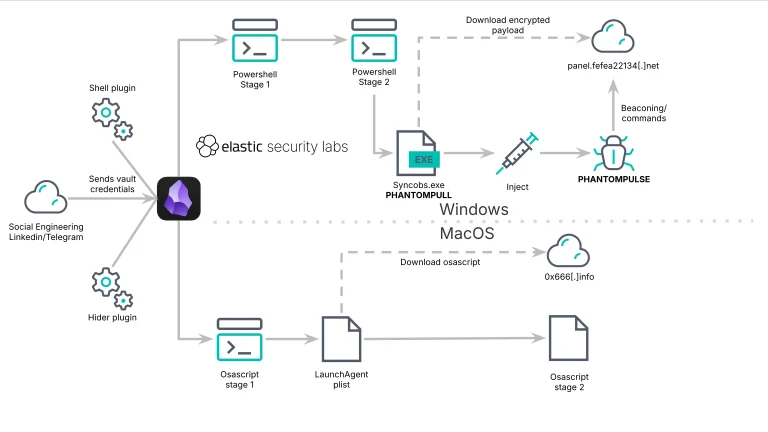
Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.
PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.

Socket identifies 108 malicious Chrome extensions stealing Telegram sessions and Google IDs. 20,000 installs hit—audit your browser extensions immediately!
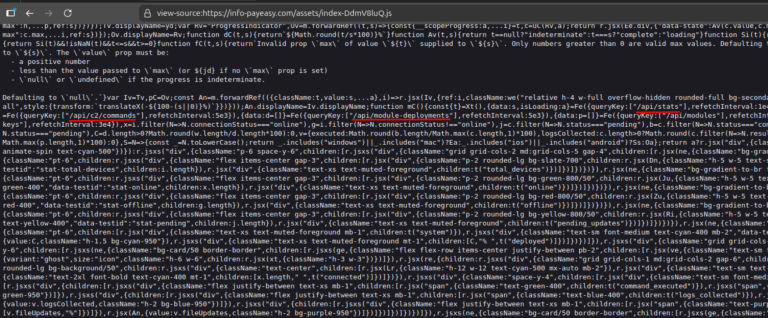
Hunt.io discovers Canis C2, an AI-assisted surveillance framework targeting all major OSs. An exposed API revealed payloads and source code. Read more here.

April 2026 Alert: CPUID downloads for CPU-Z and HWMonitor were poisoned with STX RAT via DLL sideloading. Check your systems for CRYPTBASE.dll now!

eSentire TRU uncovers STX RAT, a modular Trojan targeting finance with HVNC, AMSI Ghosting, and advanced encryption. Secure your perimeter—learn how it works.

Jamf identifies a macOS ClickFix pivot: attackers now use the Script Editor to bypass Terminal scans and deliver Atomic Stealer. Learn how to stay protected.
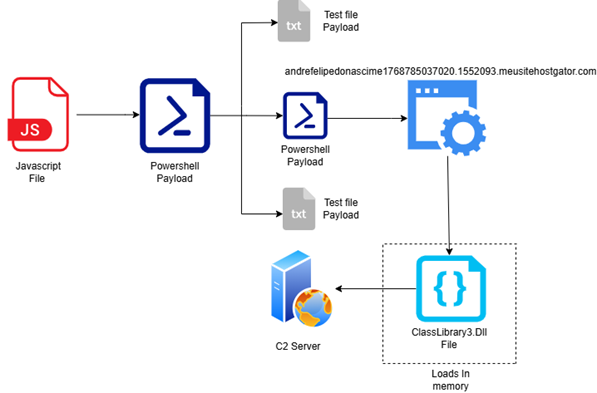
Lat61 Team uncovers DesckVB RAT, a stealthy 2026 Trojan using in-memory .NET loaders & JS obfuscation to hijack systems and evade AV. Learn how it works.

DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.
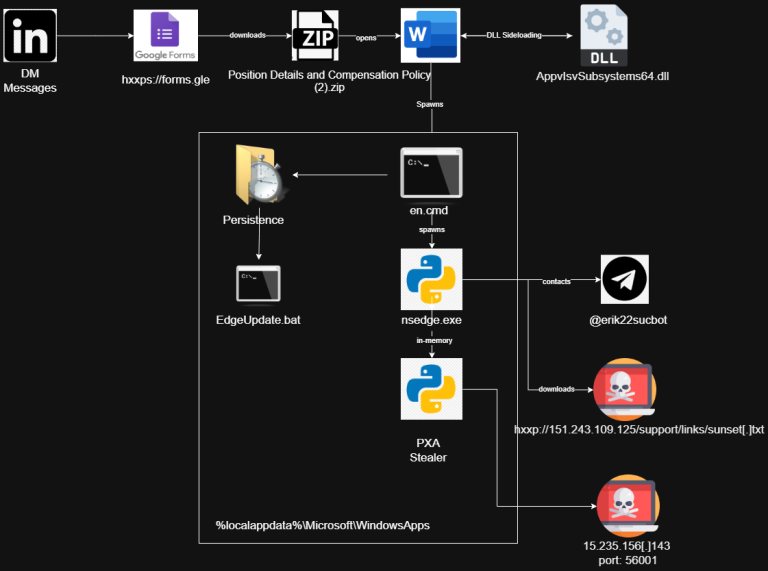
LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.

Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!

Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.

DomainTools unmasks a malicious "ChatGPT Ad Blocker" Chrome extension that steals private conversations and sends them to Discord. Check your extensions now!