 Do Son
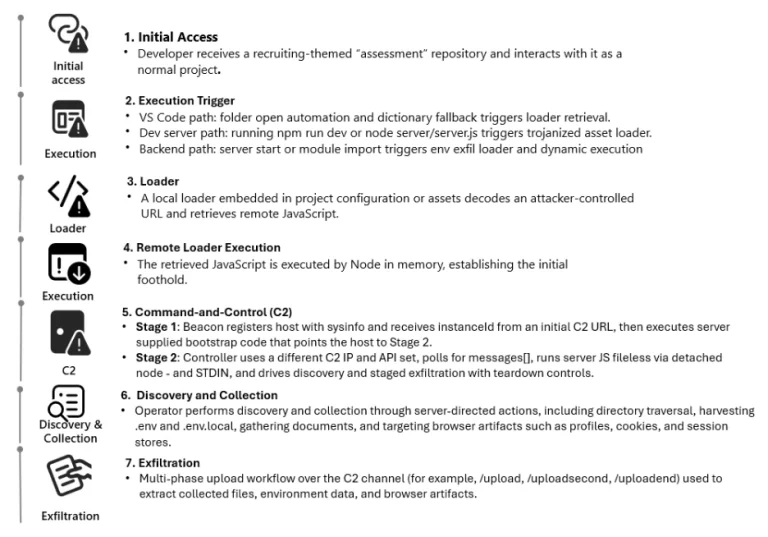
Microsoft warns of a new campaign targeting engineers via fake Next.js technical assessments. Malware hides in VS Code tasks and npm scripts to steal secrets.
malware

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.
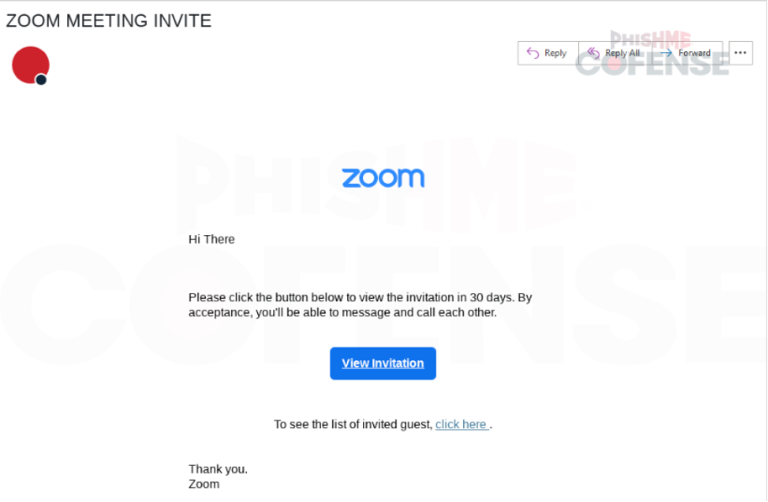
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.
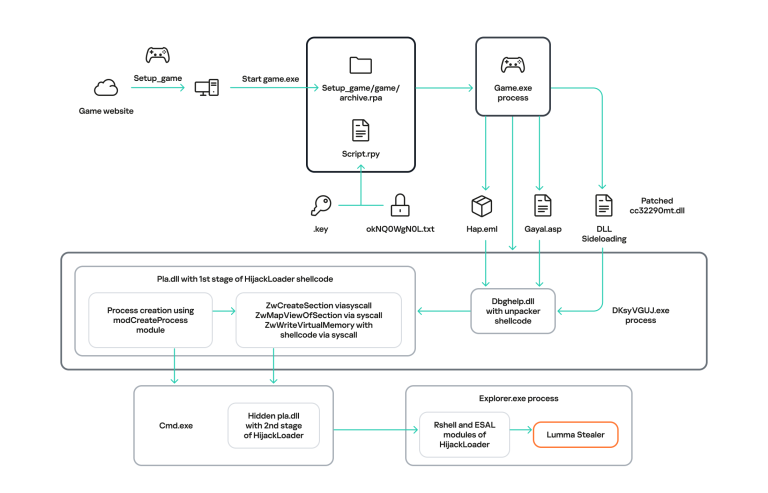
Kaspersky warns: Pirated visual novels are spreading RenEngine malware. Attackers use fake downloads to install ACR Stealer. Protect your data now.
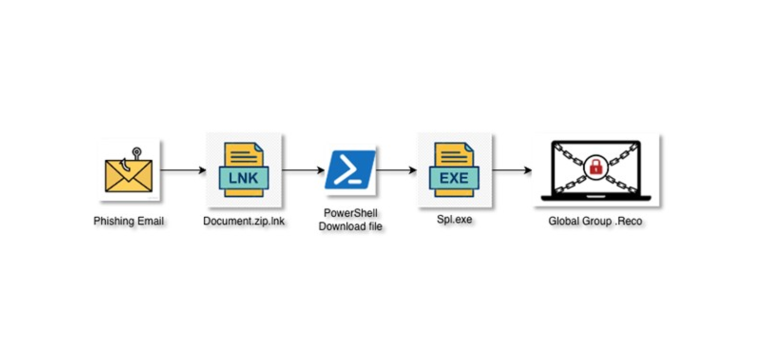
Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.
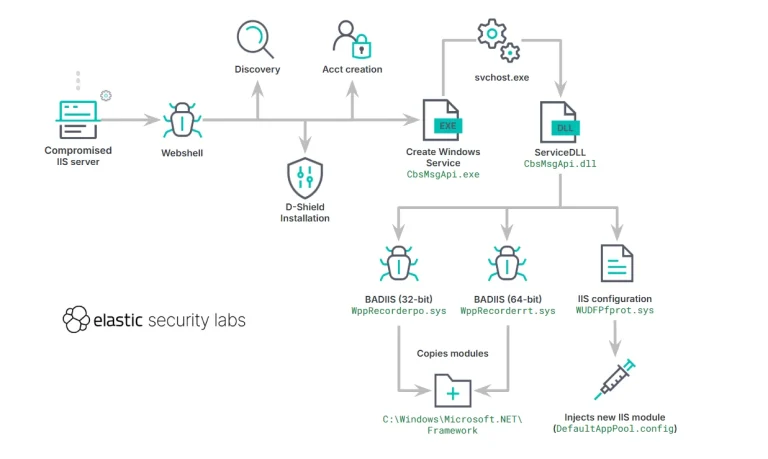
Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.

Warning: 7zip [.] com has been hijacked to spread residential proxy malware. Learn how to identify this 7-Zip impersonator and protect your system.

Silent Push reveals a massive SystemBC botnet with 10,000+ infected IPs. The SOCKS5 proxy malware hit government domains and uses bulletproof hosting.

BlueNoroff hackers use fake "audio issues" on Teams calls to trick macOS users. The "fix" runs terminal commands that steal Keychains. Watch out.

New "directory shadowing" malware creates physical folders to hijack WordPress URLs. It feeds gambling spam to Googlebots while staying invisible.

GlassWorm malware found in Open VSX extensions. Hackers stole AWS & SSH keys from macOS devs using Solana C2. 22k+ downloads affected. Check your tools.

VirusTotal warns of massive supply chain attack on OpenClaw. Hackers use fake "skills" to deploy malware like Atomic Stealer. Verify your agents.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.

Notepad++ confirms update infrastructure was compromised by state-sponsored actors targeting specific users. Update to version 8.8.9 immediately.

Critical supply chain attack hits eScan antivirus. Hackers hijacked updates to install malware and disable the AV. Manual patch required.

Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.

New ClearFake malware uses fake CAPTCHAs & "ClickFix" tactics to trick users into pasting malicious code. 150k victims infected via blockchain.

Official EmEditor installer hijacked to push malware. This supply chain attack steals credentials & evades detection. Check your logs for these domains.

DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.
CISA adds 4 flaws to KEV, including critical Versa Concerto auth bypass (CVSS 9.2) & malicious "Prettier" package. Patch by Feb 12 to stop active attacks.