
 Do Son
A new ValleyRAT campaign targets English job seekers. The malware uses DLL sideloading via a trojanized Foxit PDF Reader executable to run a Remote Access Trojan and exfiltrate data.
malware

The malicious 'Crypto Copilot' Chrome extension drains Solana funds from traders on X by injecting hidden transfers. Remove this malware immediately.

Zscaler reveals Water Gamayun exploiting the MSC EvilTwin zero-day (CVE-2025-26633) via fake hiring lures to deploy stealthy backdoors.

Cybercriminals are using fake Battlefield 6 cracks and trainers to deploy infostealers. Avoid "InsaneRamZes" & "RUNE" torrents to protect your data.

Alert: Malicious Blender files are delivering StealC V2 infostealer. 3D artists downloading from free sites are at risk. Disable auto-run scripts now.

The official Xubuntu website was compromised, replacing the torrent download with a malicious Windows executable to steal data.
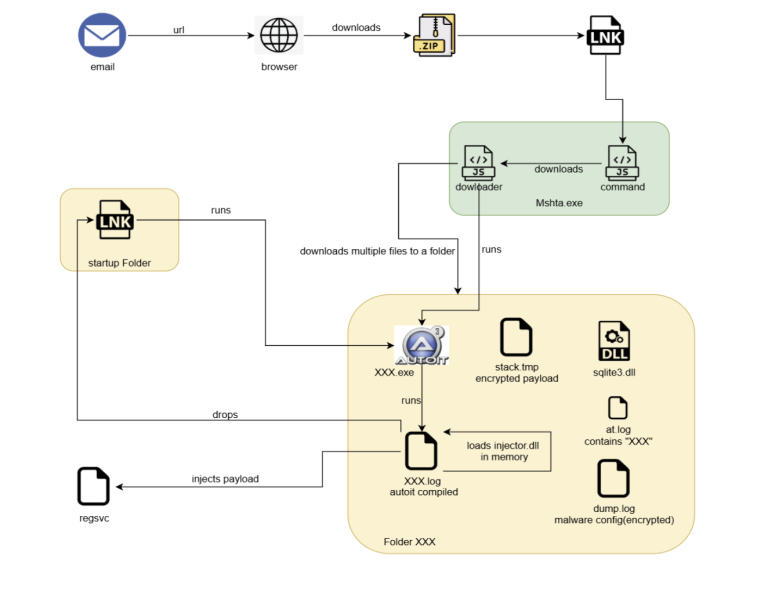
McAfee uncovered the Astaroth banking Trojan using GitHub for C2 backup, hiding encrypted configuration data via steganography in images to target Brazilian financial and crypto users.

Trend Micro uncovered "Water Saci," a self-propagating malware (SORVEPOTEL) that hijacks WhatsApp Web sessions to spread aggressively and steal Brazilian banking credentials.
WARMCOOKIE has resurfaced post-Operation Endgame with new execution handlers, a MaaS model, and evasive techniques like disguised scheduled tasks using company names.

The Detour Dog campaign is using DNS TXT records for stealthy C2, infecting thousands of websites and quickly shifting infrastructure to evade sinkholing efforts.

Patchwork APT has launched a new campaign in South Asia, exploiting DLL sideloading and obfuscation to deliver malware that masquerades as VLC media player for deep espionage.

NCSC exposes RayInitiator, a bootkit for Cisco ASA 5500-X devices without Secure Boot, which deploys the LINE VIPER shellcode loader for persistent and stealthy attacks.
Silent Push details how cybercriminals and APTs are misusing DDNS services for stealthy C2 servers, phishing, and malware delivery. Dozens of high-profile groups are involved.

The new infostealer Acreed is rapidly gaining market share post-Lumma takedown. It uses BNB Smart Chain and Steam profiles for C2, with a focus on crypto theft.

Olymp Loader, a new assembly-based MaaS, has emerged in underground markets. It's a turnkey solution for cybercriminals, with stealth and persistence features.

The TamperedChef malware campaign uses trojanized apps and digitally signed binaries to steal browser data. Attackers use SEO poisoning to trick users into downloading.
A new DarkCloud infostealer variant uses VB6 obfuscation and anti-analysis techniques to steal credentials and crypto wallets from MetaMask, Exodus, and more.

Huntress details a multi-stage attack that uses DLL sideloading and obfuscated Python to deliver PureRAT, a commercial-grade remote access trojan linked to PXA Stealer.

Security researcher Puja Srivastava from Sucuri uncovered two malicious files designed to guarantee persistent attacker access by...

A new DDoS-as-a-service botnet, ShadowV2, uses GitHub CodeSpaces and Docker to mimic legitimate cloud apps, bypassing traditional defenses and enabling powerful attacks.

Zscaler ThreatLabz has uncovered a new backdoor malware, YiBackdoor, that shares extensive code with IcedID and Latrodectus and is being tested for ransomware ops.

After nearly two years of silence, Zloader (a.k.a. Terdot, DELoader, or Silent Night) has returned with new...