
 Do Son
A new large-scale SEO poisoning campaign, "Operation Rewrite," uses the BadIIS module to hijack web servers, manipulate search results, and redirect users to scams.
malware

A new malicious npm package, "fezbox," hides a credential-stealing payload within a QR code, which it uses to exfiltrate web cookies and credentials.

A new BankBot campaign targets Android users in Indonesia and Vietnam. The malware uses spoofed app stores and a WebSocket-based download for stealth.

A new report reveals attackers are abusing ScreenConnect to deliver AsyncRAT and custom malware payloads, a serious supply chain risk for enterprises and MSPs.

A new technique, "EDR-Freeze," uses a built-in Windows feature to suspend antivirus and EDR processes, giving attackers a critical window to operate undetected.

CISA has released a new report detailing how attackers are exploiting Ivanti EPMM flaws to deploy malicious listeners and gain remote code execution.

CYFIRMA uncovers XillenStealer, a new Python-based, open-source malware on GitHub. Its built-in builder enables even novices to steal data and credentials.

GitLab Threat Intelligence reveals a new North Korean malware campaign using "ClickFix" social engineering to target new industries like crypto and retail.

A new, advanced FileFix attack campaign uses social engineering and steganography to hide malware in images, bypassing traditional security defenses.
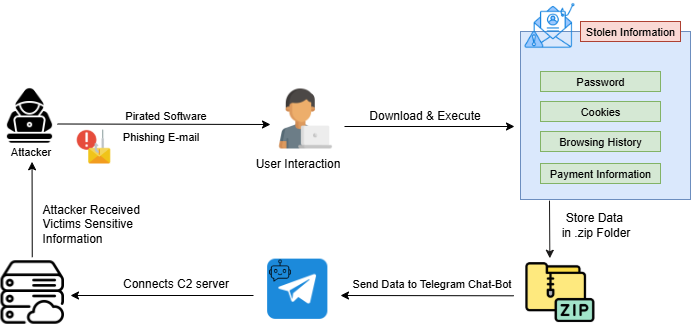
A new malware called Raven Stealer is emerging, targeting individuals and businesses by stealing credentials and data, and exfiltrating it via Telegram.

A new worm, Shai-Hulud, has compromised CrowdStrike’s NPM packages. The malware steals credentials and can spread rapidly across the developer ecosystem.
The Shai-Hulud supply chain attack has compromised multiple CrowdStrike npm packages, injecting malware to steal credentials and data.
A new APT28 campaign targets Ukraine's military with a blend of steganography, open-source tools, and legitimate cloud services for covert C2.

SmokeLoader is back. Despite a recent takedown, the malware loader returns with new versions, fixing bugs and adding advanced evasion tactics.

A new report uncovers the Pure malware family and its developer, PureCoder, highlighting an eight-day intrusion using the sophisticated PureHVNC RAT.

A sophisticated supply chain attack has compromised over 40 npm packages, including the popular TinyColor library, to steal developer credentials.

A new report reveals a multi-stage phishing campaign distributing DarkCloud Stealer. The malware hides its loader in a JPG file and injects code into MSBuild.exe for stealth.

A new report reveals Maranhão Stealer, a new malware targeting the gaming community through pirated software and cheats. It steals crypto, credentials, and data.

A new report reveals a malware campaign using SEO poisoning to target Chinese-speaking users. Attackers use fake software sites to deliver Hiddengh0st and Winos.

Researchers expose BaoLoader, a malware operation that has systematically used at least 26 code-signing certificates over seven years to appear legitimate and bypass security.

IBM X-Force reveals new findings on Hive0154, a China-aligned threat actor using an upgraded Toneshell backdoor and a new USB worm to target organizations.

Trend Micro reveals a new global malware campaign, EvilAI, that impersonates productivity and AI tools to infiltrate organizations and steal data.