
 Do Son
Protect yourself from the LummaC2 malware variant that uses Steam as a C2 server. Understand the techniques employed and the various channels
malware

FortiGuard Labs has recently identified a new phishing campaign deploying a variant of the notorious Agent Tesla malware

eSentire's Threat Response Unit (TRU) has unveiled a persistent and sophisticated cyber campaign employing the notorious more_eggs malware

A new and sophisticated malware named AsukaStealer has emerged on the cybercrime scene, offering its malicious services

attackers are leveraging an obscure WordPress plugin to install server-side malware, harvesting credit card details from WooCommerce online stores

Microsoft swiftly assigned the CVE-2024-30051 identifier to the vulnerability and released a patch during this month's Patch Tuesday

Attackers are weaponizing two critical vulnerabilities, CVE-2023-46805 and CVE-2024-21887, to spread the notorious Mirai botnet malware

Threat research team has recently uncovered sophisticated .NET managed code injection methods employed by the notorious AgentTesla malware

AhnLab Security Intelligence Center have revealed a growing trend of infostealer malware abusing the Electron framework

The expansion of the fake e-shop campaign to target 18 banks in Malaysia, coupled with its reach into Vietnam and Myanmar

A new report released by AhnLab Security Intelligence Center (ASEC) uncovers a disturbing tactic hackers are using to spread malware

A dangerous new malware named Planet Stealer is making its rounds in the cybercriminal underworld, and security experts warn

The payload delivered through this elaborate ruse is a Lua JIT malware, comprising a compiled LuaJIT executable and a batch script

The attackers hid malicious code in packages designed to mimic legitimate ones, using a technique called DLL sideloading to slip past security defenses

Bumblebee malware, known for its complexity and versatility, was initially a favored payload by cybercriminals from its inception

A formidable malware known as Glupteba has been lurking, evolving, and spreading its tentacles across the globe

Parrot TDS operates by embedding two types of scripts into web pages: a landing script that profiles potential victims and a payload script

A Linux-based malware family, DreamBus has been quietly evolving, honing its capabilities to exploit vulnerabilities in business applications
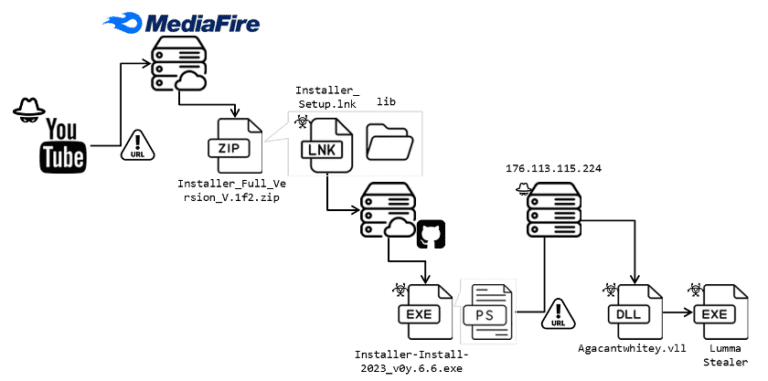
A cunning stratagem employed by a threat group, exploiting YouTube channels to disseminate a variant of the notorious Lumma Stealer malware.

JaskaGO malware checks whether it is operating on a virtual machine, and if so, performs a harmless task, like pinging Google, to avoid detection

Doctor Web's virus activity review revealed an 18.09% decrease in overall threats compared to October, with unique threats also diminishing by 13.79%

The malvertising campaign associated with PikaBot particularly targets Google searches for the remote application AnyDesk.