
 Do Son
Agenda ransomware (Qilin) is back, now using the advanced NETXLOADER and SmokeLoader to enhance infiltration and evade detection. Targets global sectors.
malware
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.

A large-scale supply chain attack has injected backdoors into e-commerce software, potentially affecting 500-1,000 stores. Sansec urges immediate checks.
California Man to Plead Guilty in Hack of Disney Employee, Theft of 1.1TB of Confidential Slack Data

California Man to Plead Guilty in Hack of Disney Employee, Theft of 1.1TB of Confidential Slack Data
Ryan Mitchell Kramer pleaded guilty to hacking Disney after using a fake AI art tool to steal 1.1TB of data. The attack involved malware and social engineering.

Recorded Future analysis exposes MintsLoader, a stealthy malware loader using advanced evasion to target industrial, legal, and energy sectors.

Socket discovers Python packages abusing Gmail SMTP for covert C2 tunnels, evading firewalls and exfiltrating data through trusted email infrastructure.

Sophos researchers detail a complex campaign using Cobalt Strike, DLL sideloading, and clever techniques like expired certificates

Cyfirma uncovers a Python-based RAT using Discord for command and control. It can lock screens, simulate BSOD, move the mouse, and steal data.
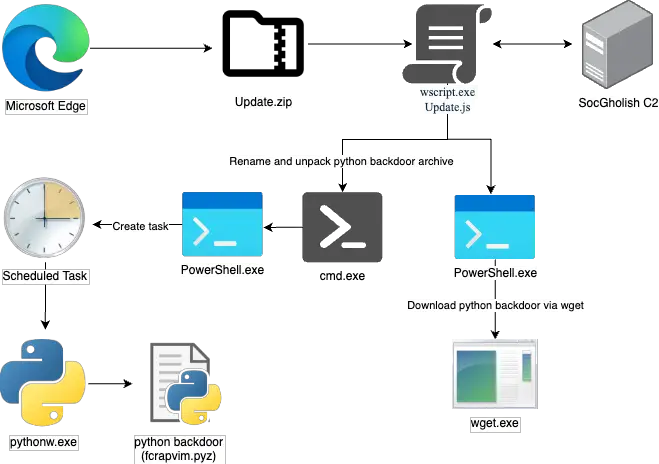
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

Silent Push uncovers Lazarus Group's campaign using fake crypto job offers to spread malware (BeaverTail, InvisibleFerret, OtterCookie), targeting job seekers.

Kaspersky uncovers "Operation SyncHole," a sophisticated cyber-espionage campaign by the Lazarus Group targeting critical South Korean sectors using advanced malware.

A new phishing campaign targets WooCommerce users with fake security alerts. Learn how attackers use IDN homographs and malicious plugins to compromise stores.

Kimsuky revives PebbleDash malware using spear-phishing and patched RDP DLLs for stealthy access and control, warns new ASEC March 2025 report.

A new phishing campaign delivers FormBook malware via Word docs, exploiting CVE-2017-11882. The fileless attack uses process hollowing to evade detection.

WormLocker ransomware is evolving! Discover how version 2.0 abuses system utilities to take over systems, as revealed by ANY.RUN analysis.

A deep dive into a sophisticated multi-stage malware attack using Cloudflare to deliver AsyncRAT. Learn how attackers evade detection and compromise systems.
Malicious open-source packages are stealing crypto wallet credentials! Learn about the threat and how to protect your seed phrases and private keys.
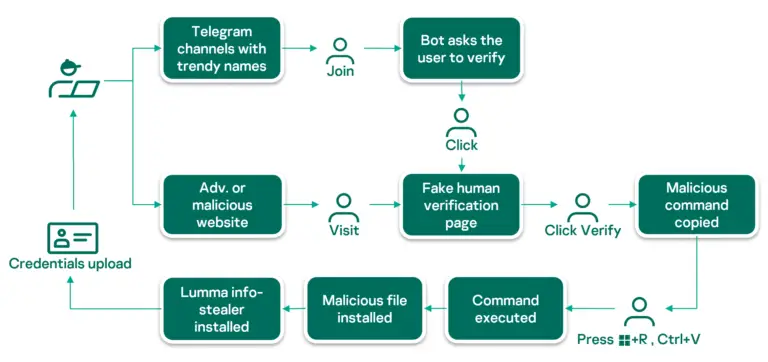
A deep dive into Lumma Stealer's sophisticated techniques: from fake CAPTCHAs to complex infection chains designed to evade detection and steal sensitive data.

A sophisticated backdoor attack targeting ViPNet networks in Russia has been uncovered. Kaspersky Labs reports on the malware and its impact on organizations.

Malicious npm packages are targeting Telegram bot developers, installing SSH backdoors and stealing data. Learn how this supply chain attack works and how to protect yourself.

RustoBot, a sophisticated botnet written in Rust, is exploiting vulnerabilities in TOTOLINK & DrayTek routers to launch DDoS attacks. Learn how this malware operates and how to protect your network.

The Billbug group targeted Southeast Asian organizations using advanced tools & DLL sideloading. This report details their sophisticated espionage campaign.