
 Do Son
Threat actors are using the PyBitmessage protocol as a stealthy C2 channel to hide a Monero coinminer and backdoor, evading detection.
malware

A malicious plugin is putting chatbot privacy at risk, silently stealing user messages. Is your Koishi bot compromised?

In-depth analysis of Skitnet malware: Rust, Nim, and DNS abuse. Discover how this sophisticated threat evades detection.

A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.

RVTools briefly hijacked in a Bumblebee malware supply chain attack. Learn how attackers used a trusted tool to deliver post-exploitation payloads.

A malicious PyPI package named 'solana-token' targeted Solana developers to steal code and secrets. Learn how it worked and how to stay safe.

North Korean threat actor TA406 intensifies cyber espionage against Ukraine, using phishing and malware to gather political intelligence.

Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.

New lightweight PupkinStealer malware silently steals browser data, messaging sessions, and desktop files, sending it all via Telegram.

Beware! Cybercriminals are using fake CAPTCHA pages to trick you into running commands that install the dangerous Lumma Stealer malware.

A massive, long-running proxy botnet using outdated IoT devices for criminal anonymity has been dismantled in a global law enforcement operation.

Sophisticated malware hides inside image files within .NET apps to secretly infect systems, targeting finance in Türkiye and logistics in Asia.

New email campaign uses tricky tactics and legitimate services to deliver the RATty Trojan in Spain, Italy, and Portugal. Stay alert for invoice scams!

Watch out! Sophisticated Facebook ads lure crypto users to download malware via fake platforms and celebrity endorsements. Bitdefender warns of data theft.

Cisco Talos warns of a Brazil-focused spam campaign abusing legitimate remote access tools (N-able, PDQ) to gain full system control. Stay vigilant!

The DOJ unsealed charges against four foreign nationals and the FBI seized domains for the Anyproxy and 5socks botnets, used to hijack routers globally.

Atomic Stealer malware is targeting macOS users, disguised as a cracked Evernote download, stealing passwords and data.

RedisRaider malware exploits misconfigured Redis servers to deploy cryptominers via cron jobs, evading detection with obfuscation and anti-forensics.

A sophisticated campaign deployed malicious IIS modules on South Korean web servers, enabling traffic control and backdoor access. Suspected Chinese actor.
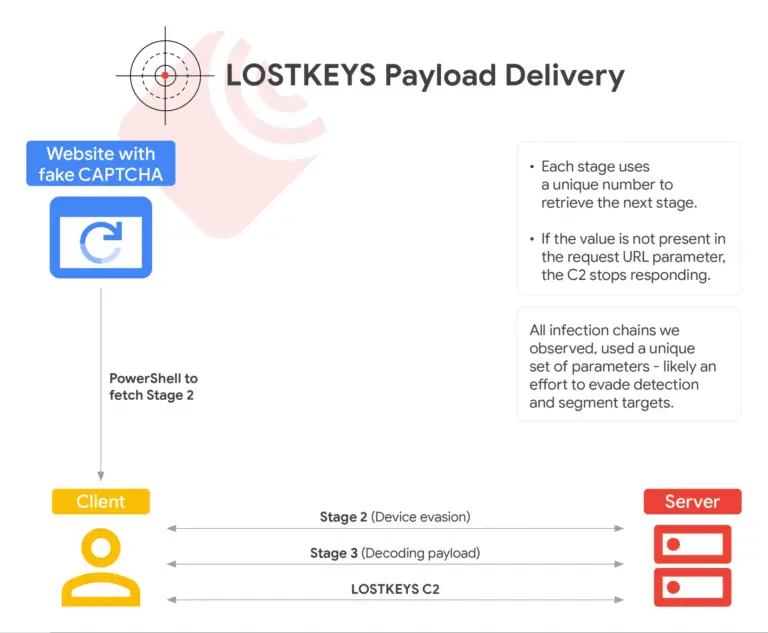
Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.