
 Do Son
Earth Lamia, a China-linked APT, is targeting critical industries worldwide using SQL injection, CVEs, and custom backdoors like PULSEPACK.
malware

AppleProcessHub, a new macOS infostealer, uses an Objective-C dropper and AES-decrypted C2 to steal sensitive files like SSH keys and Keychain.

A fake Google Meet page on compromised WordPress sites tricks users into manually running PowerShell commands, delivering remote access malware.

GhostSpy, a sophisticated Android RAT, uses Accessibility Services for full surveillance, data theft (including 2FA), and device control.

TA-ShadowCricket (formerly Shadow Force), a China-linked group, has been active for over a decade, targeting Asia-Pacific government and enterprise networks.

A new malware family, DOUBLELOADER, leverages the ALCATRAZ obfuscator to deploy RHADAMANTHYS infostealer with advanced evasion techniques.

An active npm malware campaign uses over 60 packages to steal internal/external IP addresses, hostnames, and user paths, designed for enterprise network mapping.

Russian-aligned TAG-110 (APT28) is launching a cyber-espionage campaign using macro-enabled Word docs to target Tajikistan's public sector for intelligence.

The alleged architect of the Qakbot malware empire, Rustam Rafailevich Gallyamov, has been indicted, facing charges and a $24M crypto seizure.

Over 40 malicious Chrome extensions, disguised as legitimate tools, are stealing cookies, logins, and impersonating users, many still live on the Web Store.

The "ClickFix" campaign tricks users with fake CAPTCHAs, leading them to paste malicious commands into the Windows Run dialog, delivering infostealers.

AI-generated TikTok videos are instructing users to run PowerShell commands, leading to the delivery of Vidar and StealC infostealer malware.

Malicious scripts disguised as Cloudflare human verification are embedded in WordPress themes, tricking users into executing PowerShell commands that deliver malware.

The U.S. Department of Justice charged 16 individuals for the $50M DanaBot malware operation, which infected over 300,000 computers worldwide.

Europol and Microsoft led Operation Endgame, a global takedown disrupting 300+ servers and 650 malicious domains linked to major ransomware malware strains.

The Rhadamanthys stealer is back with targeted phishing attacks across Central and Eastern Europe, using fake copyright infringement lures.

A new, deeply stealthy formjacking malware is targeting WooCommerce, secretly stealing customer payment data from legitimate checkout processes.

Malicious npm packages have been silently destroying files and corrupting data in React, Vue.js, and Vite projects for over two years.

Deceptive VS Code extensions like 'solaibot' are stealing crypto wallet credentials, disabling Defender, and deploying persistent spyware on Windows.

The notorious Genesis Market is back! A new campaign deploys a malicious browser extension via Lumma Stealer to covertly harvest user data.

Global operation neutralizes Lumma Stealer, infecting hundreds of thousands of PCs. Europol & Microsoft seized over 1,300 malicious domains.
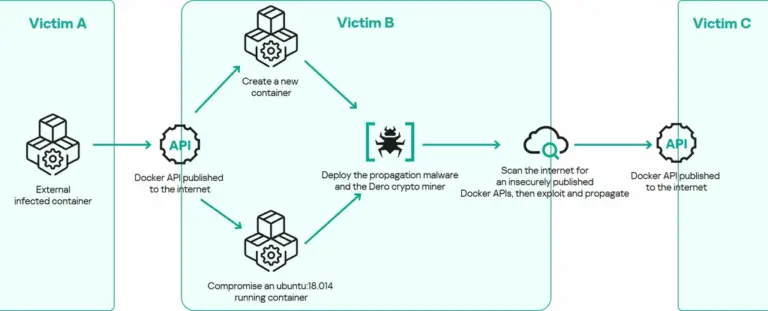
A new self-replicating Dero cryptominer is infecting exposed Docker containers, spreading as a worm without needing a C2 server.