
 Do Son
Shadow Vector campaign uses malicious SVGs in phishing emails to deliver AsyncRAT & RemcosRAT in Colombia, leveraging advanced DLL sideloading and in-memory execution.
malware

The SERPENTINE#CLOUD campaign exploits Cloudflare Tunnel subdomains and LNK files to deliver in-memory RATs like AsyncRAT and Remcos, evading detection.

Hunt.io researchers uncovered dozens of malicious Android apps disguised as popular programs on open servers, which are fronts for SpyNote spyware, harvesting sensitive user data.

Amatera Stealer, a rebranded and enhanced version of ACR Stealer, uses advanced evasion tactics like NTSockets and WoW64 syscalls to steal data from browsers, crypto wallets, and apps.

Banana Squad has compromised over 60 GitHub repos with malicious Python files, using UI quirks to hide malware and steal data from developers via a sophisticated supply chain attack.

A new campaign, "Stargazers Ghost Network," weaponizes Minecraft mods on GitHub to distribute a multi-stage infostealer, targeting user credentials and crypto wallets.

Silver Fox APT is conducting a multi-stage espionage campaign, leveraging backdoored medical software like Philips DICOM viewers to infect healthcare organizations

A C++ backdoor named Pickai is actively exploiting ComfyUI servers, compromising nearly 700 AI image generation hosts and posing a supply chain risk
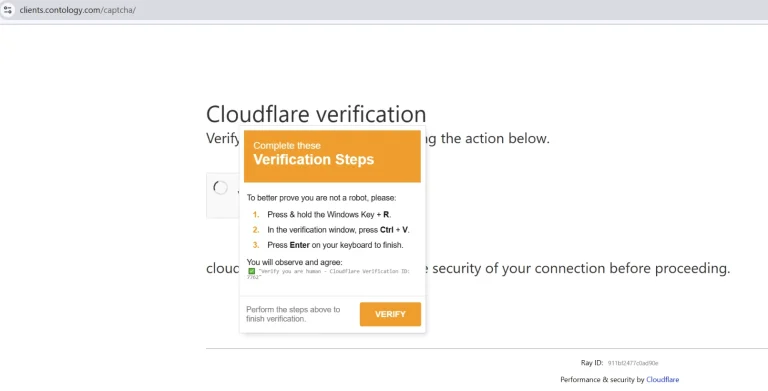
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

XDSpy, a covert cyber-espionage group, is back with a sophisticated campaign targeting governments, leveraging an obscure Windows LNK file parsing flaw and new XDigo malware
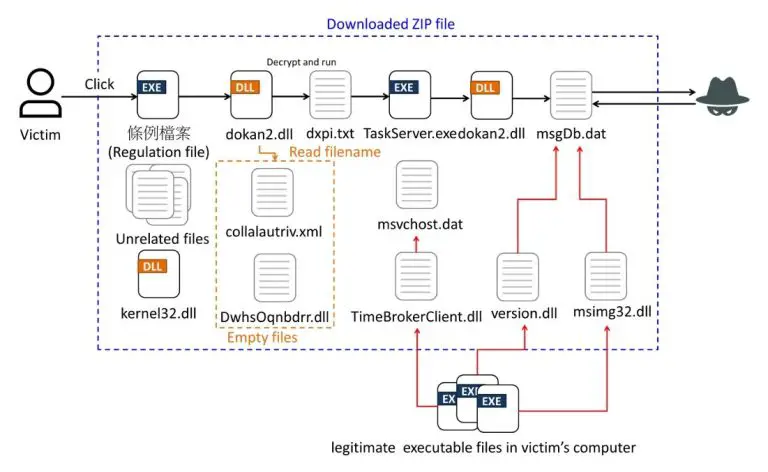
A sophisticated malware campaign is targeting Taiwan, impersonating the National Taxation Bureau to distribute Winos 4.0, HoldingHands RAT, and Gh0stCringe.

KimJongRAT is back with new PE and PowerShell variants, using LNK files and CDNs to steal browser, email, and over 30 crypto wallet details from victims.

Team46 (TaxOff) is exploiting a Google Chrome sandbox escape zero-day (CVE-2025-2783) to deploy the multi-layered Trinper malware via phishing campaigns

Water Curse is using GitHub to distribute malicious open-source projects, weaponizing 76 accounts with multi-stage malware targeting developers, red teamers, and gamers.

Malicious phishing apps are bypassing Google Play Store security, tricking users into revealing crypto wallet seed phrases and draining funds. Beware and never share your seed

Katz Stealer, a new stealthy MaaS, is actively stealing data from browsers, crypto wallets, and apps, using advanced evasion tactics like steganography and Discord hijacking.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

Infoblox unmasks VexTrio, a sprawling malicious adtech ecosystem intertwined with DNS-based malware campaigns and global website compromises, fueled by commercial operators
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

Spectra Ransomware, an evolution of Chaos, encrypts Windows files with AES-RSA, demands $5,000 in Bitcoin, and uses double extortion tactics with system evasion

HelloTDS is a sophisticated traffic direction system delivering millions to FakeCaptcha and other malware via advanced fingerprinting and evasive tactics.