
 Do Son
Interpol and Asian law enforcement blocked 20,000 malicious IPs and seized 41 servers in a major takedown of information-stealing malware infrastructure.
malware

CyberEye, a modular .NET RAT, offers widespread data theft and surveillance using a builder, Telegram C2, and anti-analysis features, making it a new threat.

A Insyde H2O UEFI flaw (CVE-2025-4275) allows Secure Boot bypass via NVRAM, enabling attackers to inject undetectable malware and rootkits. Update firmware now!

A UEFI Secure Boot flaw (CVE-2025-3052) allows attackers to bypass security and execute untrusted code on millions of devices. Patch now!

Stealth Falcon APT is exploiting a Windows WebDAV zero-day (CVE-2025-33053) in a sophisticated cyberespionage campaign targeting defense entities in the Middle East & Africa.

Kimsuky's AppleSeed campaign targets Korean Facebook, email, and Telegram users with evolved social engineering and stealthy malware.

APT41 is leveraging Google Calendar as a covert C2 channel in a new multi-stage malware campaign targeting a Taiwanese government website.

Beware 'imad213,' a fake Instagram booster stealing credentials via social engineering and bot services. Learn how to protect your account.

ESET uncovers BladedFeline, an Iran-aligned APT group, targeting KRG, Iraq, and Uzbekistan in a sophisticated cyberespionage campaign.

A new info-stealer, SoraAI.lnk, is leveraging OpenAI's Sora popularity to infect users. Learn how this sophisticated malware works and how to protect your data.

CYFIRMA uncovers DuplexSpy, a powerful C# RAT on GitHub with surveillance, persistence, and anti-analysis features, posing a significant cybercrime threat.

Two malicious npm packages, express-api-sync and system-health-sync-api, act as remote-controlled time bombs, wiping entire directories with a single POST request.

An old Microsoft Office vulnerability (CVE-2017-0199) is being exploited in a new phishing campaign to deploy the FormBook infostealer malware. Update now!

A new Mirai botnet variant is exploiting CVE-2024-3721 to infect vulnerable DVRs. Learn how this sophisticated attack works and if your surveillance system is at risk.

Proofpoint reveals TA397 (Bitter APT) is an India-aligned state-backed group conducting long-term espionage campaigns globally, targeting rivals and partners.

LayerX found "sleeper agent" Chrome extensions, installed on 1.5M devices, disguised as audio tools but capable of remote command execution and data theft.

ViperSoftX, a stealthy malware, is actively spreading via fake software to steal cryptocurrency and enable remote control, affecting users globally.

A new AMOS macOS stealer variant is using typo-squatted Spectrum domains in a clever cross-platform social engineering campaign. Stay vigilant!

Sophos X-Ops found a backdoored Sakura RAT targeting hackers and cheaters, spreading info-stealers via hidden scripts in open-source projects.
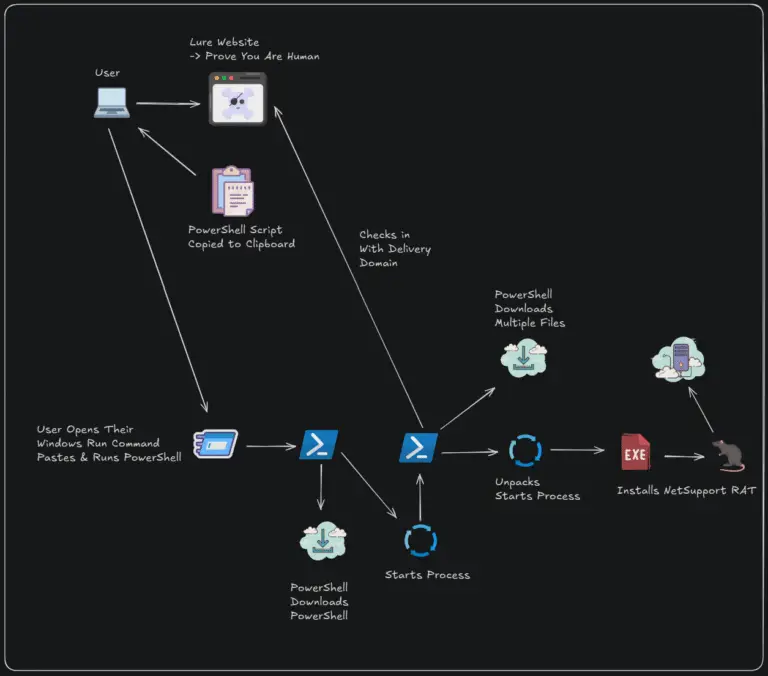
A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

IBM X-Force warns of a new phishing campaign by Hive0131 targeting Colombian users with DCRat malware via fake legal notices.

K7 Labs details an evolved PowerShell malware, ViperSoftX 2025, featuring enhanced modularity, stealth, and persistence for advanced attacks.