
 Do Son
ASEC report details Kimsuky's Larva-24005 campaign targeting South Korea and globally with RDP exploits, MySpy malware, and keyloggers.
malware

Kaspersky reports the resurgence of IronHusky APT, deploying an evolved MysterySnail RAT in espionage campaigns.

Unit 42 uncovers a sophisticated phishing campaign using multi-layered tactics to deliver malware like Agent Tesla, evading detection.

HarfangLab analysis details Gamaredon's PteroLNK malware, revealing its stealthy tactics and infrastructure used for espionage.

Sekoia TDR reveals Interlock ransomware's evolving tactics, including ClickFix social engineering, to evade detection and steal data.
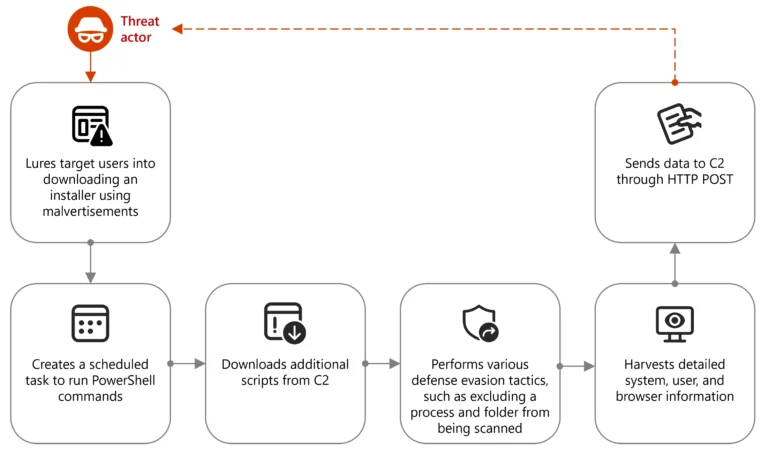
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

New attack campaign uses Microsoft Teams phishing and a novel TypeLib COM hijacking technique for persistence, targeting finance sector.

LummaStealer evolves into a sophisticated Malware-as-a-Service, using stealth and advanced techniques to steal data.

Discover Waiting Thread Hijacking, a novel process injection technique that bypasses EDR systems. Learn how it stealthily executes code in remote processes.
A new campaign by Chinese threat actor UNC5174 uses the VShell RAT. Sysdig TRT reports on the group's shift to open-source tools and evasion tactics.

Kandji's research uncovers PasivRobber, a sophisticated macOS malware suite targeting user data. Learn about its deceptive tactics and capabilities.

CloudSEK's report reveals how fake PDF converters use social engineering to spread malware. Learn how these malicious sites deceive users and steal data

Trend Micro uncovers BPFDoor backdoor used in cyberespionage across Asia and the Middle East, attributing it to the Red Menshen APT group

NVISO's report details BRICKSTORM, a China-linked backdoor targeting European industries, using sophisticated techniques to evade detection

Learn about ResolverRAT, a new remote access trojan using advanced evasion to avoid detection. This malware employs sophisticated techniques.

The Knownsec 404 team reports on the DarkHotel APT group's latest attacks, featuring upgraded frameworks and sophisticated evasion techniques.

Sucuri discovered a credit card skimming attack using a fake font domain to steal credit card data from a WordPress website.
The NCSC reveals DAMASCENED PEACOCK, a sophisticated malware targeting the UK MOD, using spear-phishing, code signing, and COM Hijacking.

North Korean threat group Slow Pisces targets crypto developers with fake job offers and malicious coding challenges. Learn how they steal millions

GOFFEE APT is actively targeting Russian organizations with updated tactics, including the new PowerModul implant, sophisticated spear phishing, and lateral movement via custom Mythic agents

ViperSoftX malware is being used by Arabic-speaking attackers to target South Korea, according to ASEC. This malware uses PowerShell and spreads through torrents, delivering PureCrypter and Quasar RAT

BI.ZONE Threat Intelligence reports Sapphire Werewolf using updated Amethyst stealer malware to target energy companies, employing advanced evasion techniques.Sources and related content