
 Do Son
The SideCopy APT group is evolving its tactics, using new methods like MSI packages and custom malware to target critical Indian sectors, including railways and oil & gas
malware

A new report reveals Russia-linked Shuckworm's evolved cyber campaign targeting a military mission in Ukraine, featuring sophisticated malware and stealthy tactics.

A Silent Push report details the evolving tactics of the Scattered Spider hacker collective, including new phishing kits, the Spectre RAT, and targeting of major brands in 2025.

A new "Pick Your Poison" phishing campaign tricks users into choosing between having their credentials stolen or infecting their systems with malware. Cofense analysis reveals how this double-edged attack uses files.fm to deliver malicious payloads.
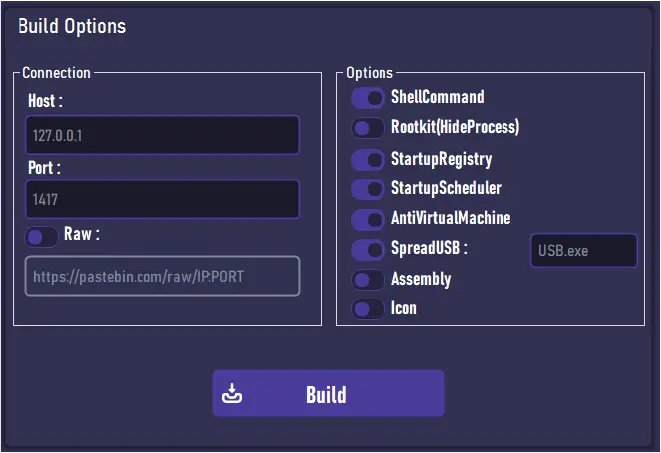
CYFIRMA researchers discovered Neptune RAT, an advanced Remote Access Trojan targeting Windows. Learn about its destructive features, evasion techniques, and distribution methods.

Vidar Stealer malware is distributed by masquerading as BGInfo.exe, exploiting expired signatures and file discrepancies to evade detection

Attackers are using SourceForge to distribute malware, including a ClipBanker Trojan and a cryptocurrency miner, disguised as a Microsoft Office enhancement suite.

The Grandoreiro banking trojan is being spread through phishing campaigns. Learn about the attack methods and how to stay safe.

Uncover the reverse shell threat. Malicious packages on npm can infect local installations through hidden techniques and scripts.
Uncover the tactics of the CNC group in Operation Sea Elephant targeting academic and research institutions in South Asia.

Explore the Yokai backdoor malware campaign targeting the Royal Thai Police in a detailed report by Cado Security Labs.

Learn about CoinMiner Malware and how it is distributed via USB devices to secretly mine cryptocurrency on victims' computers.

Uncover the details of RedDelta: A sophisticated cyber-espionage group targeting political and government entities in Asia.
Discover the alarming rise of cyber threats in Hong Kong. Find out about the most common types of attacks and how to safeguard your online security.
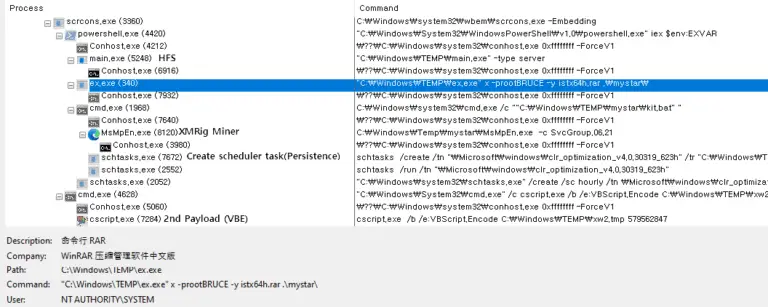
ASEC reveals the increasing sophistication of cybercriminals distributing XMRig malware through Binary Managed Object Files. Stay informed about this threat.

Beware of PG_MEM: a new malware targeting PostgreSQL. Learn how this sophisticated threat exploits and mines cryptocurrency.

Uncover the details of Cyclops, a new malware developed by the APT 35 group. Learn about its capabilities, targets, and method of operation.

Discover the alarming truth about malicious extensions and how they are being used to compromise user's browsers and steal sensitive data.

Learn about the RHADAMANTHYS malware, a sophisticated infostealer posing a significant threat to organizations and individuals in Israel.

Learn about Mint Stealer, a sophisticated malware designed to steal confidential data. Find out how it operates and the techniques it uses to bypass security measures.

Beware of Sora AI malware! Cybercriminals are exploiting the buzz around OpenAI's upcoming AI model to distribute phishing sites and malicious software.

Discover the latest cybersecurity trends affecting SMBs. Find out about the surge in malware infections and the favored tactics used by cybercriminals.