Google Uncovers LOSTKEYS Malware Used by Russian COLDRIVER for Cyber Espionage
 Do Son
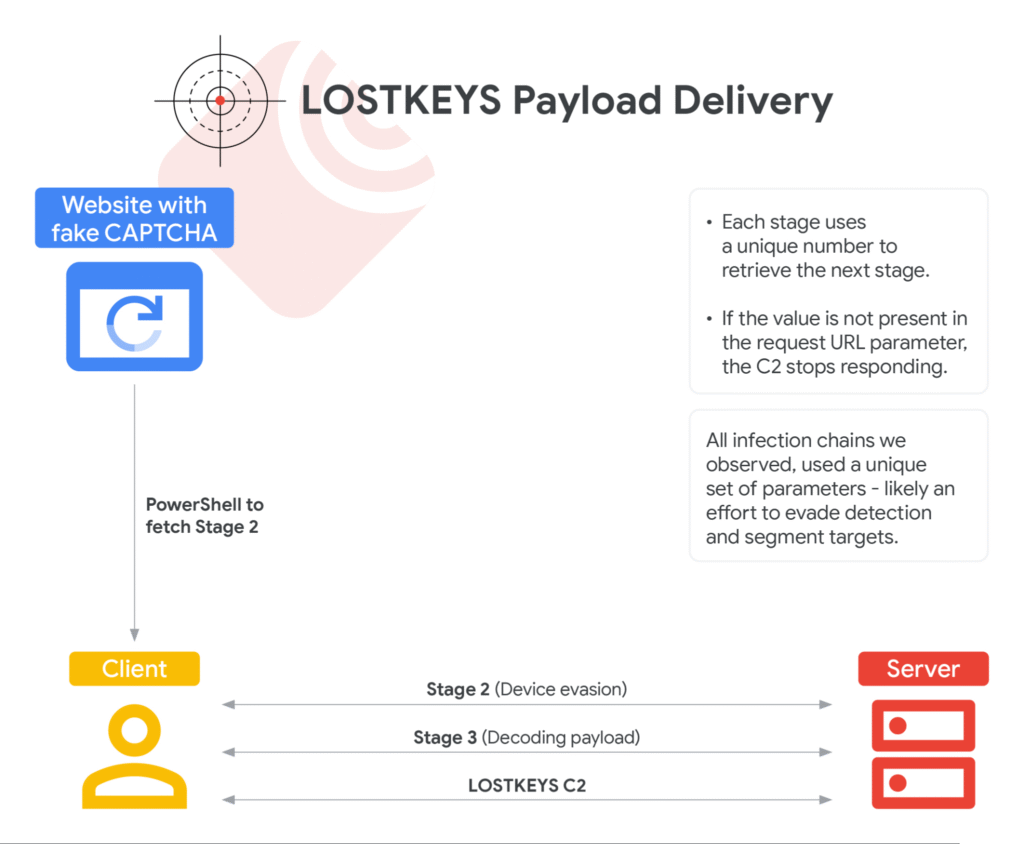
Image: Google Threat Intelligence Group
In a concerning escalation of cyber-espionage activity, Google’s Threat Intelligence Group (GTIG) has revealed the emergence of a new malware tool named LOSTKEYS, developed and deployed by the Russian state-backed threat actor COLDRIVER—also tracked as UNC4057, Star Blizzard, and Callisto.
“LOSTKEYS is capable of stealing files from a hard-coded list of extensions and directories, along with sending system information and running processes to the attacker,” GTIG wrote.
COLDRIVER is no stranger to Western cybersecurity circles. Known for targeting high-profile individuals—such as advisors to NATO governments, journalists, and non-governmental organizations—the group has now expanded its operational playbook beyond phishing.
Google’s report highlights that “the group has also continued targeting individuals connected to Ukraine,” and their activities are “in support of Russia’s strategic interests.” The malware delivery starts with a fake CAPTCHA page, a classic social engineering lure that tricks victims into copying and executing PowerShell commands—a technique colloquially known as ClickFix.
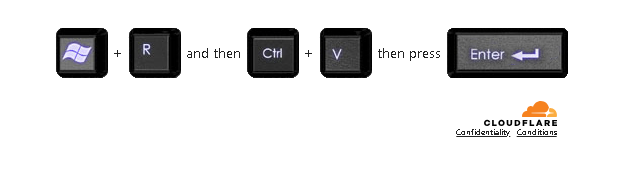
“Once the CAPTCHA has been ‘verified,’ PowerShell is copied to the users clipboard and the page prompts the user to execute the PowerShell via the ‘run’ prompt in Windows,” GTIG explains.
The infection chain unfolds across three stages:
- Stage 1: A PowerShell script copied by the victim fetches and runs the next stage from a remote server (165.227.148[.]68).
- Stage 2: Device evasion logic checks if the system is running in a virtual environment by calculating the MD5 hash of screen resolution. If a match is found in a hardcoded list, execution halts.
- Stage 3: A Base64-encoded blob decodes into more PowerShell, which retrieves two final files—a Visual Basic Script (the decoder) and an encoded payload. These use a substitution cipher with unique keys to decode the final malware.
Google provided a Python script that security analysts can use to reverse-engineer the final payload.
The final stage delivers LOSTKEYS, a stealthy Visual Basic Script capable of stealing sensitive files, exfiltrating system metadata, and monitoring running processes. It targets specific file types and directories hardcoded into its logic.
“LOSTKEYS is designed to achieve a similar goal [to COLDRIVER’s previous SPICA malware] and is only deployed in highly selective cases,” the report says.
In contrast to SPICA, LOSTKEYS appears optimized for document theft, signaling a potential shift in COLDRIVER’s operational intent—from email exfiltration to broader system reconnaissance and document collection.
Intriguingly, Google researchers discovered earlier LOSTKEYS samples from as far back as December 2023, disguised as Maltego installers. While these Portable Executable (PE) files differ from the newer VBS-based chain, their ultimate payload is the same. Whether these samples are directly tied to COLDRIVER or repurposed by another actor remains under investigation.
To protect at-risk users, GTIG urges enrollment in Google’s Advanced Protection Program, use of Enhanced Safe Browsing in Chrome, and strict device patching policies. Enterprise environments are advised to adopt least privilege principles and block unauthorized script execution.
“Users should exercise caution when encountering a site that prompts them to exit the browser and run commands on their device,” GTIG warns.
Related Posts:
- Google: Zero-Day Exploits Shift from Browsers to Enterprise Security Tools in 2024
- CVE-2024-10205: Critical Authentication Bypass Flaw Found in Hitachi Infrastructure Analytics Advisor and Ops Center Analyzer
- DPRK IT Workers: A Global Threat Expanding in Scope and Scale
- NATO member diplomatic office in Kiev has been attacked by hackers
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
