 Do Son
Mandiant and GTIG detailed how Russian COLD RELIC phishing and COLD RELIC phishing attacks use stolen cloud rosters and passkeys to breach partners.
Star Blizzard
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.

NCSC warns high-risk individuals of Russian and Chinese state actors hijacking WhatsApp and Signal. Protect your chats with these essential 2026 defense tips.

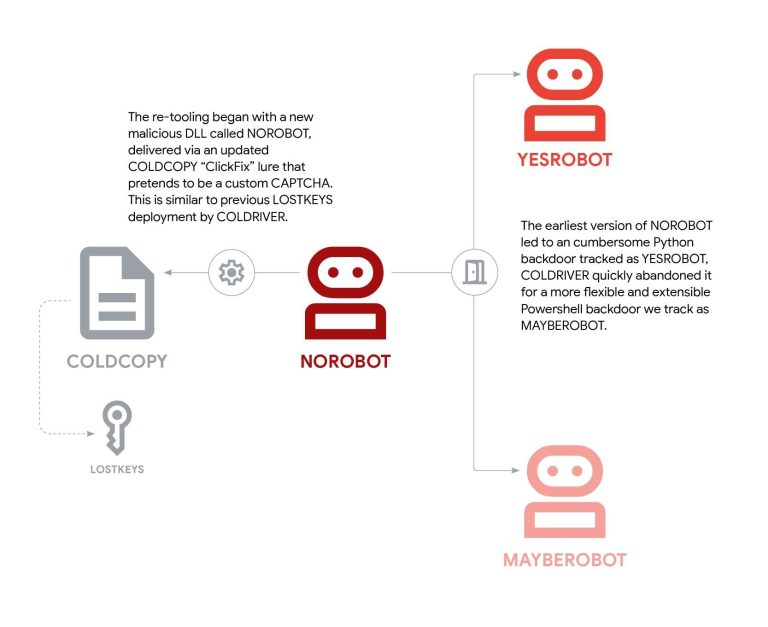
Russia-linked APT COLDRIVER is using a new multi-stage malware campaign (BAITSWITCH/SIMPLEFIX) with a ClickFix lure to target journalists and activists for espionage.
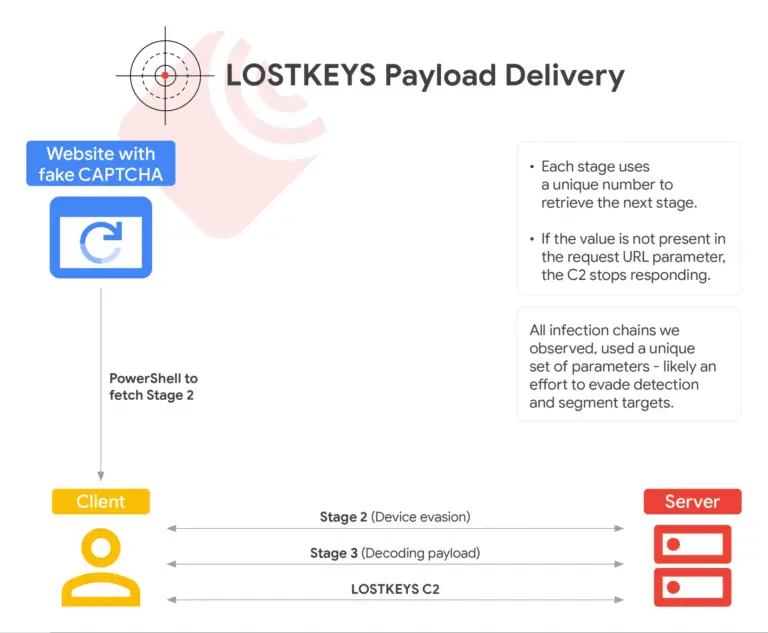
Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.

Uncover the latest spear-phishing campaign by the Russian threat actor Star Blizzard targeting WhatsApp accounts.

Justice Department announcement: 41 internet domains seized in cyber fraud and espionage linked to Russian intelligence agents.

The Russia-based threat group known as Star Blizzard has been operating in the shadows, launching sophisticated spear-phishing attacks