
 Do Son
North Korean APT Kimsuky is evolving its ClickFix tactics, using deceptive social engineering, fake job portals, and obfuscated PowerShell to compromise targets via spear-phishing campaigns.
ClickFix

CYFIRMA uncovers "Odyssey Stealer," a new macOS malware using fake App Store prompts & typosquatting to steal crypto wallets, passwords, and browser data from Western users.

DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.

Amatera Stealer, a rebranded and enhanced version of ACR Stealer, uses advanced evasion tactics like NTSockets and WoW64 syscalls to steal data from browsers, crypto wallets, and apps.
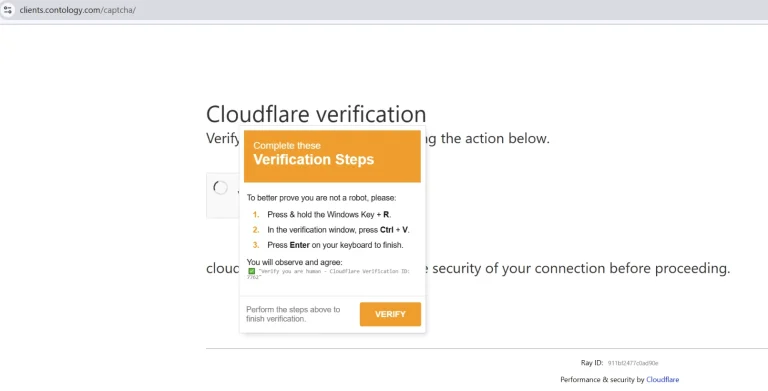
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

A fileless AsyncRAT campaign, dubbed "Clickfix," targets German-speaking users, luring them into executing obfuscated PowerShell payloads via fake verification prompts.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

A sophisticated "ClickFix" phishing campaign uses fake Booking.com CAPTCHAs to deliver RATs and info stealers to the hotel and travel industry.

The "ClickFix" campaign tricks users with fake CAPTCHAs, leading them to paste malicious commands into the Windows Run dialog, delivering infostealers.
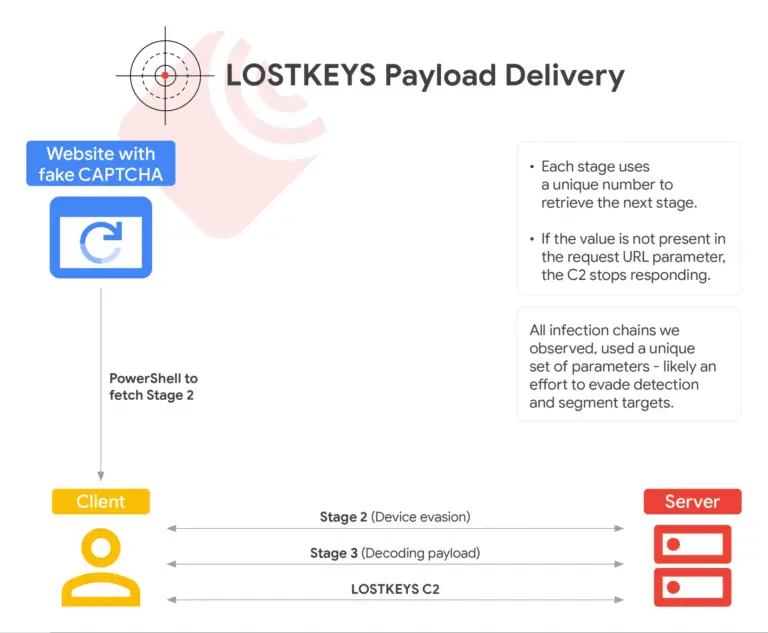
Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.

State-sponsored hackers from North Korea, Iran, and Russia are now using ClickFix, a cybercrime-born social engineering trick.

Sekoia TDR reveals Interlock ransomware's evolving tactics, including ClickFix social engineering, to evade detection and steal data.

Uncover the latest findings on a Pakistan-Linked APT targeting Indian users with sophisticated malware distribution tactics.

Uncover the latest variant of ClearFake malware, EtherHiding, exploiting Web3 features for advanced malicious tactics.

Stay informed about Booking Phishing schemes. Discover how attackers use social engineering to steal credentials in this campaign.
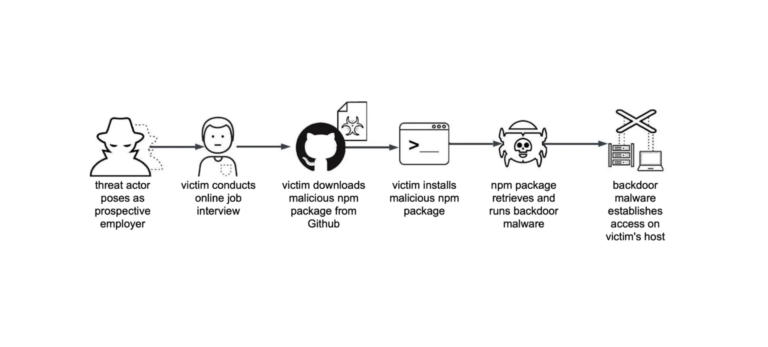
Uncover the dangers of Lazarus Group’s Infostealer Malware targeting software developers and IT professionals with malicious scripts.

Discover the latest evasion tactic used by cybercriminals: the ChaCha20 cipher in Lumma Stealer malware. Stay informed and protected against evolving threats.
Uncover the ClickFix Technique and its use by North Korea's Lazarus APT group. Learn how this advanced social engineering method targets job seekers.
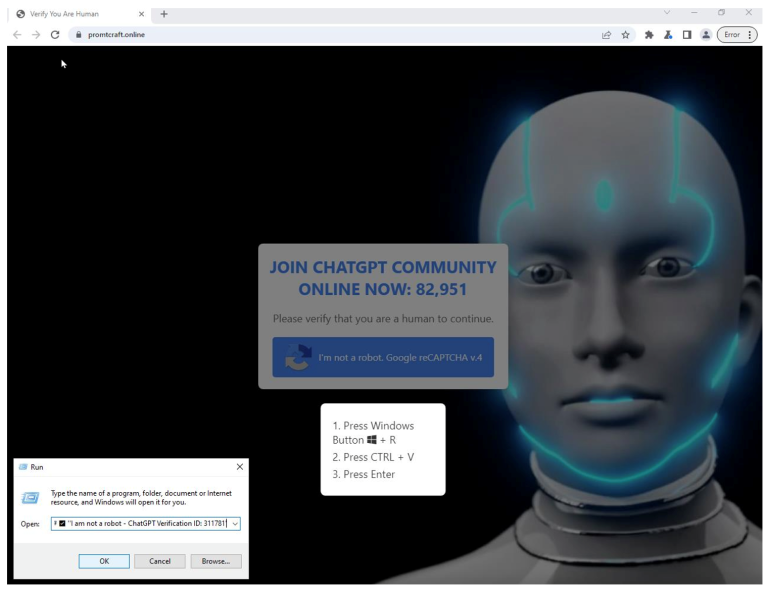
Discover the alarming rise of ClickFix, a unique social engineering method used to spread malware. Learn how it exploits human behavior and how to protect yourself.