 Do Son
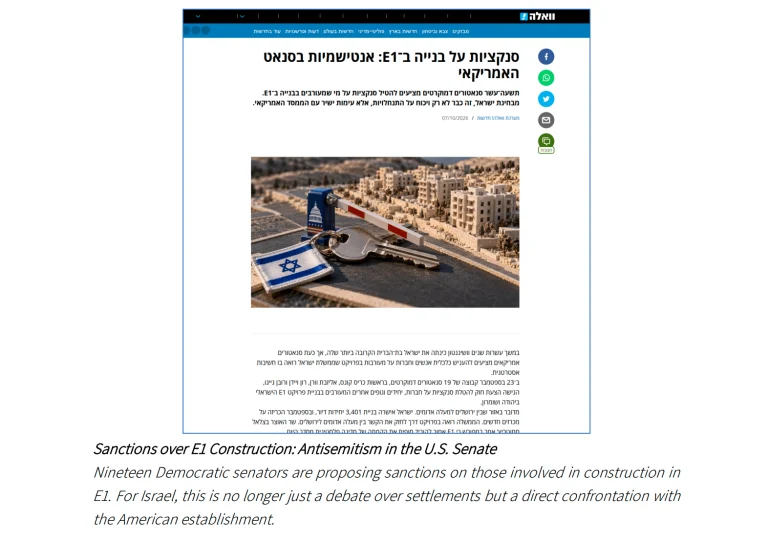
ClearSky exposed the Russian Doppelganger campaign in Israel using 76 fake Walla articles, 66 redirect domains, and AI poisoning ahead of elections.
russia
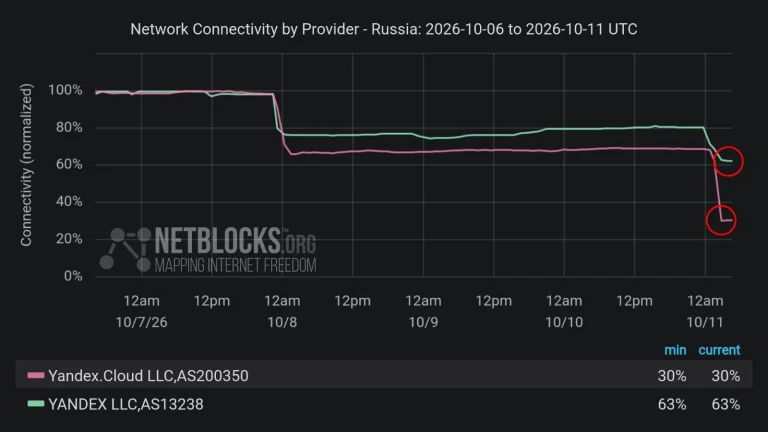
A recent Yandex Cloud drone strike in Vladimir caused severe service outages across Russia, disrupting Yandex Pay, search, and enterprise cloud operations.
CoreRAT malware powers Core Werewolf attacks on Russian defense and government targets, using fake military PDFs and Telegram phishing.
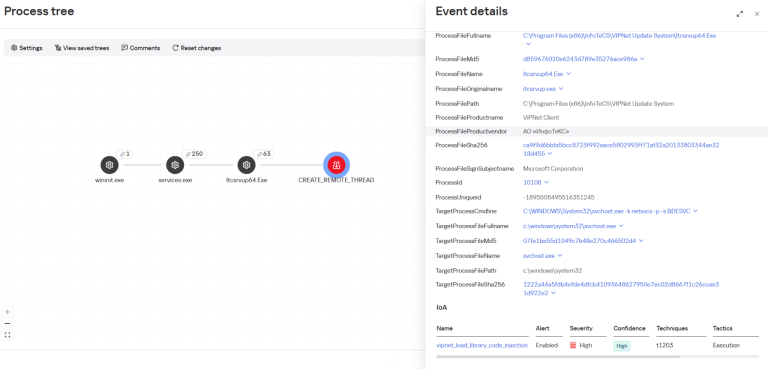
The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.
A 20-nation alert warns that Russia's FSB Center 16 is hacking vulnerable routers. The group targets critical infrastructure through weak SNMP settings.
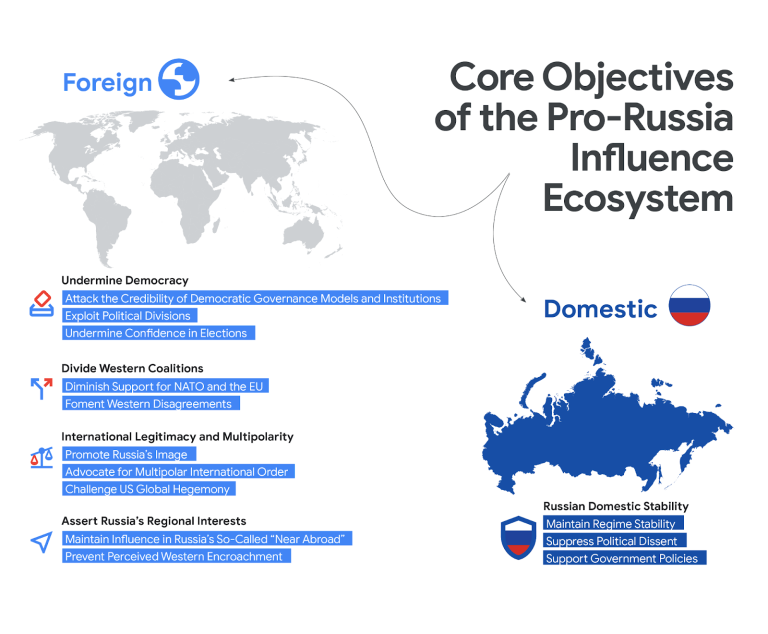
The pro-Russia influence ecosystem is expanding information operations beyond Ukraine. Discover how global targets face new cyber threats and AI tactics.
Apple removes Russian apps VK and MAX from the App Store without explanation, prompting Kremlin demands and push notification cutoffs.
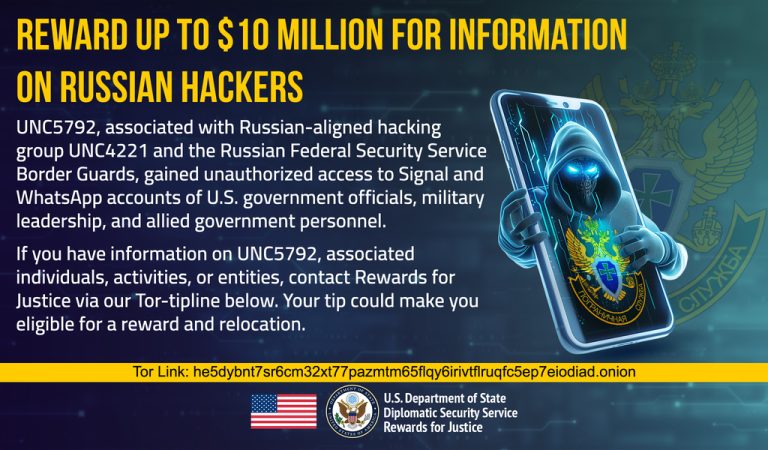
The U.S. offers a $10 million reward for UNC5792, a Russian FSB-linked group behind Signal and WhatsApp phishing of officials.
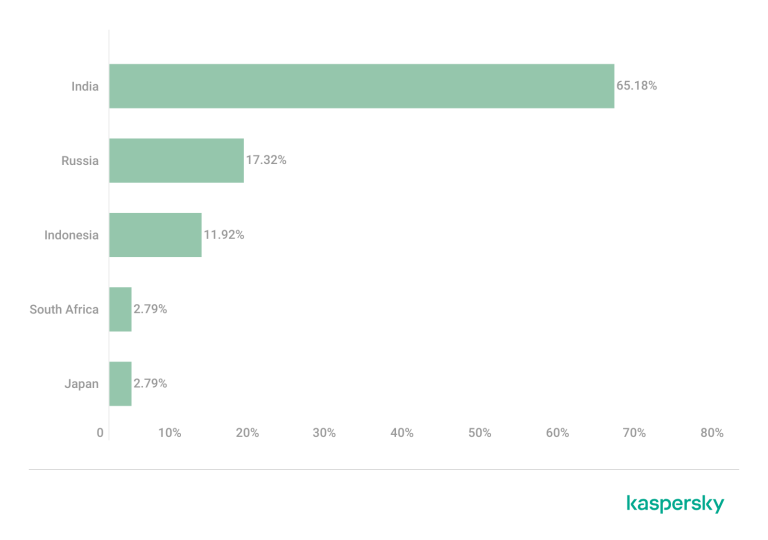
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.

Apple officially ceases all payment services in Russia as of April 1, 2026. Subscriptions, App Store buys, and iCloud+ renewals are now indefinitely frozen.
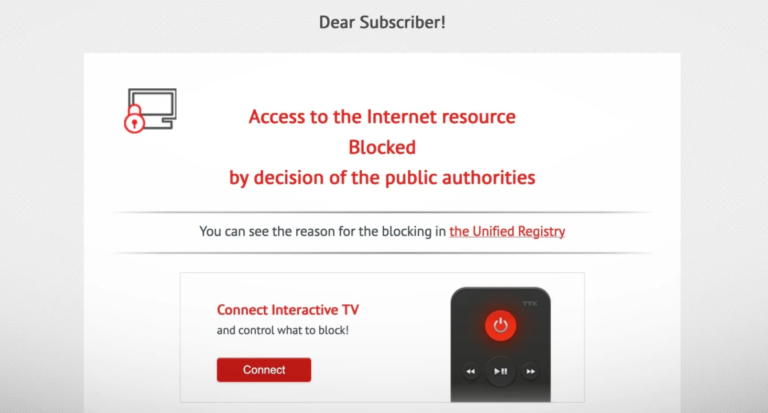
Russia’s Roskomnadzor has blocked Archive.today using DPI technology, while Wikipedia has banned the site over hidden DDoS code. Is the paywall-killer dead?
Russian national Aleksei Volkov was sentenced to 81 months in prison and ordered to pay $9.1M for his role as an access broker in major U.S. ransomware attacks.

Recorded Future’s Insikt Group warns of a two-year escalation in Russian hybrid warfare. From cyber sabotage to airspace incursions, NATO faces a new doctrine.

APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.

Intezer reveals EchoGather, a new Paper Werewolf backdoor using XLL files and AI-generated decoys to target Russian defense and high-tech firms.

Operation MoneyMount-ISO targets Russian financial institutions with a Phantom Stealer info-stealer hidden in an ISO file. The malware steals crypto wallets, browser data, and uses a keylogger. It has a SelfDestruct function for evasion.

Russia imposed a network-level blockade on Apple's encrypted FaceTime service, citing its alleged use for coordinating fraud and terrorist attacks, making the app unusable.
SEQRITE exposed Operation DUPEHIKE targeting Russian HR with a malicious LNK bonus lure. The DUPERUNNER implant uses PowerShell and process injection into explorer.exe to deploy the Adaptix C2 Beacon.

Arctic Wolf Labs reveals Russian GRU Unit 29155 using SocGholish to deploy RomCom malware against a US firm with ties to Ukraine.
Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam

Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam
Zimperium found 760+ Android apps exploiting NFC/HCE to steal payment data. The malware impersonates 20 banks across Russia, Poland, and Brazil, using Telegram for criminal coordination.

SEQRITE exposed CAPI, a .NET trojan targeting Russian FinTech with malicious LNK resumes. It uses rundll32 for execution and a hidden "Security" scheduled task for persistence.

Resecurity exposed Qilin RaaS's reliance on bulletproof hosting (BPH) in Russia/HK. The same network was linked to the Asahi Group Holdings ransomware attack that stole 27 GB of data.