Doppelganger Campaign Targets Israel Elections With Fake News and AI Poisoning
 Do Son
TL;DR
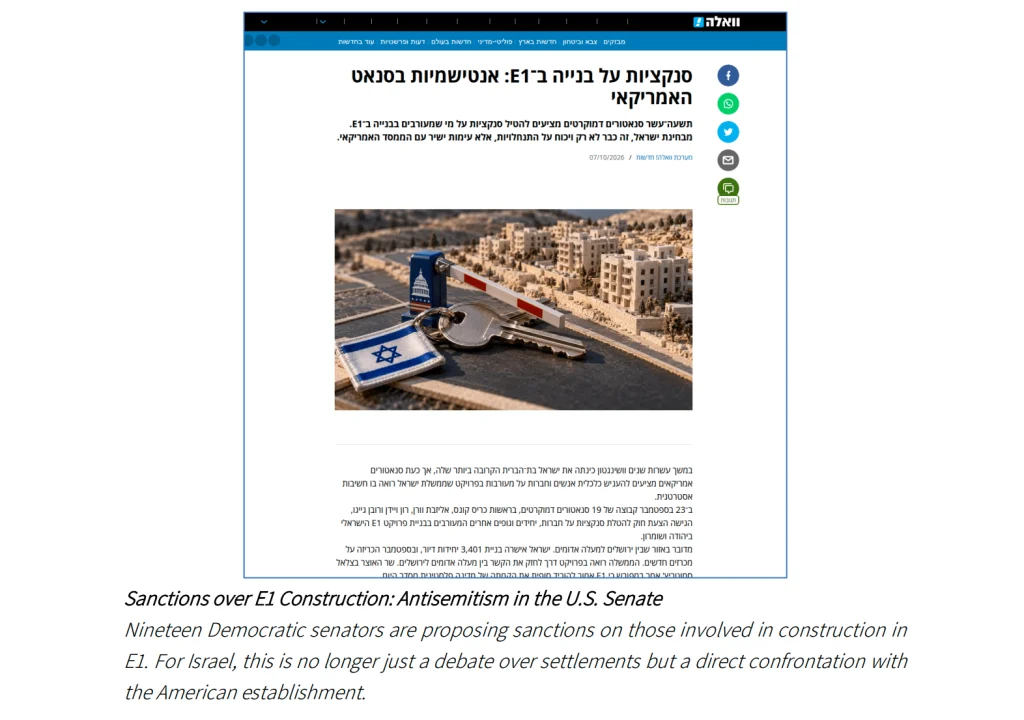
Russian threat actors revived the Doppelganger campaign in August 2026 to target voters ahead of Israel’s October 27 elections. Through a spoofed news portal, the Doppelganger campaign in Israel published at least 76 fake articles backed by 66 redirect domains. Furthermore, researchers warn that the operation aims to divide society, weaken trust in institutions, and poison artificial intelligence models.
What Happened in the Operation
Between May and October 2026, analysts tracked a renewed wave of fake Hebrew news stories targeting Israeli readers. According to a report on the Doppelganger Russian influence campaign in Israel by ClearSky Cyber Security, the actors built a counterfeit site at walla.ist to mimic the legitimate Walla news portal. Specifically, the operators published around 10 fabricated articles per week using automated social media accounts on X.
Initially, the operation paused on June 2, 2026, just one week after EU DisinfoLab reported the May 27 arrest of an international fraud network leader in the Netherlands. However, after two months of silence, the Doppelganger campaign resumed on August 6, 2026, with a new central server and high publication volume. “The campaign’s resurgence since August 2026 may stem from a Russian intent to influence Israeli public opinion ahead of the elections scheduled for October 27, as Russia has done in election campaigns in other countries,” ClearSky researchers stated.
Shifting Narratives and Redirect Chains
Rather than inventing entirely false events, the writers distort real public debates to stir fear and isolation. “The campaign is effective when it takes issues that already concern the public and frames them to deepen fear, distrust and a sense of isolation,” the report noted. Across the 76 documented articles, 28% claimed that Turkey is preparing for war against Israel, while 26% argued that the United States is abandoning Israel. Additionally, another 17% focused on brain drain and emigration, and 16% highlighted economic collapse and rising living costs.
To hide their tracks, the operators use a multi-step redirect chain. When a user clicks a link on X, the browser passes through an initial disposable domain, runs obfuscated JavaScript, and hits a central root server before loading walla.ist. Moreover, geofencing rules ensure that only users located inside the target country can view the spoofed articles. Over the past five months, the attackers rotated their root domains from pvolp.pro and dwerp.pro to Awlessx.pro, while cycling through 66 unique redirect domains.
Who Is Behind the Activity
ClearSky attributes the Doppelganger campaign to Russian operators with high confidence based on technical indicators and historical law enforcement actions. Previously, in September 2024, the U.S. Department of Justice seized 32 campaign domains and named Russian firms Social Design Agency, Structura National Technology, and ANO Dialog as the primary operators. Similarly, an August 2026 report by Meta noted that the network had split into smaller sub-operations targeting Hungary, France, and Germany.
In October 2026, ClearSky uncovered a major operational change that exposed the group’s hosting provider. Instead of hiding behind a Cloudflare-protected root domain, the actors switched to bare IP addresses, including 87.199.201.161 and 89.124.67.27. According to WHOIS records, these IP addresses belong to vdsina.com, a virtual private server provider registered in Dubai whose parent company, vdsina.ru, is based in Russia. “This finding links the campaign’s active infrastructure directly to a Russian company,” ClearSky explained.
Impact and AI Poisoning Scale
Beyond targeting Israeli voters, the exact same infrastructure supports parallel influence operations across Europe. For example, ClearSky and Ukrainian media outlet Babel found that the root domain Awlessx.pro also redirected traffic to unian.st and obozrevatel.st, which spoofed Ukrainian news sites. Meanwhile, investigations by The Guardian and Threadlings revealed that the Doppelganger campaign floods fake portals to manipulate large language models.
“The goal is for search engine and language model crawlers to scan the content, so that chatbots present it to users as fact,” ClearSky researchers wrote. Because automated web crawlers index these spoofed sites, the operation does not need high social media engagement to succeed. Instead, the false articles enter AI training pipelines and corrupt chatbot responses over the long term.
How Readers and Organizations Can Stay Protected
Because the Doppelganger campaign in Israel relies on lookalike domains and automated bot networks, defenders and citizens must verify online sources carefully. First, network administrators should block known root servers, including Awlessx.pro, dwerp.pro, pvolp.pro, 87.199.201.161, and 89.124.67.27, along with the walla.ist domain. Second, social media users should watch for auto-generated X handles that combine English names with random trailing letters, such as KaylaBloodvk or JulietLumkq. Finally, AI developers and search engine operators must filter out known spoofed domains from their web crawlers to prevent disinformation from polluting language models.
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
