 Do Son
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
COLDRIVER

Sekoia exposed Russian Calisto APT (FSB-linked) targeting RSF and NGOs with spear-phishing. The attack uses a custom AiTM kit and a "missing file" lure to steal credentials and 2FA codes.

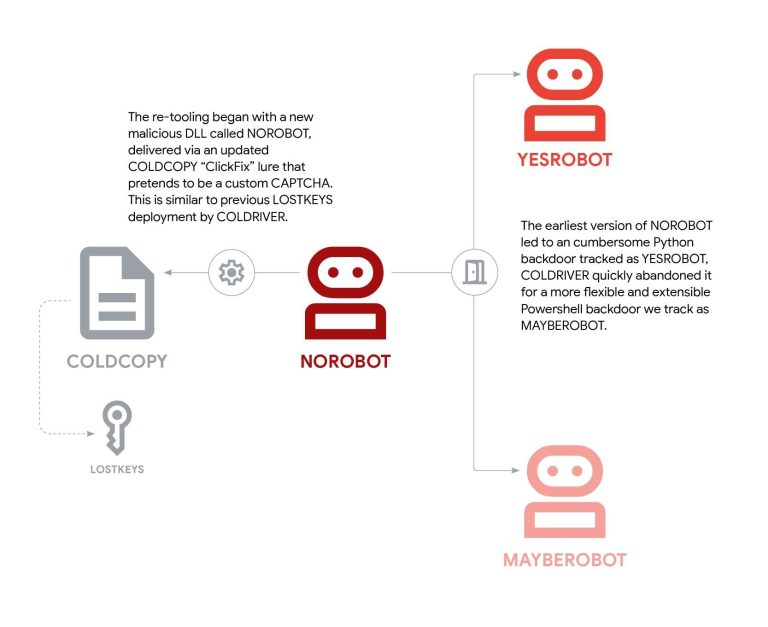
Google exposed Russia's COLDRIVER APT deploying a new "ROBOT" malware family (NOROBOT, YESROBOT) just 5 days after its LOSTKEYS tool was disclosed. The multi-stage malware uses a ClickFix lure.

Russia-linked APT COLDRIVER is using a new multi-stage malware campaign (BAITSWITCH/SIMPLEFIX) with a ClickFix lure to target journalists and activists for espionage.
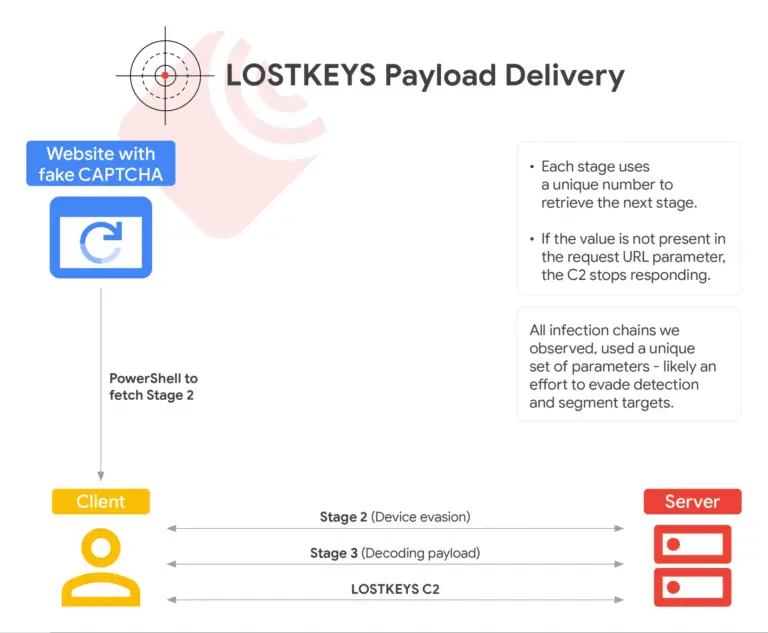
Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.

Justice Department announcement: 41 internet domains seized in cyber fraud and espionage linked to Russian intelligence agents.

SPICA backdoor represents a significant advancement in COLDRIVER's capabilities, marking its first foray into custom malware development