 Do Son
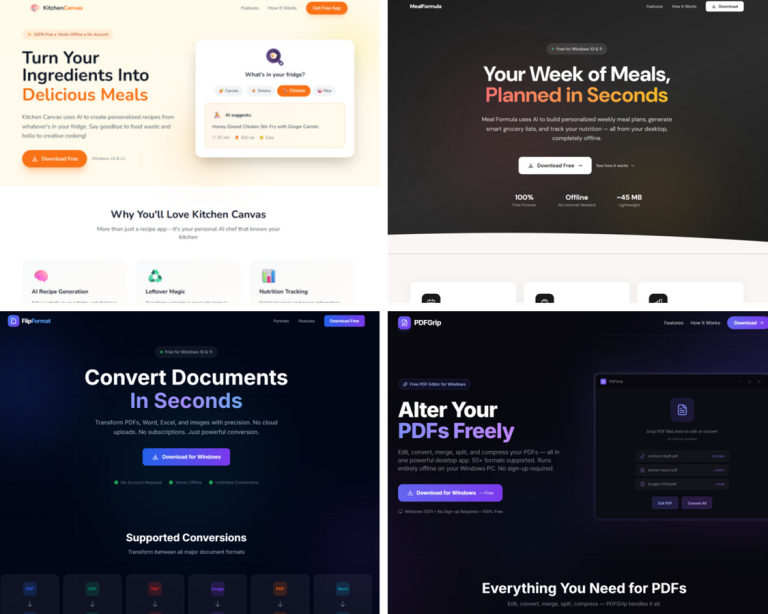
G DATA details Projextor, an Electron malware hidden in working PDF and recipe apps that runs injected scripts and captures the desktop.
G DATA
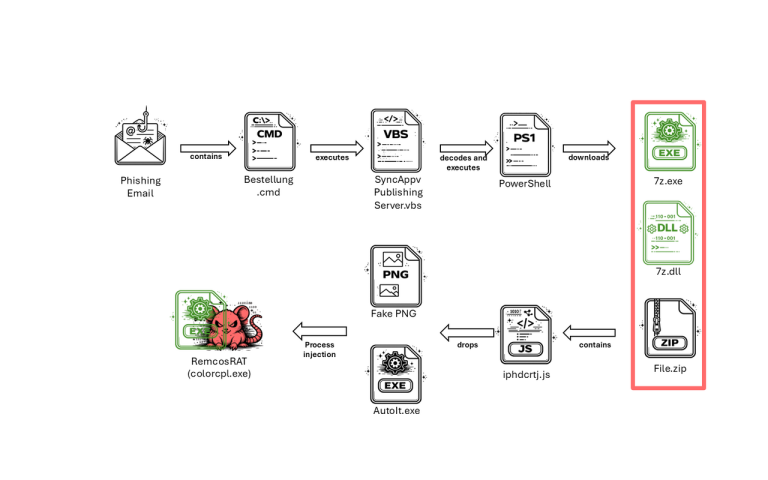
G Data uncovers a new Remcos RAT variant using DonutLoader shellcode and trusted LOLBins to bypass Windows security filters.
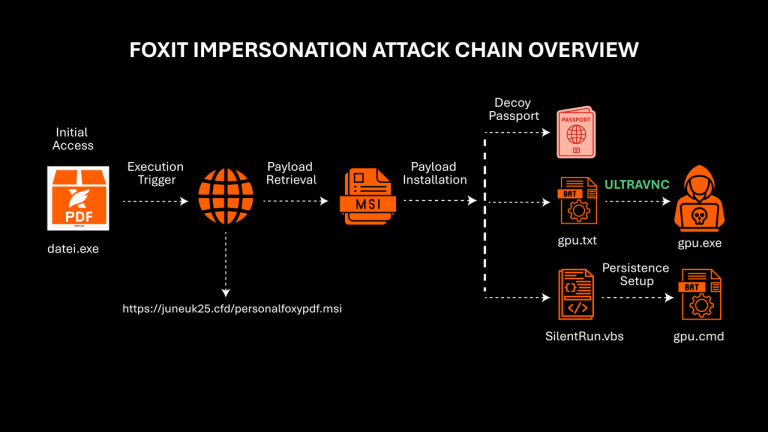
G DATA warns Foxit PDF users of a global malware campaign using fake installers and Danish passport decoys to deploy hidden UltraVNC remote access tools.
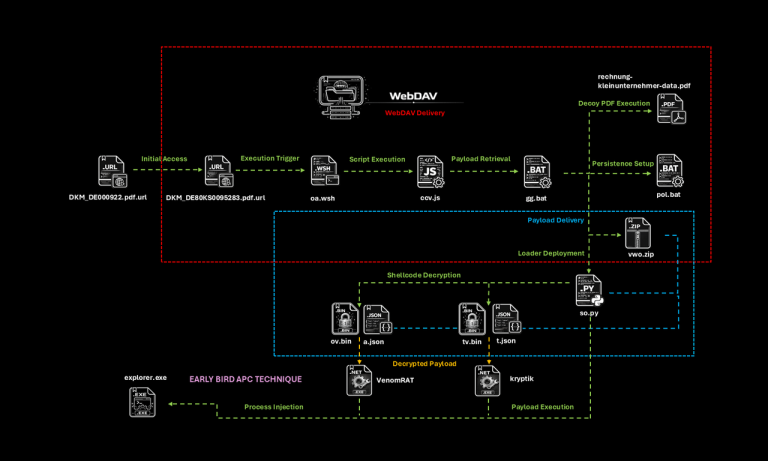
G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.

G DATA exposed Arkanix, a fast-evolving C++ stealer. Its premium version uses process injection and Chrome Elevator to bypass Chrome App-Bound Encryption (ABE) and steal crypto wallets and Wi-Fi passwords.

A Steam game, BlockBlasters, was compromised with malware in an update, which is stealing crypto and credentials from unsuspecting gamers.
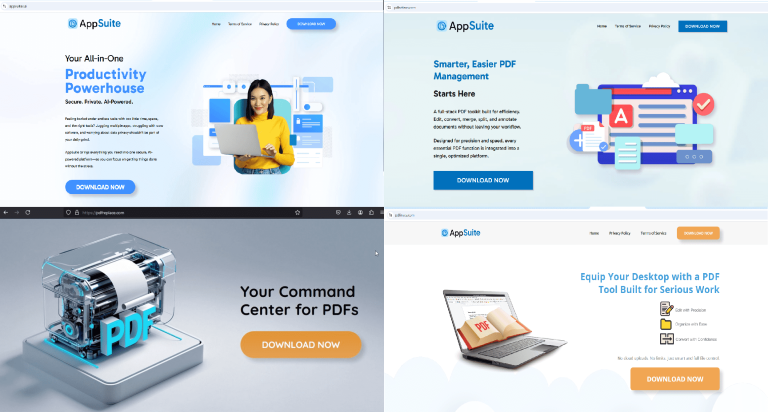
A new report reveals that the AppSuite PDF Editor is a Trojan horse that functions as a backdoor. Its developers even submitted it to AV vendors to get it whitelisted.

XMRig cryptojacking is surging, leveraging LOLBAS techniques, PowerShell, and Scheduled Tasks to mine Monero undetected, with a 45% rally in XMR price driving the attacks.

Hackers are weaponizing legitimately signed ConnectWise ScreenConnect installers by using Authenticode stuffing to deploy malware and fake updates, leveraging social engineering.

Chihuahua Stealer uses stealthy PowerShell loaders, CNG AES-GCM encryption, and .NET memory injection to exfiltrate browser and crypto wallet data.