 Do Son
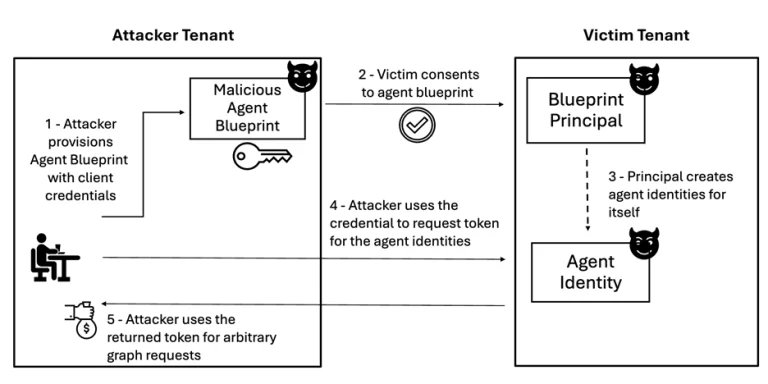
Proofpoint researchers detailed the BluePhishing attack Entra Agent ID technique, showing how malicious AI agent blueprints enable OAuth consent abuse.
OAuth Phishing
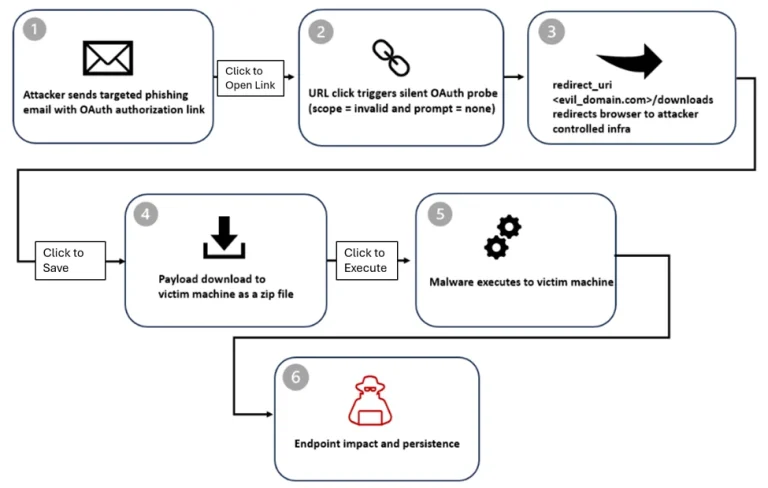
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.

Volexity exposed Russian APT UTA0355 using fake security conference sites and WhatsApp support to trick victims. The attacks steal Microsoft 365 OAuth and Device Code tokens for persistent access.

Volexity uncovers Russian threat actors abusing Microsoft 365 OAuth flows via phishing, impersonation, and device registration to access email accounts.