
 Do Son
Librarian Ghouls APT launches a new cyber-espionage and cryptojacking campaign targeting Russia and CIS, using legitimate tools for stealth.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

UNC6040 is using sophisticated vishing to breach Salesforce, tricking employees into granting access, exfiltrating data, and then pivoting to other cloud platforms.

Sophos X-Ops found a backdoored Sakura RAT targeting hackers and cheaters, spreading info-stealers via hidden scripts in open-source projects.

IBM X-Force warns of a new phishing campaign by Hive0131 targeting Colombian users with DCRat malware via fake legal notices.

Sysdig uncovers a campaign exploiting misconfigured Open WebUI instances to deploy AI-assisted cryptominers and infostealers, showcasing new threat vectors.

Microsoft, Google, and major cybersecurity firms are collaborating to unify hacker group naming, aiming for clearer threat intelligence across the industry.

BitoPro confirms $11.5M hot wallet cyberattack after investigator @zachxbt exposed the theft. User funds are safe, but initial silence raises concerns.

Haozi, a Chinese Phishing-as-a-Service platform, is back, offering no-code phishing kits and full support. Learn how this service enables easy cybercrime.

Netskope reveals a surge in phishing on Glitch, abusing the platform to bypass MFA and steal credentials, mainly targeting Navy Federal Credit Union members.

A sophisticated malware campaign targets Korean Internet cafés with Gh0st RAT and CoinMiner, hijacking systems for crypto mining. ASEC urges immediate action.

Intrinsec exposes BtHoster, a bulletproof hosting provider behind widespread scanning and malware, revealing its network of shell companies and evasion tactics.

The DOJ, with international partners, seized four domains providing crypting services to cybercriminals, hindering malware attacks in a global operation.
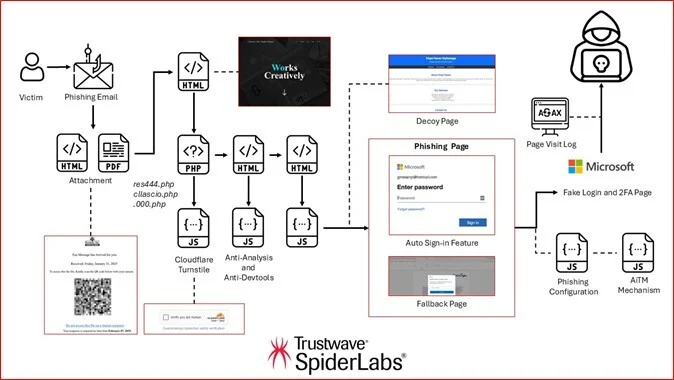
Trustwave uncovers Dadsec and Tycoon2FA, new Phishing-as-a-Service kits bypassing MFA to target Microsoft 365 users with advanced AiTM tactics.

A stealthy spear-phishing campaign uses fake Rothschild job offers to trick finance execs into installing NetBird RAT, gaining remote access.

Apple's latest report reveals it thwarted over $2 billion in fraudulent App Store transactions in 2024, blocking millions of malicious accounts and app submissions.

A stealthy campaign is persistently hacking ASUS routers via undocumented bypasses and CVE-2023-39780, building a backdoor network without malware.

A new campaign by UNC6032 uses fake AI video generator sites and social media ads to distribute a malware cocktail including STARKVEIL.

Attackers compromised an MSP's RMM tool (SimpleHelp) to deploy DragonForce ransomware across customer environments.

Iranian national Sina Gholinejad pleaded guilty for his role in the Robbinhood ransomware attacks targeting U.S. cities like Baltimore.

Mimo (Hezb) is exploiting an unauthenticated RCE (CVE-2025-32432) in Craft CMS to deploy webshells, cryptominers, and proxyware. Patch now!

The alleged architect of the Qakbot malware empire, Rustam Rafailevich Gallyamov, has been indicted, facing charges and a $24M crypto seizure.

Threat actors are installing legitimate DB client tools like DBeaver and Navicat on compromised systems to covertly steal sensitive database information.